> ## Documentation Index
> Fetch the complete documentation index at: https://docs.airmdr.com/llms.txt
> Use this file to discover all available pages before exploring further.
# Confluence
> The Confluence integration enables AirMDR to retrieve and investigate information from your Atlassian Confluence Cloud environment directly within AirMDR, reducing the need to switch between applications.
The Confluence integration enables AirMDR to:
* Retrieve pages, blog posts, comments, tasks, and attachment metadata.
* Search content and identify related pages, spaces, labels, and users.
* Review space permissions and role assignments during access investigations.
* Retrieve page history and hierarchy to understand content changes and relationships.
| Component | Compatibility |
| - | - |
| Confluence deployment | Confluence Cloud. The supplied connection configuration uses Atlassian Cloud authentication. |
| REST APIs | Confluence REST API v2 for supported resources, with v1 endpoints for operations such as CQL search and current-user lookup. |
| Authentication | Atlassian account email and API token, with or without scopes. |
| Space role assignments | Available only on Confluence sites that support role-based access control. |
| Confluence Server or Data Center | Outside the scope of this guide; compatibility is not established by the supplied configuration. |
**Authentication method**
AirMDR authenticates using **HTTP Basic authentication** with:
* **Email:** The email address of the Atlassian account that owns the token.
* **API Token:** A token created for that account.
Select the connection configuration that matches your token:
| Token type | Site URL | Cloud ID | API destination |
| :- | :- | :- | :- |
| **API token with scopes — recommended** | Optional when Cloud ID is provided; useful for identifying the site. | Required. | `https://api.atlassian.com/ex/confluence/{cloudId}` |
| **API token without scopes** | Required. | Leave blank. | `https://your-domain.atlassian.net` |
Scoped tokens must use Atlassian’s API gateway. These credential requirements also match the supplied AirMDR connection screenshots.
**Minimum roles and permissions**
| Activity | Minimum role or access |
| :- | :- |
| Create a token for your own Atlassian account | Account owner, subject to organizational token policies. |
| Retrieve Confluence content | Authenticated Confluence user with site access and permission to view the required space and content. |
| Retrieve space permission assignments | Permission to view the target space. |
| Retrieve space role assignments | Permission to view the target space; the site must support role-based access control. |
| Grant the integration account access | An administrator authorized to manage the relevant app, space, or content permissions. |
| Configure the AirMDR connection | An AirMDR role authorized to manage integration connections. |
A site or organization administrator role is **not a blanket requirement** for the listed read operations. Atlassian documents View access for retrieving space permissions and role assignments.
For an integration that only retrieves data, start with a read-only role such as **Viewer**, then verify that it permits every required AirMDR operation. Published Orca connector instructions use Viewer for read access; this does not establish the minimum role for every AirMDR skill.
| Requirement | Access guidance |
| :- | :- |
| Create the token | Use an account authorized to manage API tokens |
| Retrieve information | Grant the read permissions required by the selected skills |
| Change information | Grant the specific write permissions only if an enabled skill requires them |
| Limit accessible resources | Restrict the token to the required accounts, business units, or other available scope options |
Use a dedicated integration token. Avoid granting administrator-level access solely to resolve a connection error.
## Pre-requisites
>
> An active Atlassian account with access to the required Confluence Cloud site.
>
>
>
> Permission to create API tokens under your organization’s Atlassian policies.
>
## Setup Steps
1. Open your Confluence Cloud site.
2. Sign in using the account that will own the AirMDR API token.
3. Open each space that AirMDR must access.
4. Open a representative page in each space.
5. Confirm that the account can view the required content.
6. If access is missing, ask the relevant administrator to grant the required permissions.
A valid token can authenticate successfully while individual skills fail because the account cannot access their target content.
The email is an existing account identifier; you do not generate it.
1. In Confluence, select your profile avatar.
2. Select **Account settings**.
3. Open **Email**.
4. Copy the email address associated with the account.
5. Use this address in the AirMDR **Email** field.
You can also open [Atlassian account settings](https://id.atlassian.com/manage-profile) directly.
\*\*Example: \*\*`airmdr-confluence@example.com`
Atlassian documents the navigation path through the avatar, Account settings, and Email.
Use the email of the account that creates the token.
Choose one of the following methods.
**Option A: Create an API token with scopes**
1. Open [Atlassian API tokens](https://id.atlassian.com/manage-profile/security/api-tokens).
2. Select **Create API token with scopes**.
3. Enter a descriptive name, such as `AirMDR-Confluence-ReadOnly`.
4. Select an expiration date.
5. Select **Confluence** as the app.
6. Select the scopes listed in **Section 3.3**.
7. Select **Create**.
8. Copy the token into an approved password manager.
**Option B: Create an API token without scopes**
1. Open the same API tokens page.
2. Select **Create API token**.
3. Enter a descriptive name and expiration date.
4. Select **Create**.
5. Copy the token into an approved password manager.
Atlassian permits token lifetimes of **1–365 days**. The token value cannot be retrieved after the creation screen is closed.
If prompted, complete Atlassian’s identity verification before creating the token.
**The Confluence API token may be visible only once.**
**If it is lost, generate a new token and update the AirMDR integration.**
**Do not include the token in screenshots, email, chat, Jira tickets, or documentation examples.**
1. Return to your Confluence site.
2. Open the Confluence home page or any page within that site.
3. Check the browser address bar.
4. Copy the scheme and hostname.
5. Remove `/wiki` and any remaining page path.
**Example:**
| Browser URL | Site URL to enter in AirMDR |
| :- | :- |
| `https://example.atlassian.net/wiki/home` | `https://example.atlassian.net` |
| `https://example.atlassian.net/wiki/spaces/SEC/pages/123456789` | `https://example.atlassian.net` |
The supplied AirMDR field guidance accepts the site root and ignores paths after the hostname. Entering the root URL keeps the configuration clear.
Complete this step when using a **scoped API token**.
**Method A: Retrieve it in your browser**
1. Open a new browser tab.
2. Enter the following address, replacing `your-domain` with your site hostname:
```text theme={null}
https://your-domain.atlassian.net/_edge/tenant_info
```
3. Press **Enter**.
4. Locate the `cloudId` value in the response:
```text theme={null}
{
"cloudId": "11111111-2222-3333-4444-555555555555"
}
```
5. Copy only the value, excluding the quotation marks.
6. Paste it into the AirMDR **Cloud ID** field.
**Method B: Retrieve it through the administration UI**
This method requires access to Atlassian Administration.
1. Open [Atlassian Administration](https://admin.atlassian.com/).
2. Select the organization that owns your Confluence site.
3. Navigate to **Apps → Sites**.
4. Select the required site.
5. Check the browser address bar for a URL containing:
```text theme={null}
https://admin.atlassian.com/s//...
```
6. Copy the identifier immediately after `/s/`.
Atlassian documents both methods. The **Cloud ID differs from the Organization ID**; ensure it belongs to the intended Confluence site.
### Confluence Credential Reference Table
| AirMDR field | Required | Description | Where to obtain it |
| :- | :- | :- | :- |
| **Email** | Yes | Email of the Atlassian account that owns the API token. | Atlassian **Account settings → Email**. |
| **API Token** | Yes | Token used to authenticate Confluence API requests. | Atlassian **Account settings → Security → API tokens**. |
| **Site URL** | Required for an unscoped token | Root URL of your Confluence Cloud site, such as `https://example.atlassian.net`. | Browser address bar while viewing your Confluence site. |
| **Cloud ID** | Required for a scoped token | Unique identifier of the Atlassian Cloud site. | The site’s `/_edge/tenant_info` endpoint or Atlassian Administration. |
### Validate Connectivity
Use this when troubleshooting credentials outside AirMDR.
Set the account email: `ATLASSIAN_EMAIL='airmdr-confluence@example.com'`
For a **scoped token**, set:
```text theme={null}
CONFLUENCE_BASE='https://api.atlassian.com/ex/confluence/11111111-2222-3333-4444-555555555555'
```
For an **unscoped token**, set:
```text theme={null}
CONFLUENCE_BASE='https://example.atlassian.net'
```
Check the current user:
```text theme={null}
curl --request GET \
--user "$ATLASSIAN_EMAIL" \
--header 'Accept: application/json' \
--write-out '\nHTTP status: %{http_code}\n' \
"$CONFLUENCE_BASE/wiki/rest/api/user/current"
```
When curl prompts for a password, paste the **API token**.
Confirm that the response identifies the expected account. A successful HTTP response alone is insufficient if the result represents anonymous access.
The current-user endpoint requires Confluence site access and an appropriate user-read scope for scoped authentication.
Then test page access:
```text theme={null}
curl --request GET \
--user "$ATLASSIAN_EMAIL" \
--header 'Accept: application/json' \
--write-out '\nHTTP status: %{http_code}\n' \
"$CONFLUENCE_BASE/wiki/api/v2/pages/123456789?body-format=storage"
```
Replace the example page ID with a page the connected account can view. Atlassian documents page access and the `read:page:confluence` scope for these read operations.
## Configure Confluence in AirMDR Integrations Dashboard
1. Navigate to [AirMDR](https://app.airmdr.com/auth/login), provide the credentials and click **Login**
2. Navigate to the AirMDR Integrations Dashboard in the left navigation pane and select **ADMIN → Integrations**.
3. Use the search option, enter the keyword "**Confluence**", select the **Connections** tab, and click **+ New Connection** button.
4. Use the following values in the AirMDR integration configuration screen:
| Field | Value to enter |
| :- | :- |
| **Instance** | A unique name, such as `Example-Confluence`. |
| **Organization** | The AirMDR organization that owns the connection. |
| **Description** | A brief description, such as `Read-only access to security documentation`. |
| **Email** | The Atlassian account email from Step 2. |
| **API Token** | The token from Step 3. |
| **Site URL** | The root URL from Step 4; required for an unscoped token. |
| **Cloud ID** | The value from Step 5 for a scoped token; leave blank for an unscoped token. |
1. In **Remote Agent**, select an AirMDR Remote Agent when Confluence API requests must run through an approved network route. Ensure the selected agent can resolve and reach `api.atlassian.com` for scoped API tokens, or your Confluence site hostname for unscoped API tokens, over HTTPS. For direct connectivity from AirMDR, leave this field unselected.
2. In **Expiry**, select the Atlassian API token’s expiration date or an earlier date required by your organization’s credential-rotation policy.
Expiry controls credential validity in AirMDR. It does not automatically rotate, extend, or revoke the token in Atlassian. Before expiry, create a replacement token, update **API Token** and **Expiry**, save and validate the connection, and then revoke the previous token when it is no longer required.
5. Click **Save**.
## Skills provided by this Integration
| Skill | Purpose | Access type | Required permission |
| :- | :- | :- | :- |
| **Resolve Confluence IDs** | Resolves space keys and names, page titles, labels, and person names into identifiers required by other skills. | Read-only | Access to the resources being resolved. Scopes depend on the lookup: `read:space:confluence`, `read:page:confluence`, `read:label:confluence`, and applicable content-search or user-read scopes. |
| **Search Confluence Users** | Searches users by name or retrieves user information by Atlassian account ID. | Read-only | Confluence site access, subject to profile visibility restrictions. User search: `read:content-details:confluence`. User lookup: `read:confluence-user` or the documented granular alternative, `read:content-details:confluence`. |
| **Search Confluence Content** | Finds content using CQL, full-text search, partial-title matching, and supported filters. | Read-only | Permission to view matching content. Scope: `search:confluence` or the documented granular alternative, `read:content-details:confluence`. |
| Skill | Purpose | Access type | Required permission |
| :- | :- | :- | :- |
| **Get Confluence Spaces** | Retrieves space details or lists spaces using supported filters. | Read-only | Permission to view the target spaces. Scope: `read:space:confluence`. Additional lookup scopes may apply when resolving filters. |
| **Get Confluence Pages** | Retrieves page content or lists pages using supported filters. | Read-only | Permission to view the target page and its space. Scope: `read:page:confluence`. Label resolution may also require `read:label:confluence`. |
| **Get Confluence Blog Posts** | Retrieves blog-post content or lists posts using supported filters. | Read-only | Permission to view the target blog post and its space. Scope: `read:page:confluence`. |
| **Get Confluence Attachments** | Retrieves attachment metadata, including associated content and file details. Does not download file content. | Read-only | Permission to view the attachment’s containing content. Scope: `read:attachment:confluence`. |
| Skill | Purpose | Access type | Required permission |
| :- | :- | :- | :- |
| **Get Confluence Page Hierarchy** | Retrieves direct children, descendants to a selected depth, or ancestors of a page. | Read-only | Confluence site access and permission to view the applicable child or descendant content. Scopes: `read:page:confluence` for child pages; `read:hierarchical-content:confluence` for descendants and applicable child-content operations; `read:content.metadata:confluence` for ancestors. |
| **Get Confluence Page Versions** | Retrieves page version history or details of a selected version, including author, timestamp, and change message. | Read-only | Permission to view the target page and its space. Scope: `read:page:confluence`. |
| Skill | Purpose | Access type | Required permission |
| :- | :- | :- | :- |
| **Get Confluence Comments** | Retrieves footer comments, inline comments, and optional reply threads from a page or blog post. | Read-only | Permission to view the containing page or blog post and its space. Scope: `read:comment:confluence`. |
| **Get Confluence Labels** | Retrieves labels associated with content, spaces, or the site. | Read-only | Access to the relevant content or space. Scopes: `read:label:confluence` for site-wide labels; `read:page:confluence` for page or blog-post labels; `read:space:confluence` for space-related labels. |
| **Get Confluence Tasks** | Retrieves action items by ID or supported filters, including status, assignee, content, and date ranges. | Read-only | Permission to view the containing page or blog post and its space. Scope: `read:task:confluence`. |
| Skill | Purpose | Access type | Required permission |
| :- | :- | :- | :- |
| **Get Confluence Space Permissions** | Retrieves permission assignments to identify who can access or perform operations within a space. | Read-only | Permission to view the target space. Scope: `read:space:confluence` for permission assignments. |
| **Get Confluence Space Role Assignments** | Retrieves assigned roles, role names, and associated permissions for a space. | Read-only | Permission to view the target space. Scope: `read:space.permission:confluence`. The site must support role-based access control. |
To view the details of Input Parameters and Output for the respective skills
* Go to [AirMDR → Confluence](https://app.airmdr.com/integrationsv2/54a74d83-62e8-403c-a573-944f48f21437/skills?search=confluence) Integration page.
* Select the **Skills** tab and click on the required listed skills.
### Permissions and Roles by Skill
The following permissions apply to the **Atlassian account connected to AirMDR**. All listed skills perform read-only operations.
**Confluence user** means an authenticated account with permission to access the Confluence site. API scopes apply when using a **scoped API token** and do not override the account’s resource permissions.
| AirMDR skill | Required access | Applicable role | Required permissions |
| :- | :- | :- | :- |
| **Resolve Confluence IDs** | Look up spaces, pages, labels, and users to resolve their identifiers. | Confluence user | Access to the resources being resolved. Scopes depend on the lookup: `read:space:confluence`, `read:page:confluence`, `read:label:confluence`, and applicable search or user-read scopes. |
| **Search Confluence Users** | Search users by name and retrieve information by Atlassian account ID. | Confluence user | Site access, subject to profile visibility restrictions. User search: `read:content-details:confluence`. User lookup: `read:confluence-user` or its documented granular alternative, `read:content-details:confluence`. |
| **Search Confluence Content** | Search content using CQL and supported filters. | Confluence user | Permission to view matching content. Scope: `search:confluence` or its documented granular alternative, `read:content-details:confluence`. |
| **Get Confluence Spaces** | List accessible spaces and retrieve space details. | Confluence user | Permission to view the target spaces. Scope: `read:space:confluence`. |
| **Get Confluence Pages** | Read page bodies and list matching pages. | Confluence user | Permission to view the page and its space. Scope: `read:page:confluence`. Label resolution may additionally require `read:label:confluence`. |
| **Get Confluence Blog Posts** | Read blog-post bodies and list matching posts. | Confluence user | Permission to view the blog post and its space. Scope: `read:page:confluence`. |
| **Get Confluence Attachments** | Read attachment metadata without downloading file content. | Confluence user | Permission to view the attachment’s containing content. Scope: `read:attachment:confluence`. |
| **Get Confluence Page Hierarchy** | Read direct children, descendants, or ancestors of a page. | Confluence user | Site access and permission to view applicable child or descendant content. Scopes depend on the operation: `read:page:confluence`, `read:hierarchical-content:confluence`, or `read:content.metadata:confluence`. |
| **Get Confluence Page Versions** | Read page version history and individual version details. | Confluence user | Permission to view the page and its space. Scope: `read:page:confluence`. |
| **Get Confluence Comments** | Read footer comments, inline comments, and supported reply threads. | Confluence user | Permission to view the containing page or blog post and its space. Scope: `read:comment:confluence`. |
| **Get Confluence Labels** | Read labels associated with content, spaces, or the site. | Confluence user | Access to the relevant content or space. Scope depends on the resource: `read:label:confluence` for site-wide labels, `read:page:confluence`for page or blog-post labels, or `read:space:confluence` for space-related labels. |
| **Get Confluence Tasks** | Read action items and retrieve tasks using supported filters. | Confluence user | Permission to view the containing page or blog post and its space. Scope: `read:task:confluence`. |
| **Get Confluence Space Permissions** | Inspect permission assignments for a space. | Confluence user with View access to the space | Permission to view the target space. Scope: `read:space:confluence`. |
| **Get Confluence Space Role Assignments** | Inspect assigned roles and their associated permissions. | Confluence user with View access to the space | Permission to view the target space. Scope: `read:space.permission:confluence`. Available only on sites supporting role-based access control. |
Organization, site, or space administrator access is not a blanket requirement for these skills. Grant only the access needed for the intended investigations.
## Additional Information
| Symptom | Possible cause | Recovery steps |
| :- | :- | :- |
| **Verify Authentication fails** | Incorrect email/token pair, expired token, or incorrect destination configuration. | Confirm the token owner’s email, token validity, and the Site URL/Cloud ID combination. Save and validate again. |
| **Current-user result represents anonymous access** | Credentials were not accepted even though a response was returned. | Check the email/token pair and request destination. Do not treat anonymous access as successful authentication. |
| **401 Unauthorized** | Invalid, expired, or revoked token; incorrect authentication configuration. | Replace invalid credentials and confirm the token type matches the configured destination. |
| **403 Forbidden** | Missing scope, insufficient account access, or an organizational restriction. | Check the documented scopes and the account’s site, space, and content permissions. |
| **404 Not Found** | Incorrect ID, wrong site, removed resource, or inaccessible content. | Resolve the ID again, confirm the site, and verify access using the same account. |
| **400 Bad Request** | Invalid CQL, unsupported filter, or malformed identifier. | Review the skill inputs and test a simpler query. |
| **429 Too Many Requests** | Atlassian rate limit reached. | Reduce concurrency and request frequency; respect `Retry-After` when provided. |
| **Empty search results** | Restrictive filters, wrong site, or content visibility limits. | Search for known accessible content, simplify filters, and verify the account’s access. |
| **Space role skill unavailable** | The site does not support role-based access control. | Review supported access information using **Get Confluence Space Permissions**. |
| **Connection timeout** | DNS, proxy, firewall, destination, or Remote Agent issue. | Test connectivity from the actual execution environment. |
| **TLS certificate error** | Certificate trust or inspection-proxy issue. | Correct certificate trust configuration and retry with validation enabled. |
| **Results appear incomplete** | Filters or pagination limits. | Review skill limits and available pagination controls. |
**Recovery sequence**
1. Confirm the expected Confluence site.
2. Confirm the token owner’s email.
3. Check token expiration and validity.
4. Verify Site URL and Cloud ID configuration.
5. Validate the current user.
6. Test a known accessible space and page.
7. Check scopes for the failing skill.
8. Check connectivity from the selected execution environment.
9. Retry the affected skill.
**Where to check**
| Location | What to review |
| :- | :- |
| AirMDR Confluence connection | Authentication result and configured connection details. |
| Associated AirMDR playbook execution | Failed skill step, input values, output, and available error details. |
| Atlassian API token list | Token expiration and whether a replacement is required. |
| Confluence access settings | Account, space, and content access relevant to the failed request. |
| Selected Remote Agent, if applicable | Availability, DNS resolution, HTTPS connectivity, and execution errors. |
**Recommended monitoring**
Monitor for:
* Repeated authentication failures.
* Permission errors affecting previously accessible content.
* Rate-limit responses.
* Remote Agent connectivity failures.
* Upcoming token expiration.
* Unexpectedly empty or incomplete results.
**Example log entries**
The following entries are **illustrative troubleshooting examples**, not a verified AirMDR log schema:
```text theme={null}
INFO integration=Confluence operation=verify_authentication result=success
ERROR integration=Confluence operation=get_pages http_status=403
WARN integration=Confluence operation=search_content http_status=429
ERROR integration=Confluence operation=get_tasks result=connection_timeout
```
**Recommended log levels**
Where logging controls are available:
| Level | Recommended use |
| :- | :- |
| **INFO** | Routine execution outcomes. |
| **WARN** | Rate limiting and recoverable failures. |
| **ERROR** | Authentication, authorization, and connectivity failures. |
| **DEBUG** | Temporary troubleshooting with sensitive values redacted. |
Do not log tokens, authorization headers, or complete sensitive document bodies
**✅ Do**
* **Use a dedicated integration account:** Use an organization-managed Atlassian account with a designated owner.
* **Apply least privilege:** Grant access only to the spaces and content required for AirMDR investigations.
* **Use scoped API tokens:** Select the documented read scopes required by the integration.
* **Protect credentials:** Store the API token in an approved password manager and restrict access to AirMDR connection settings.
* **Verify the account and site:** Ensure the email belongs to the token owner and the Cloud ID identifies the intended Confluence site.
* **Maintain secure connectivity:** Use HTTPS with certificate validation enabled. If using a Remote Agent, ensure it can reach the required Atlassian endpoints.
* **Track expiry and rotate tokens:** Set AirMDR **Expiry** no later than the token’s expiration date. Validate replacement credentials before revoking the previous token during routine rotation.
* **Review access periodically:** Reassess account permissions when spaces, playbooks, ownership, or investigation requirements change.
**❌ Don’t**
* **Do not expose tokens:** Never include API tokens or authorization headers in documentation, screenshots, logs, tickets, or messages.
* **Do not grant unnecessary privileges:** Avoid administrator roles, write scopes, or delete scopes for the supplied read-only skills.
* **Do not use the account password:** Enter an Atlassian API token in the **API Token** field.
* **Do not mix credentials:** Avoid pairing one account’s email with another account’s token or using a Cloud ID from a different site.
* **Do not bypass access restrictions:** Do not make restricted content public to resolve an integration permission error.
* **Do not disable certificate validation:** Correct certificate or proxy trust issues before retrying.
* **Do not assume Expiry renews the token:** Updating AirMDR **Expiry** does not extend or replace the Atlassian token.
* **Do not rely only on authentication success:** Test the required skills against representative content to confirm sufficient access.
* 📧 Contact [**AirMDR Support**](mailto:support@airmdr.com) through your designated support channel.
* 🔁 Rotate credentials regularly. Recommended cadence: As per your internal security policy
* 🔄 Replace a token before expiration. Review the connection when:
* The integration account owner changes.
* Spaces or content permissions change.
* The Confluence site changes.
* New skills or playbooks are introduced.
* Token policies change.
* The selected Remote Agent changes.
**Data exchanged**
| Data category | Examples |
| :- | :- |
| Content | Page and blog-post bodies, titles, IDs, and status. |
| Relationships | Space membership, ancestors, children, and descendants. |
| Discussion and action items | Comments, replies, tasks, assignees, and dates. |
| Attachment metadata | File names, media types, sizes, and associated content IDs. |
| History | Version numbers, authors, timestamps, and change messages. |
| Access information | Space permissions, role assignments, and principals. |
| Identity information | Atlassian account IDs and visible profile details. |
The returned information depends on the selected skill and the connected account’s access.
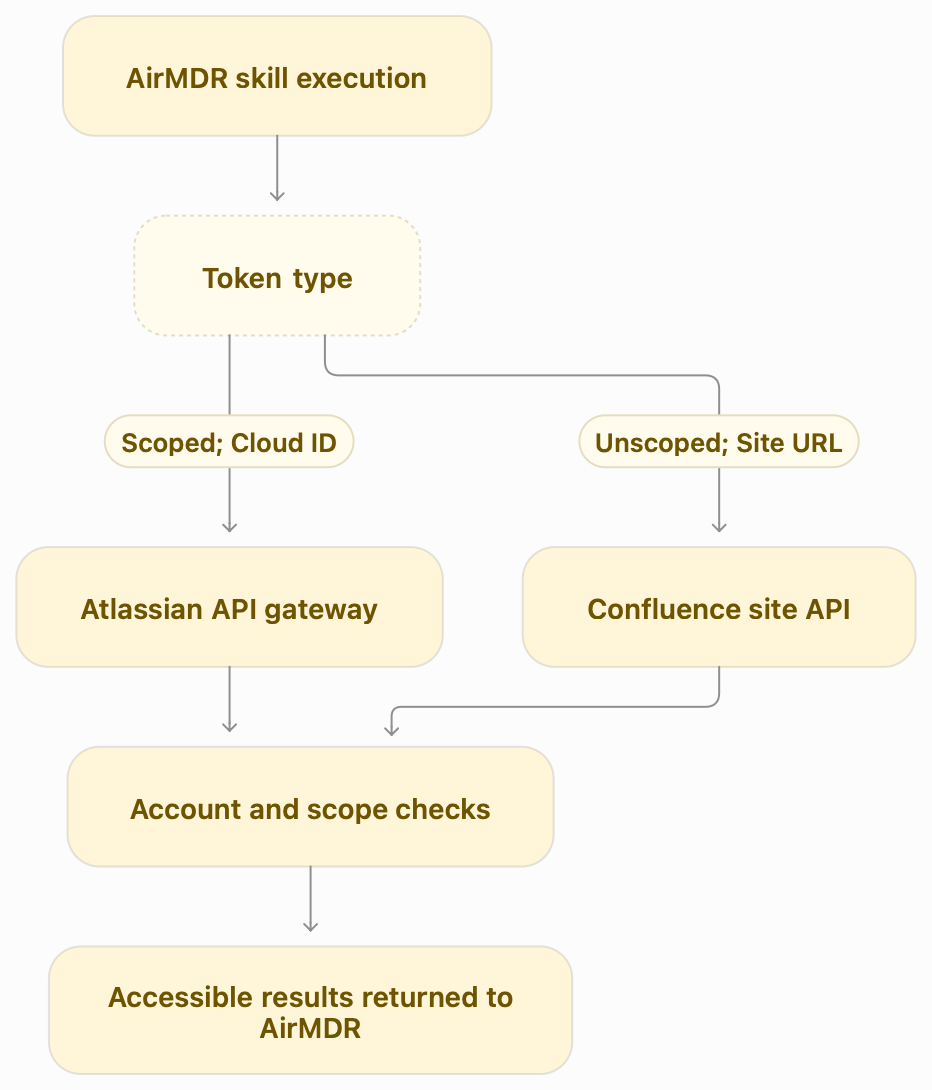
**Authentication and request flow**
When an approved Remote Agent route is used, the selected agent provides the execution path to the appropriate API destination.
 **Ports and endpoints**
| Destination or path | Purpose | Port |
| :- | :- | :- |
| `id.atlassian.com` | Account settings and token management through the browser. | TCP 443 |
| `admin.atlassian.com` | Administrative retrieval of the Cloud ID. | TCP 443 |
| `your-domain.atlassian.net/_edge/tenant_info` | Browser retrieval of the Cloud ID. | TCP 443 |
| `your-domain.atlassian.net/wiki/...` | API requests using an unscoped token. | TCP 443 |
| `api.atlassian.com/ex/confluence/{cloudId}/wiki/...` | API requests using a scoped token. | TCP 443 |
**Common API paths include:**
| Operation | Reference API path |
| :- | :- |
| Current-user verification | `GET /wiki/rest/api/user/current` |
| Content search | `GET /wiki/rest/api/search` |
| User search | `GET /wiki/rest/api/search/user` |
| Pages | `GET /wiki/api/v2/pages` |
| Blog posts | `GET /wiki/api/v2/blogposts` |
| Spaces | `GET /wiki/api/v2/spaces` |
| Space permission assignments | `GET /wiki/api/v2/spaces/{id}/permissions` |
| Space role assignments | `GET /wiki/api/v2/spaces/{id}/role-assignments` |
| Tasks | `GET /wiki/api/v2/tasks` |
These are Atlassian reference paths. An AirMDR skill may call multiple endpoints depending on its inputs.
**Encryption and credential handling**
* Use HTTPS for requests to Atlassian.
* Keep certificate validation enabled.
* Store tokens only in approved credential-management locations.
* Restrict access to connection management and investigation outputs.
* Apply your organization’s retention policy to retrieved content.
Atlassian documents TLS 1.2 or later for customer data in transit over public networks and AES-256 encryption at rest for Confluence Cloud data drives. These statements describe Atlassian’s environment; they do not establish AirMDR’s storage controls.
This documentation is built and hosted on [Mintlify](https://mintlify.com), a developer documentation platform.