Overview
AirMDR integrates with Amazon Web Services (AWS) to investigate security findings, query logs and metrics, retrieve cloud resource context, and automate response actions. The permissions required depend on the skills and workflows your organization uses.- Investigation access: Read security findings, audit events, logs, metrics, and resource information to investigate threats and enrich alerts.
- Query access: Execute Athena queries for historical analysis. This requires access to source data, catalog metadata, and an S3 location where query results are written.
- Write access: Perform response actions, such as archiving GuardDuty findings, updating Security Hub finding status, and uploading or deleting S3 objects.
- Permissions-management access: Revoke IAM role sessions by attaching or updating an inline policy on the specified target role.
Setup at a glance
In a hurry, and GuardDuty plus CloudTrail is all you need? The Use a Script tab does step 1 and Option 1 of step 2 for you, in a single account. Otherwise:- Enable AWS GuardDuty — required for every method.
-
Choose one of the three authentication methods, based on your organization’s requirements. Each method defines its own permissions, so follow only the path you choose:
- Configure AWS in the AirMDR Integrations Dashboard
AWS Setup Prerequisites
AWS Setup Prerequisites
Set up the integration
The connection dialog offers two paths, on the Do it Yourself and Use a Script tabs.- Use a Script — a generated Python script provisions a single account for you in a few minutes. It grants GuardDuty and CloudTrail access only, so it suits a GuardDuty-led deployment rather than full coverage.
- Do it Yourself — the manual steps below. Required for STS role assumption and for an AWS Organization, and the direct route to full skill coverage. (You can also reach full coverage from the script path by widening its policy afterwards.)
Quick setup with the Use a Script tab
AccessDenied. Six of the twenty-four skills work out of the box. Widen the policy afterwards, or follow the manual steps instead, if you need more.- Python 3 and pip. If
pythonon your system is Python 2 or missing, usepython3andpip3in the commands below. - An AWS CLI profile for the target account, defined in
~/.aws/config. If it is an IAM Identity Center (SSO) profile, sign in first withaws sso login --profile <name>— the script fails with an expired-token error otherwise. - Enough privilege on that profile. The script calls
guardduty:ListDetectors,guardduty:CreateDetector,iam:GetPolicy,iam:CreatePolicy,iam:GetUser,iam:CreateUser,iam:ListAttachedUserPolicies,iam:AttachUserPolicyandiam:CreateAccessKey, plusiam:CreateServiceLinkedRolethe first time GuardDuty is enabled in the account. That is close to IAM-administrator privilege — run it from an administrator workstation, not a shared or long-lived host.
- Open Integrations → Amazon Web Services → Connections → + Create, fill in Instance and Description, then select the Use a Script tab.
- Step 1 — Select the script language. Python is the only option.
-
Step 2 — Fill the details and download the script. Both fields are required, and both are written into the script before it downloads:
- SSO Profile That Will Run The Script — the named profile from your local
~/.aws/config. It becomesprofile_namein the script’sboto3.Session. - Region_name — the region this connection queries, e.g.
us-east-1. GuardDuty is enabled in this region only.
- SSO Profile That Will Run The Script — the named profile from your local
-
Step 3 — Run it on the machine holding that profile:
-
Step 4 — Provide the credentials. Copy the Access Key ID and Secret Access Key the script prints into
Access_keyandSecret_key. Both are required on this tab. - Expand Advanced Configuration if you need a Remote Agent or an Expiry date, then click Save and run Authenticate on the connection.
What the script creates
AirMDRSkillsReadOnlyPolicy is the script’s policy. It is a different object from AirMDR-ReadOnlyPolicy, the policy the manual Create IAM policy step builds, and from AirMDRReadOnlyPolicy, the inline policy inside the Option 3 StackSet template.Widening the script’s policy
EditAirMDRSkillsReadOnlyPolicy in IAM → Policies and add the fourteen read actions it is missing:
sts:GetCallerIdentity, logs:DescribeLogGroups, logs:DescribeLogStreams, logs:GetLogEvents, logs:FilterLogEvents, cloudwatch:GetMetricStatistics, securityhub:GetFindings, securityhub:GetFindingsV2, securityhub:GetEnabledStandards, s3:ListAllMyBuckets, s3:ListBucket, s3:GetObject, s3:GetBucketLocation, iam:SimulatePrincipalPolicy.
That unlocks eleven more skills — the CloudWatch, Security Hub read, S3 read and caller-permission ones — bringing the policy level with the read statement in Create IAM policy.
The remaining seven need more than reads: Archive Guardduty Findings, Update AWS SecurityHub Finding Status, Put S3 Object, Delete S3 Objects and Revoke AWS Role Sessions are write actions, Execute AWS Athena Query needs the Athena set, and General AWS Query needs whatever its playbook calls. The callout in Create IAM policy lists the action for each.
Enable AWS GuardDuty
AWS GuardDuty is mandatory for integration with AirMDR because it serves as the primary threat detection engine in your AWS environment and AirMDR relies on GuardDuty findings to perform its core security use cases.
Create IAM policy
Create the AirMDR-ReadOnlyPolicy (Options 1 and 2 only)
Create the AirMDR-ReadOnlyPolicy (Options 1 and 2 only)
Understand the Purpose of AWS Permissions Used by AirMDR
Understand the Purpose of AWS Permissions Used by AirMDR
✅ AmazonEC2ReadOnlyAccess
✅ AmazonEC2ReadOnlyAccess
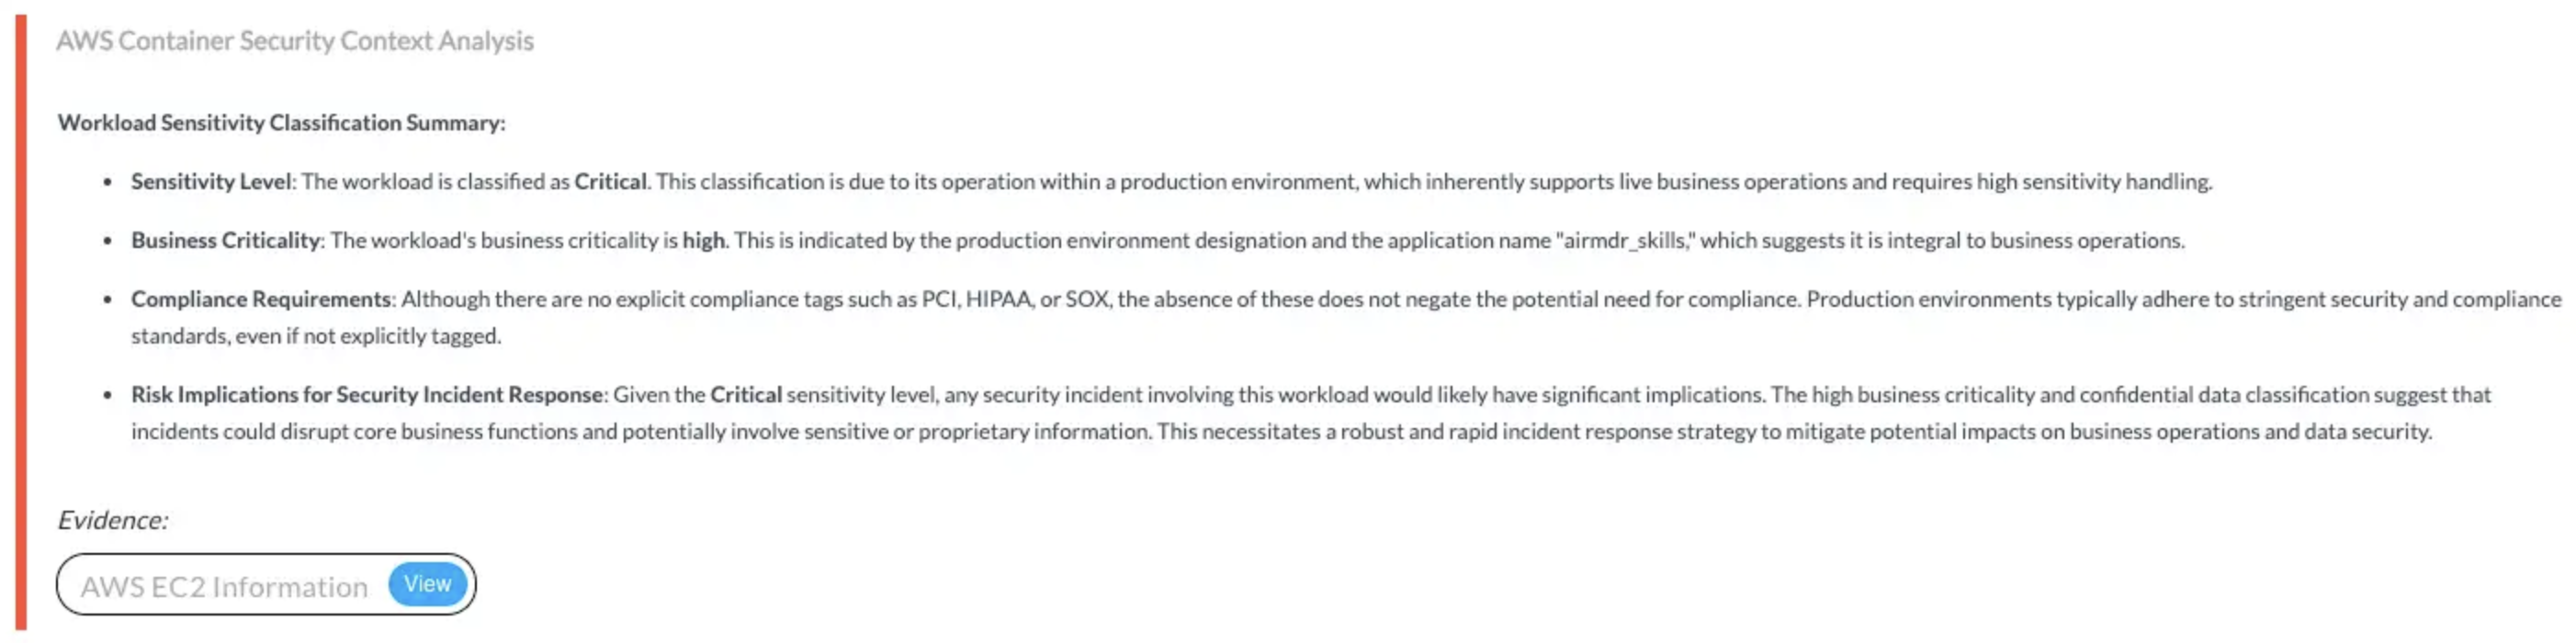
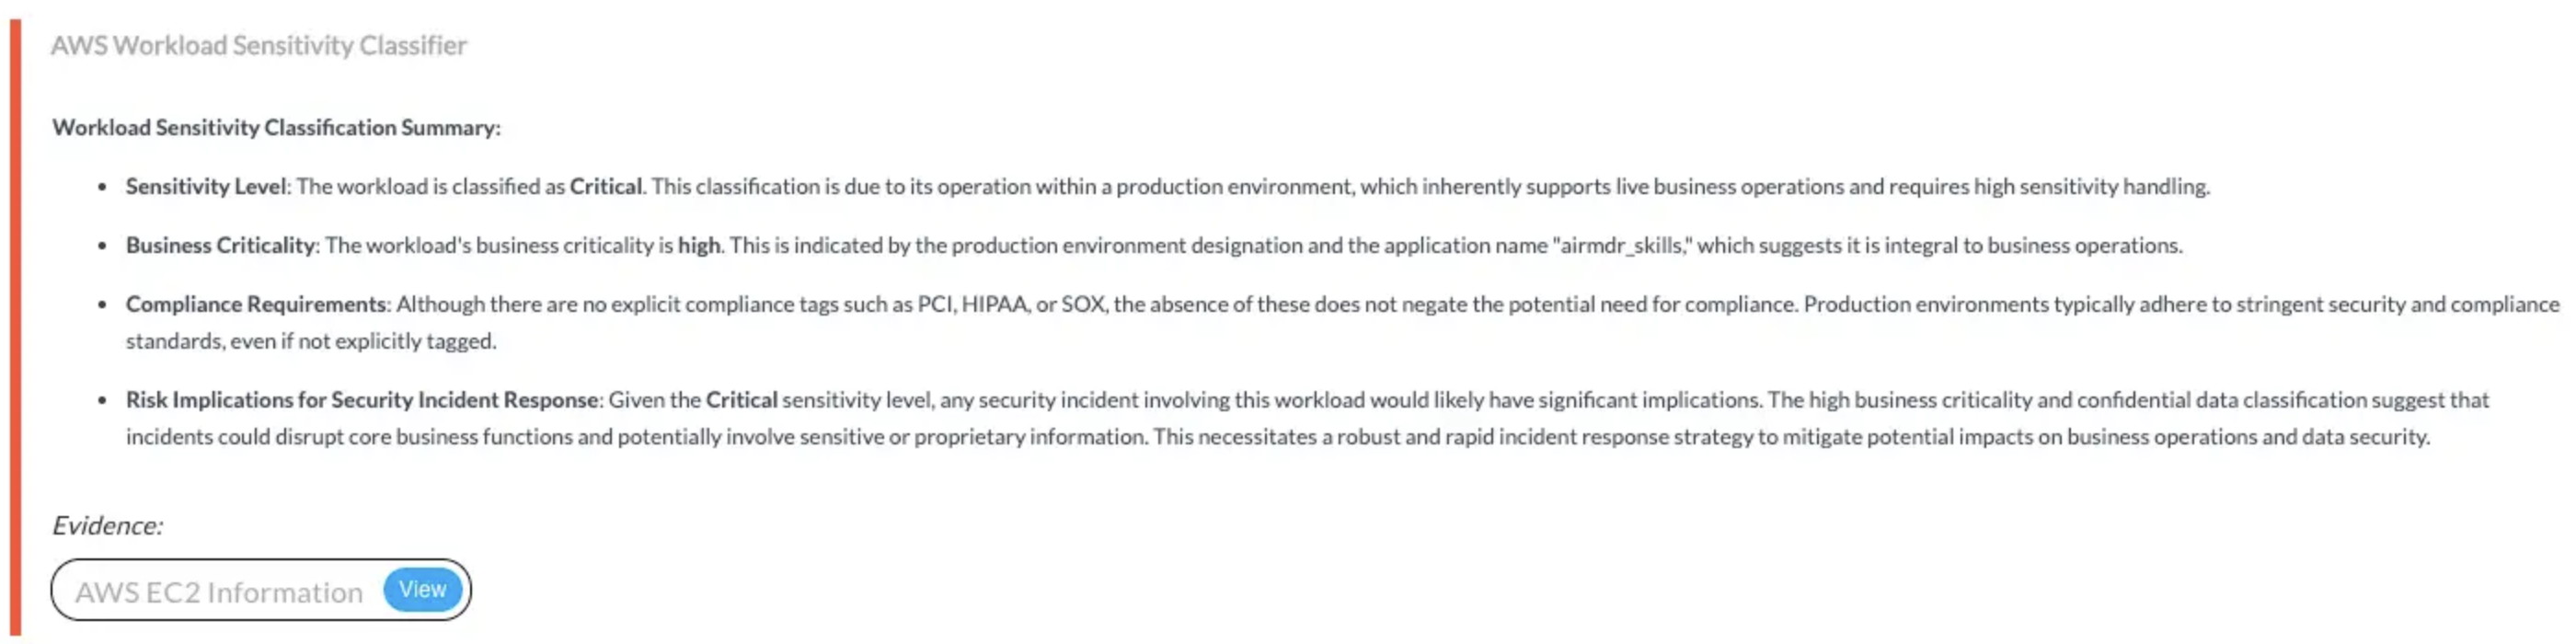
Provides read-only access to EC2 and container metadata, enabling AirMDR to enrich alerts, assess security configurations, classify workloads by risk, and validate container deployment standards.🔸 Input Params Used:
service_name: ec2, method_name: describe_instances🔸 AWS Actions:ec2:DescribeInstances🔸 Skills Used:general_aws_query📎 Findings: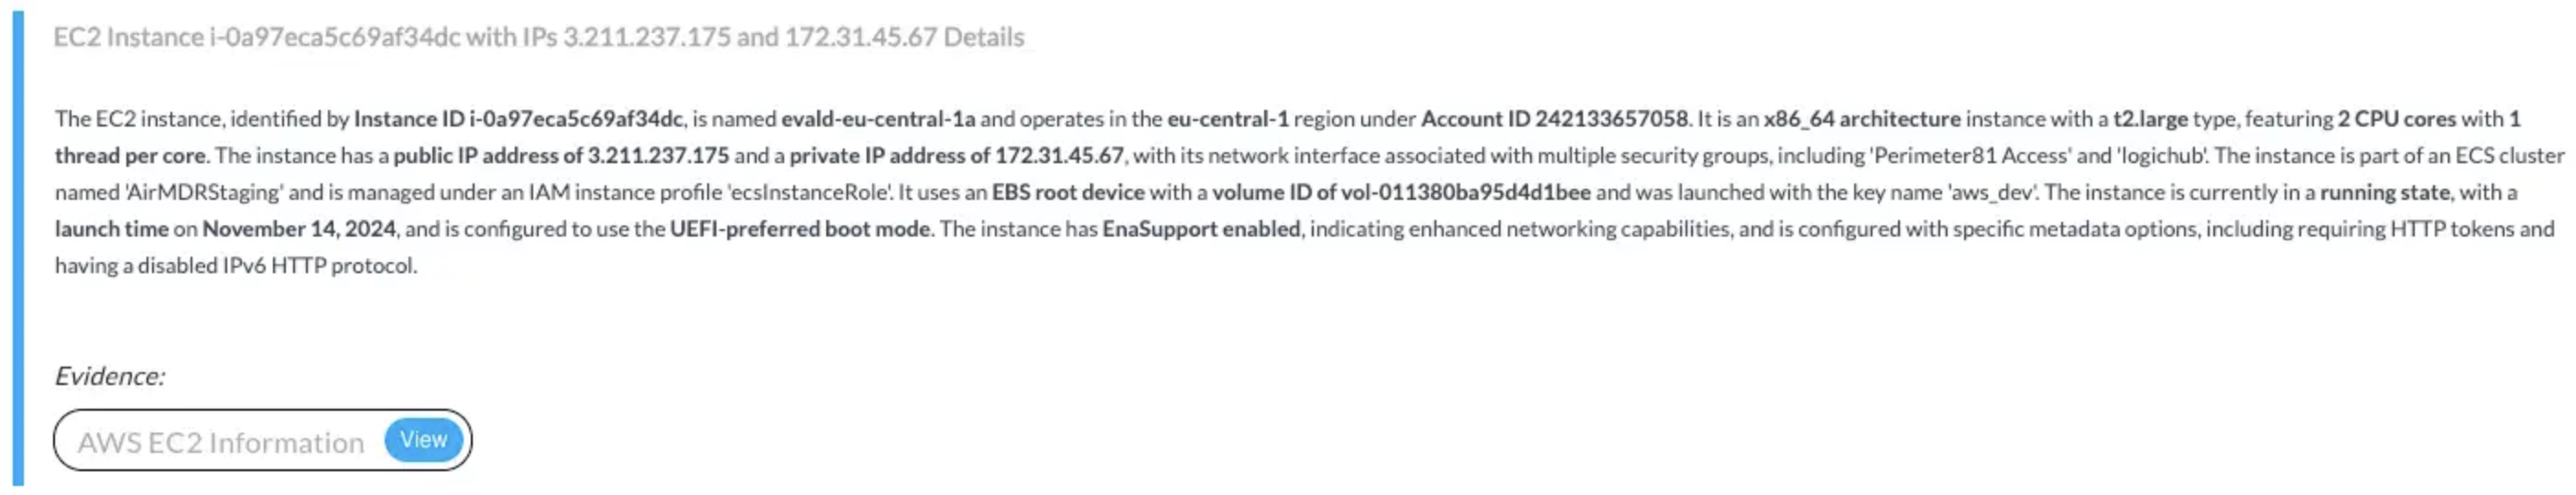
✅ AmazonGuardDutyReadOnlyAccess
✅ AmazonGuardDutyReadOnlyAccess
Enables AirMDR to retrieve and analyze GuardDuty findings for suspicious activity related to S3 buckets and remote IPs, supporting threat pattern detection, anomaly analysis, and automated case enrichment.🔸 AWS Actions:
guardduty:ListFindings, guardduty:ListDetectors, guardduty:GetFindings🔸 Skills Used:Get AWS Guard Duty Findings, List Guardduty Detectors, List Guardduty Findings✅ AmazonS3ReadOnlyAccess
✅ AmazonS3ReadOnlyAccess
Provides read-only access to evaluate S3 bucket security by checking configurations, classifying data sensitivity, and validating real-world exposure risks.🔸 Input Params Used:
service_name: s3, method_name: [get_bucket_acl, get_public_access_block, get_bucket_policy, get_bucket_tagging, list_objects_v2]🔸 AWS Actions:s3:ListAllMyBuckets, s3:ListBucket, s3:GetObject, s3:GetBucketLocation for the dedicated S3 skills; s3:GetBucketAcl, s3:GetBucketPublicAccessBlock, s3:GetBucketPolicy, s3:GetBucketTagging for bucket-configuration checks through General AWS Query🔸 Skills Used:List S3 Buckets, List S3 Objects, Get S3 Objects, general_aws_query📎 Findings: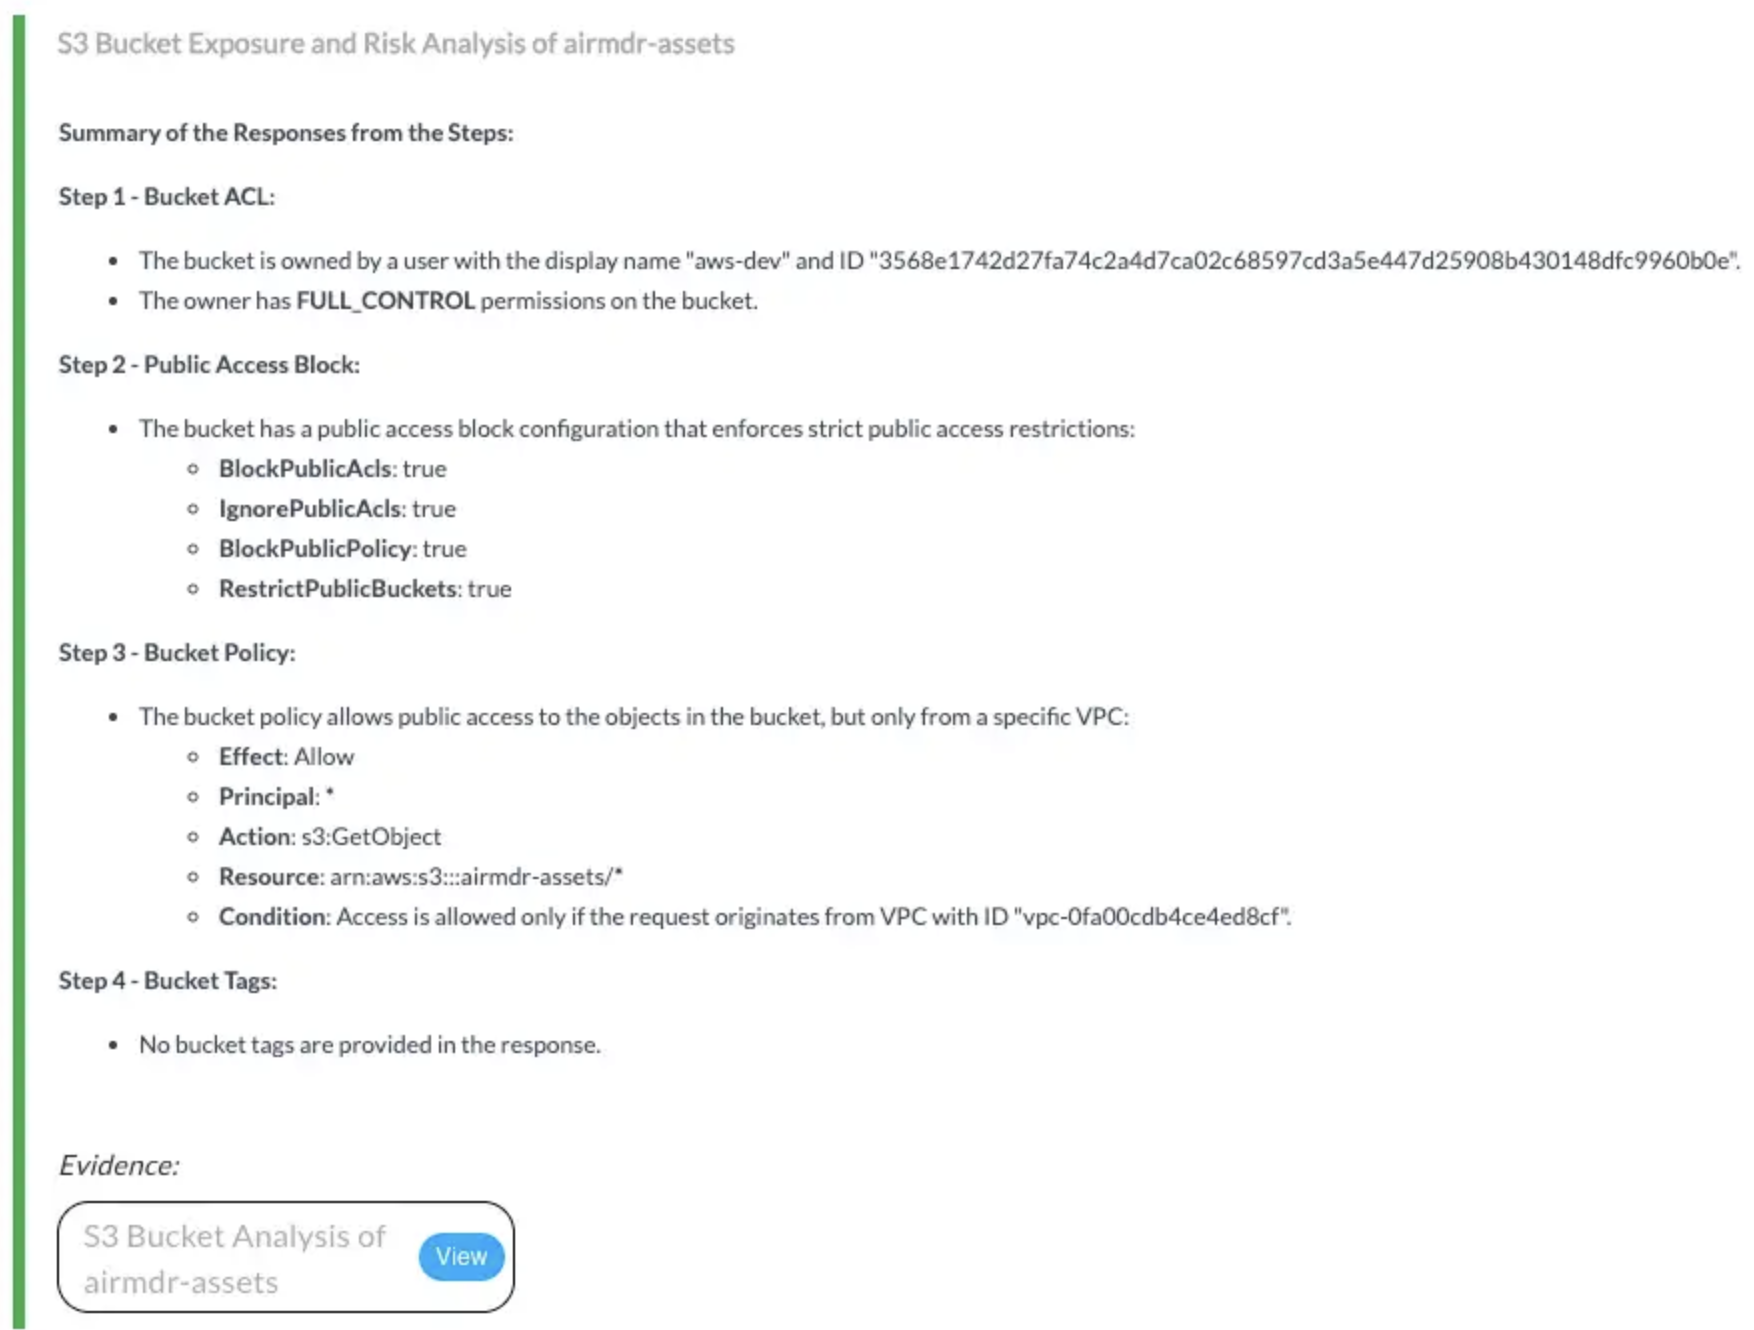
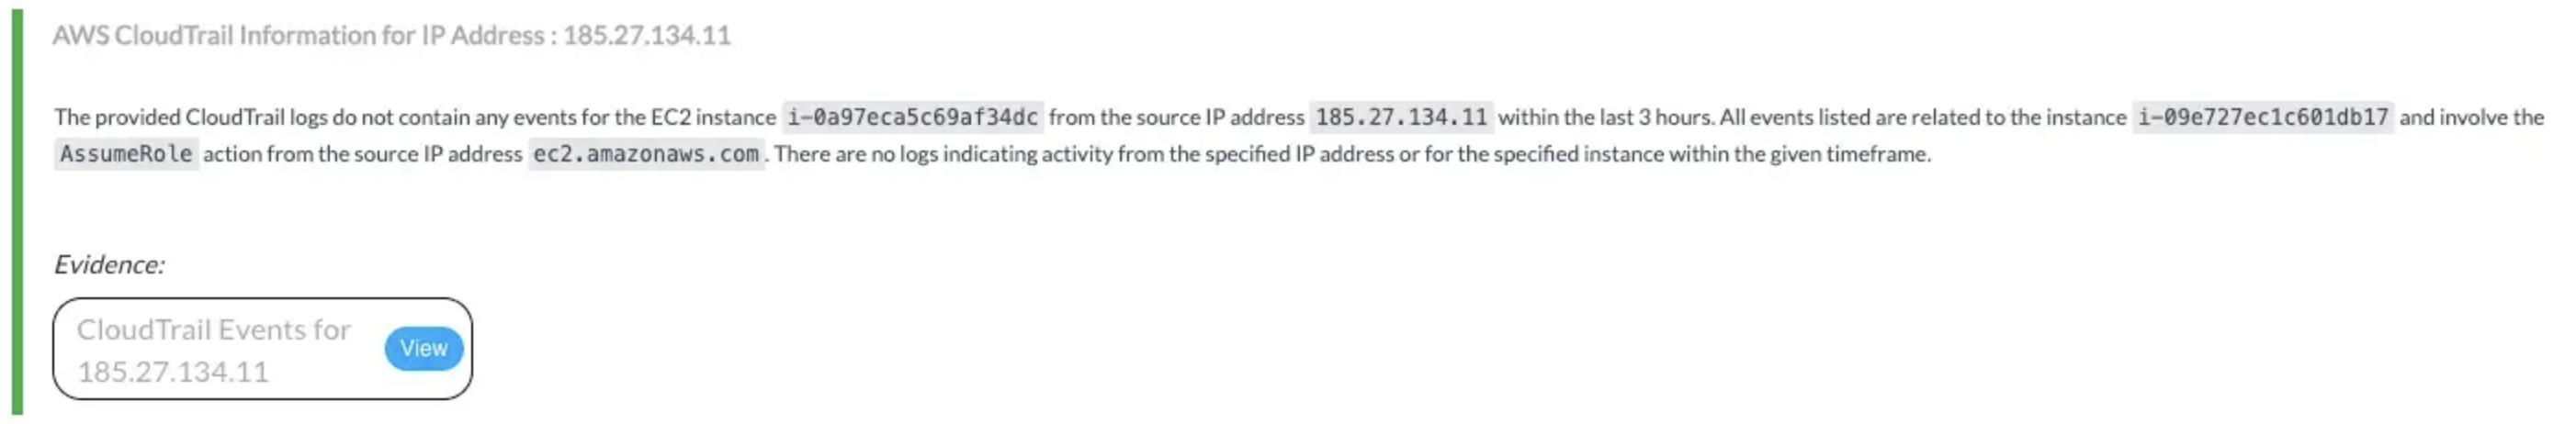
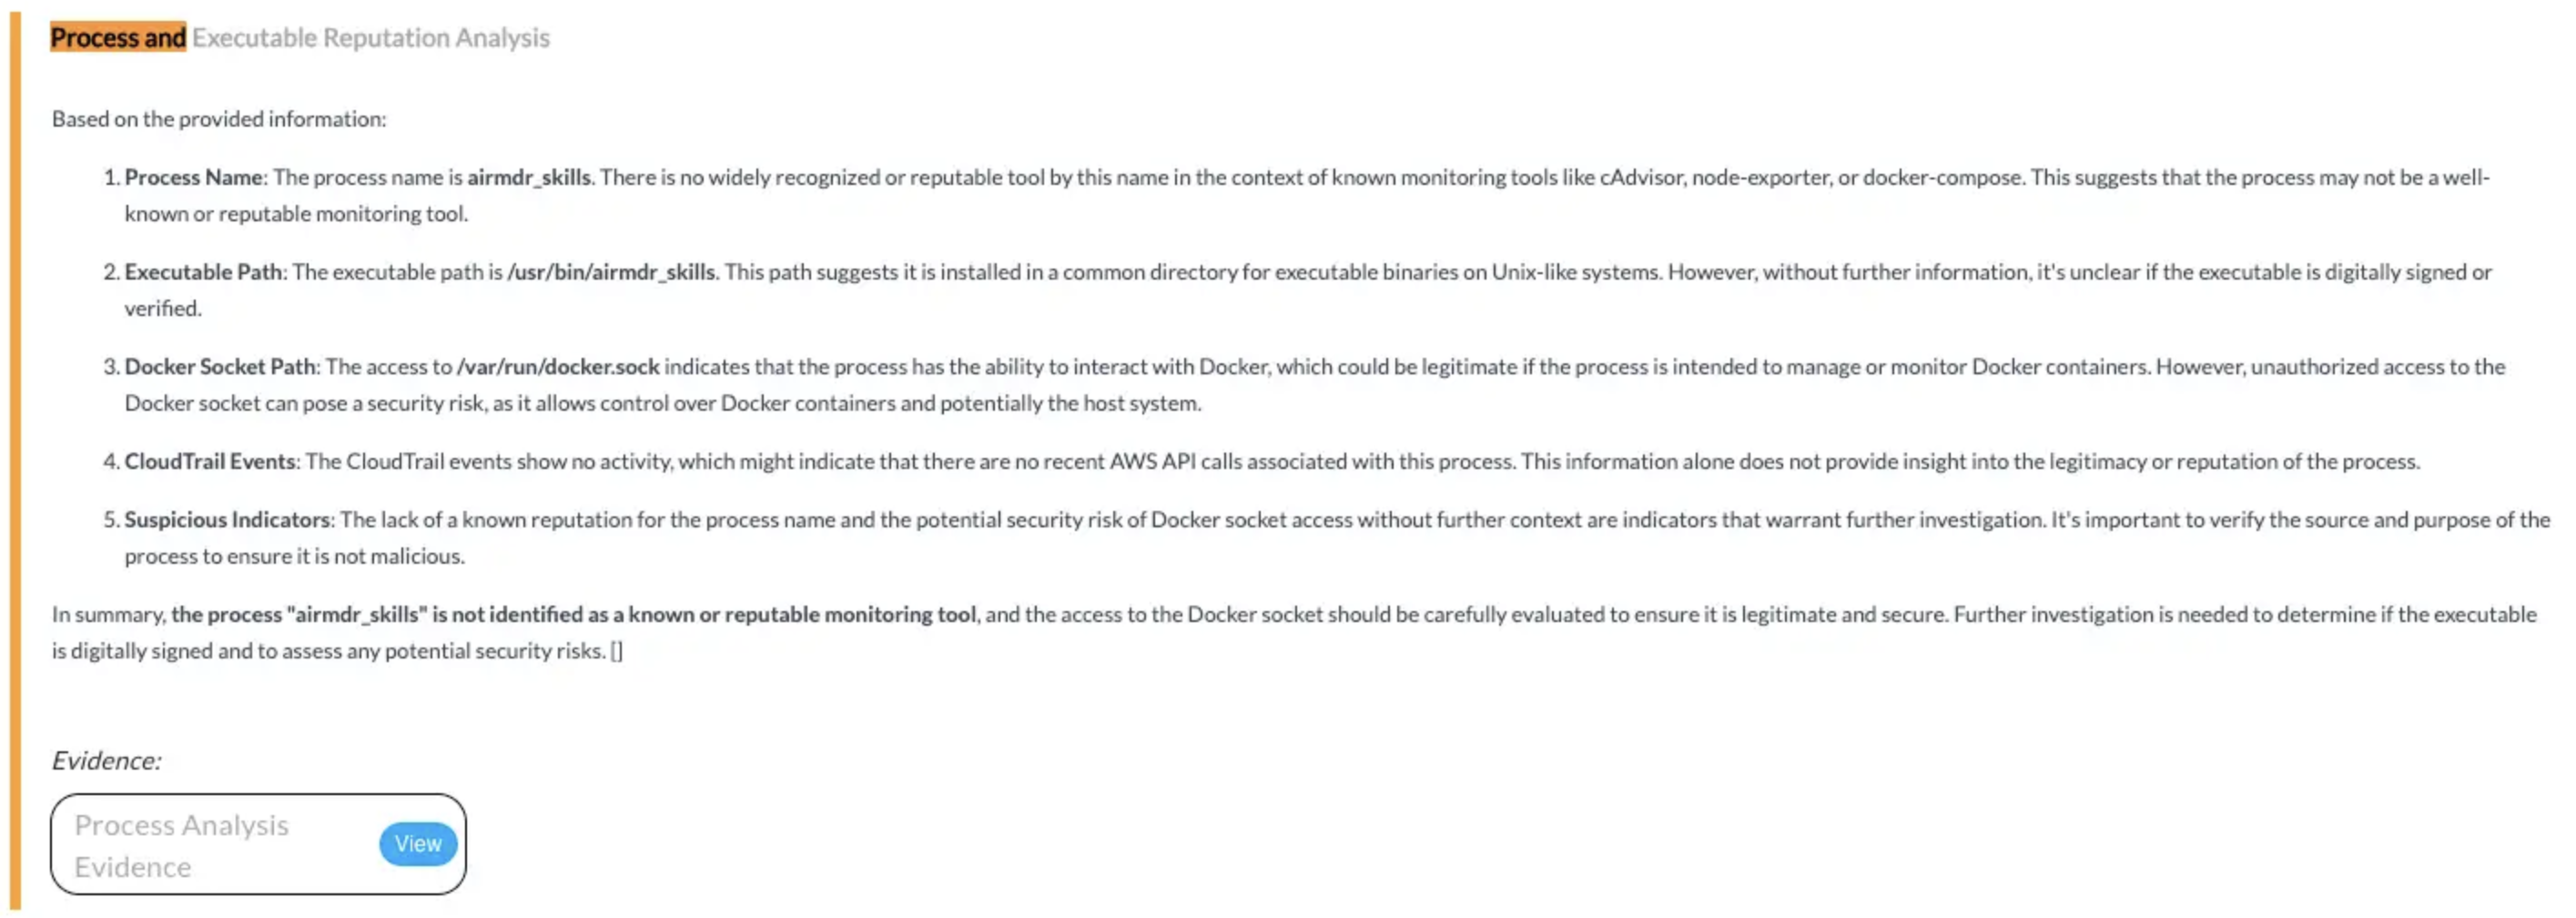
✅ AWSCloudTrail_ReadOnlyAccess
✅ AWSCloudTrail_ReadOnlyAccess
Grants read-only access to CloudTrail logs for reconstructing activity timelines, detecting suspicious patterns, and enriching alerts with user and process-level context.🔸 Input Params Used:
Attribute Key: ResourceName, Attribute Value: ec2 instance id, filter_key: sourceIPAddress🔸 AWS Actions:cloudtrail:DescribeTrails, cloudtrail:GetTrailStatus, cloudtrail:LookupEvents🔸 Skills Used:Lookup AWS CloudTrail Events, List Cloudtrail Trails📎 Findings: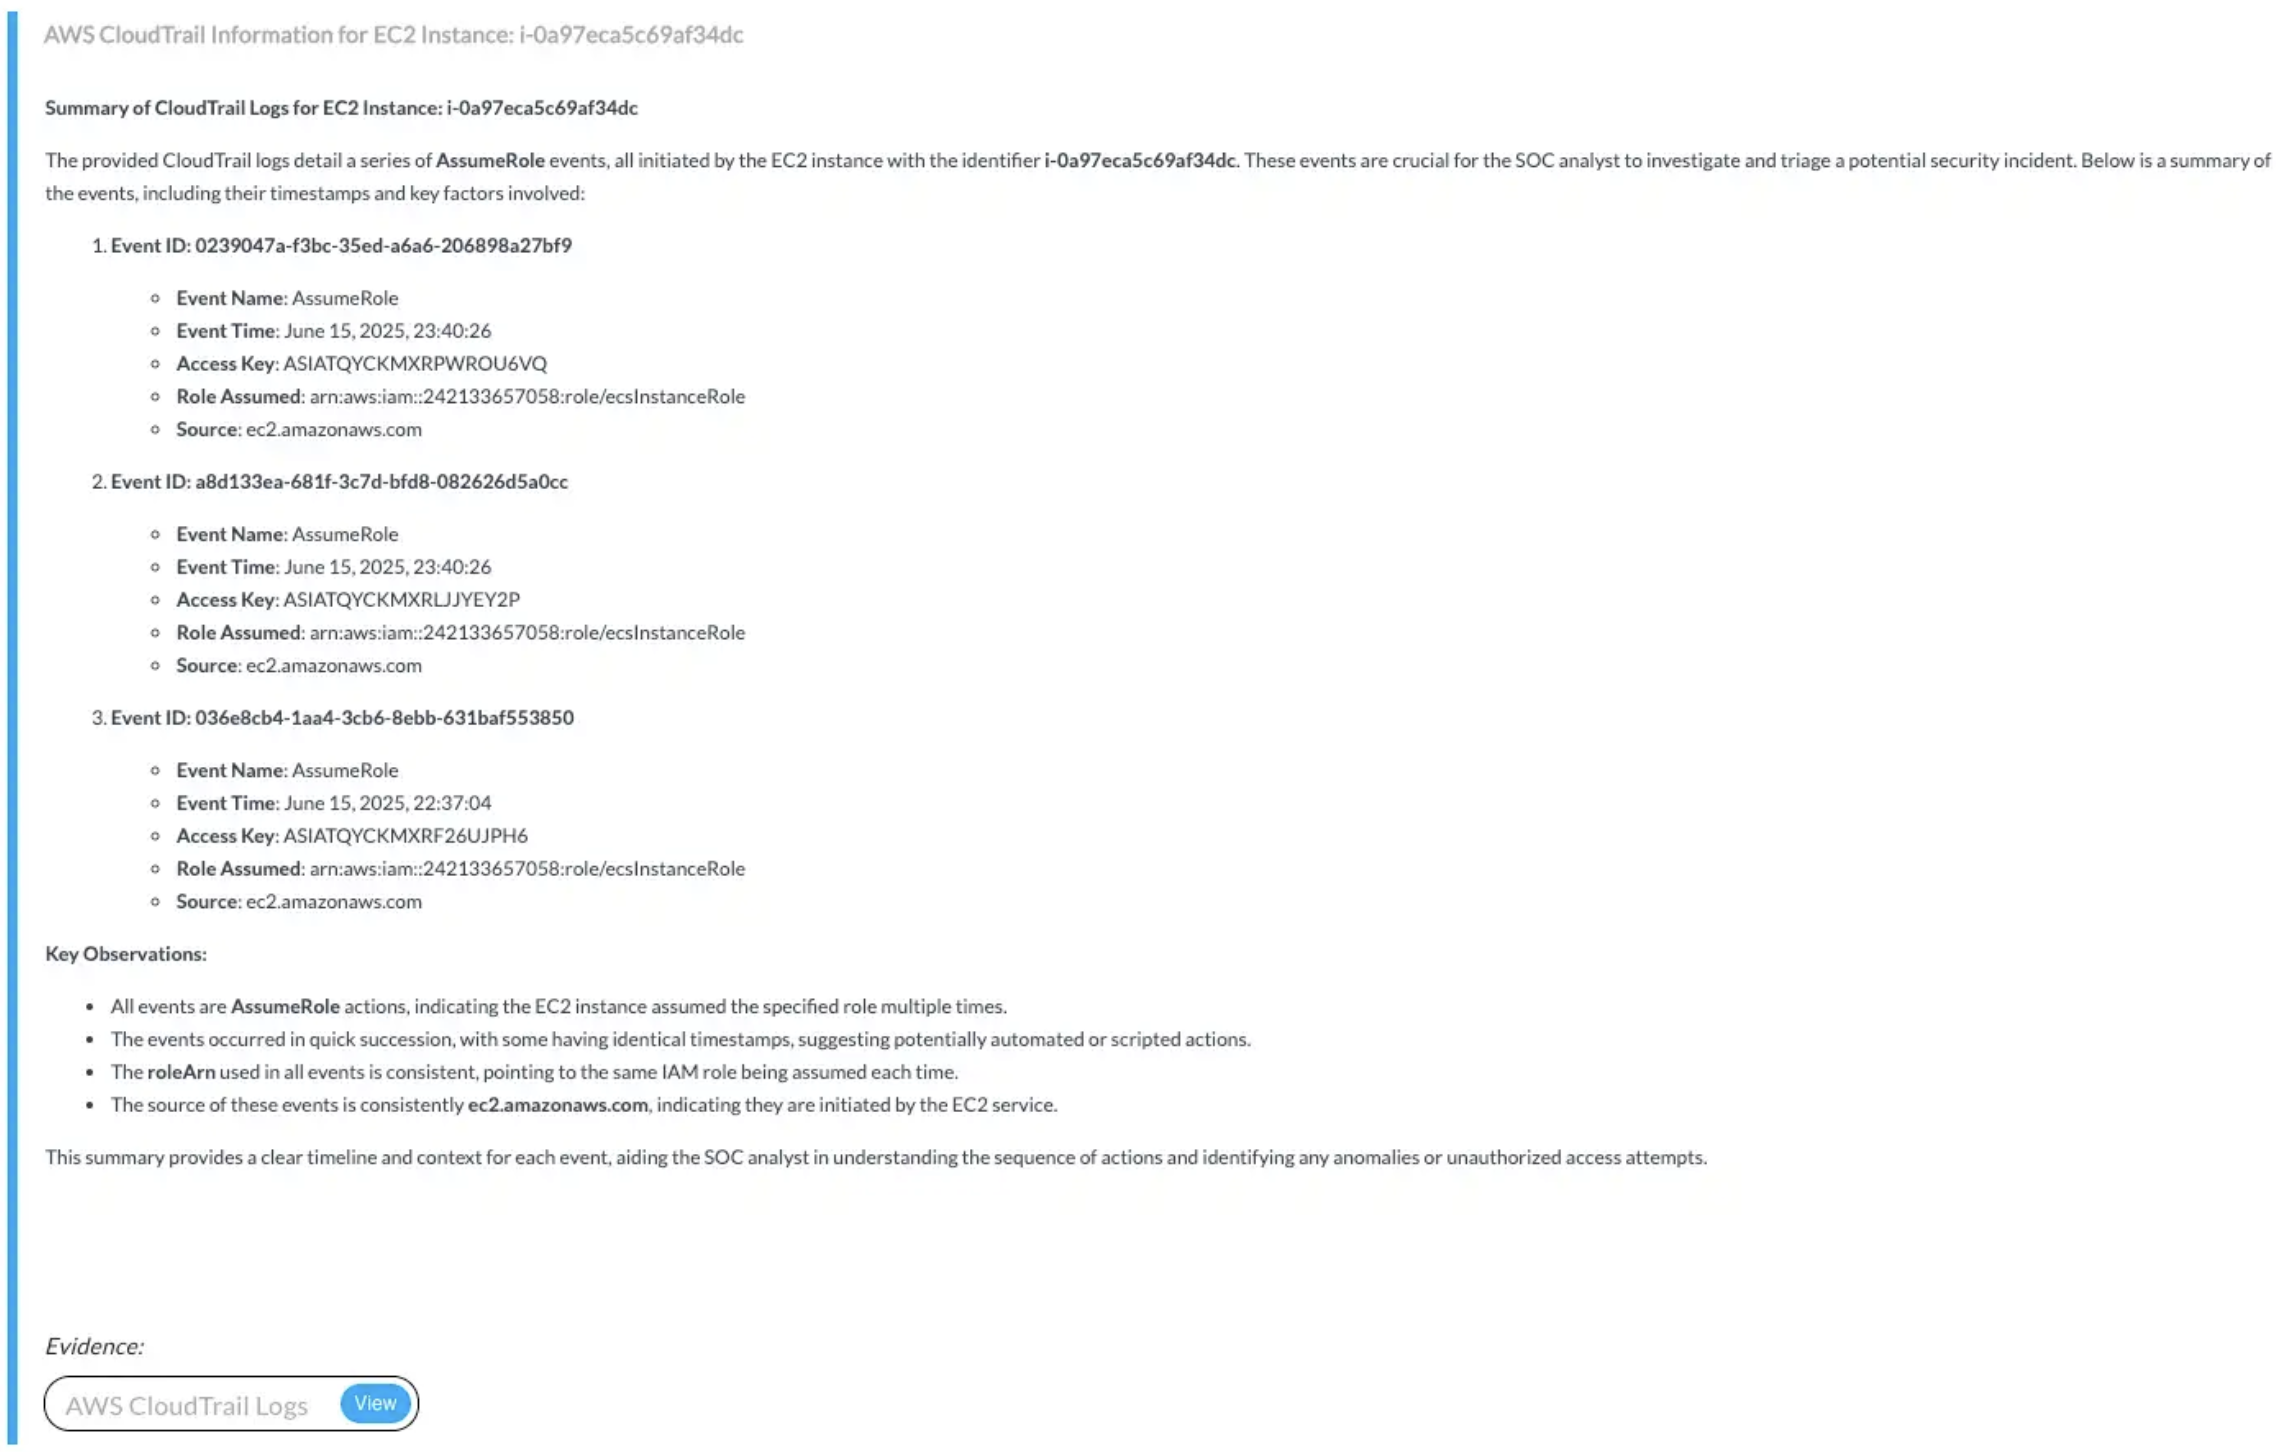
✅ CloudWatchReadOnlyAccess
✅ CloudWatchReadOnlyAccess
Allows read-only access to CloudWatch logs and metrics for analyzing VPC activity, extracting alert context, and enriching investigations with time-bound log insights and metric statistics.🔸 Input Params Used:
Log Group Name, Log Stream Name Prefix🔸 AWS Actions:logs:DescribeLogGroups, logs:DescribeLogStreams, logs:GetLogEvents, logs:FilterLogEvents, cloudwatch:GetMetricStatistics🔸 Skills Used:List Cloudwatch Log Groups, Filter AWS CloudWatch Log Events, Get AWS CloudWatch Log Events, Get AWS CloudWatch Metrics📎 Findings: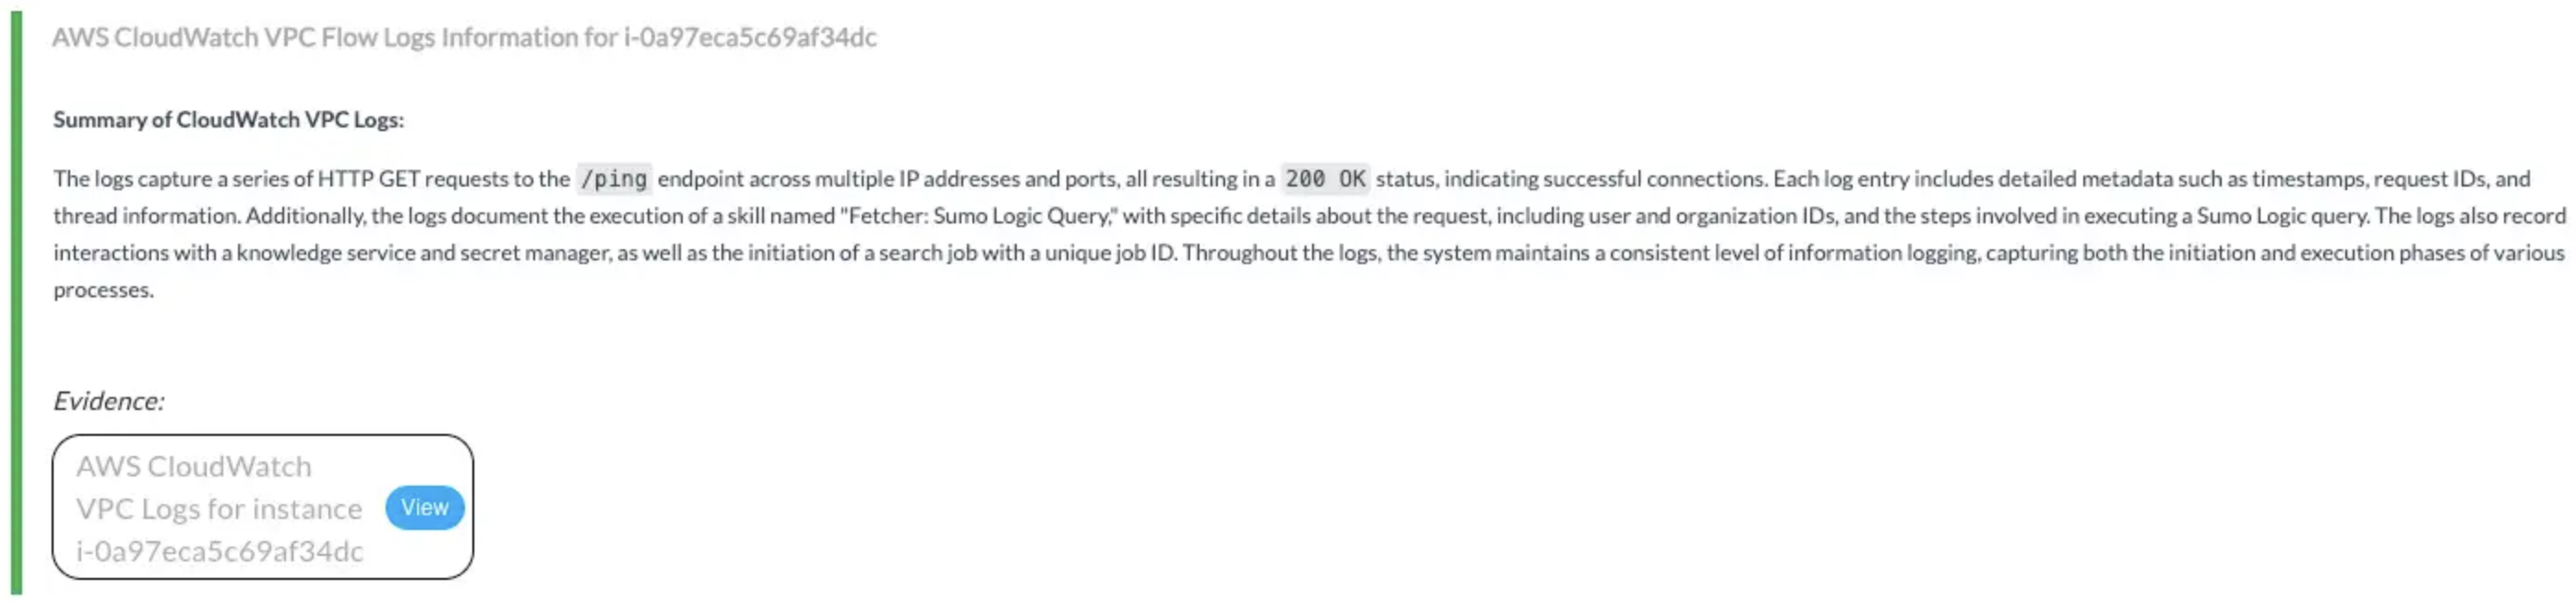
✅ AmazonEC2ContainerRegistryReadOnly
✅ AmazonEC2ContainerRegistryReadOnly
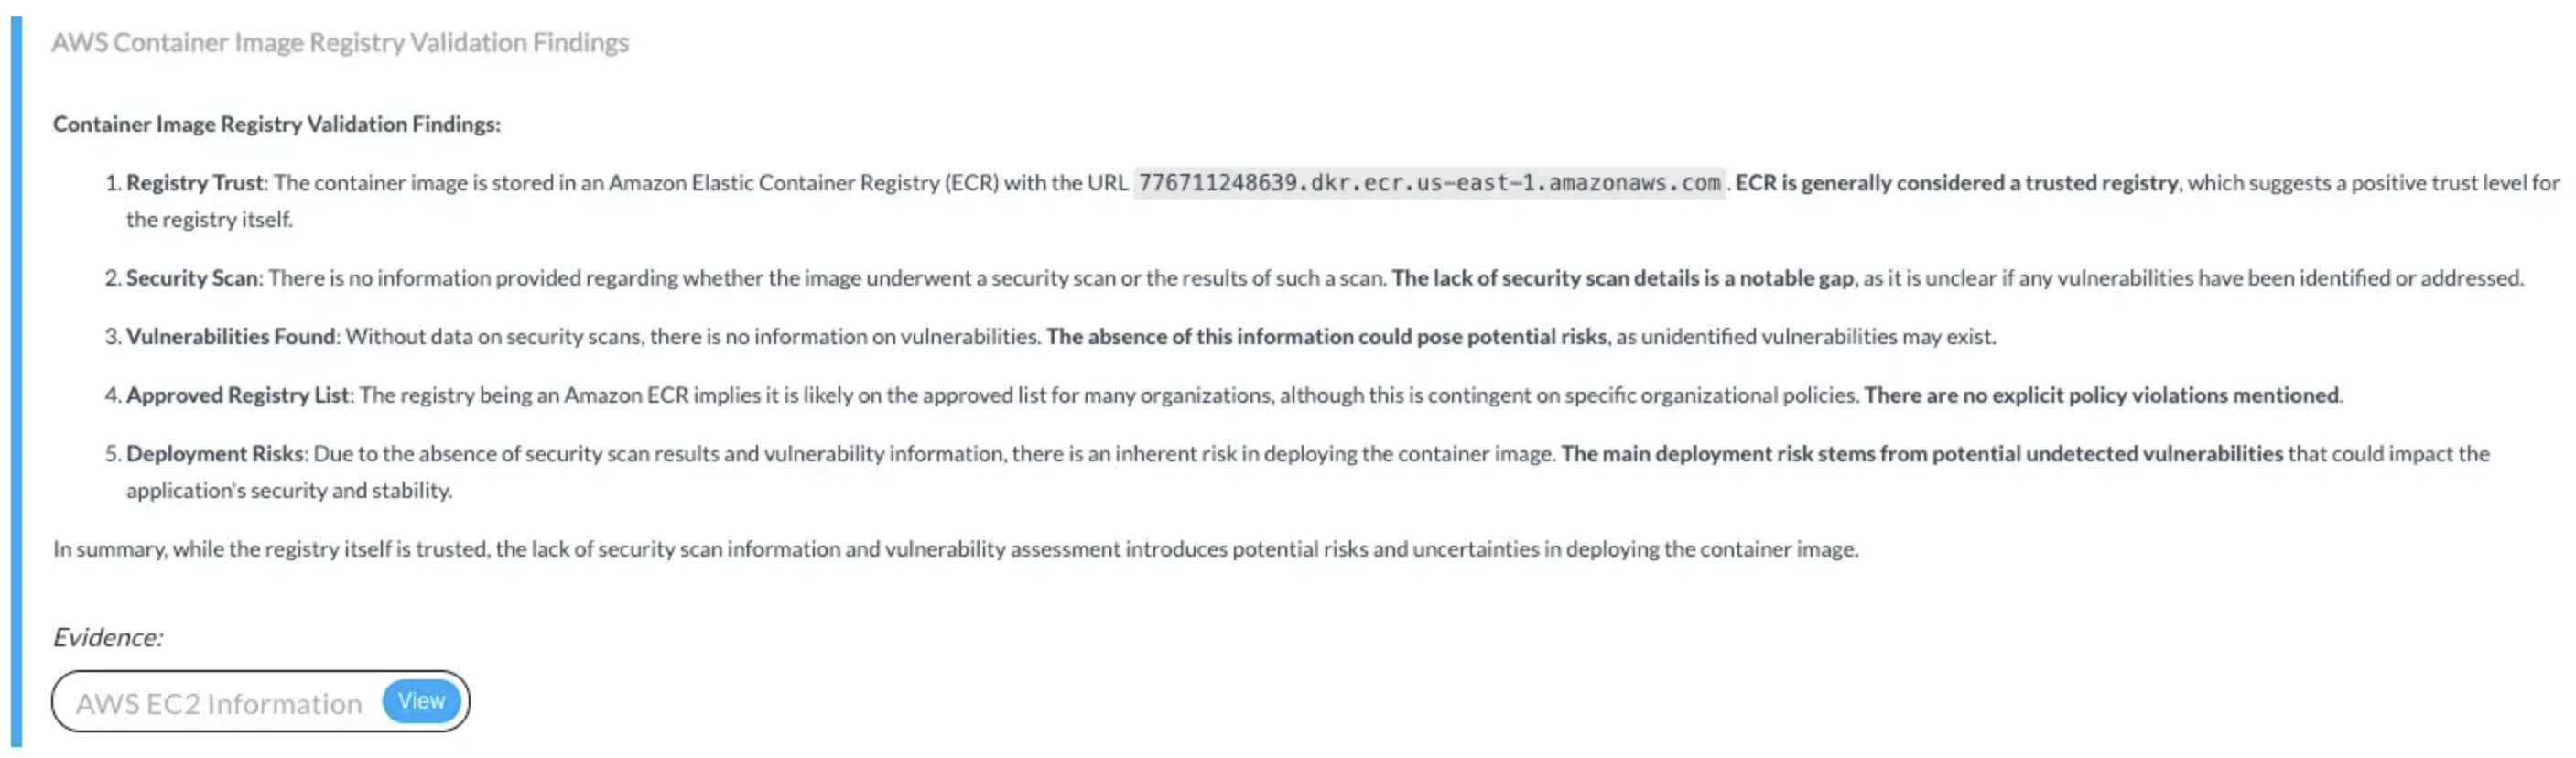
Provides read-only access to container workloads and images, letting AirMDR identify what a running task is executing and validate container deployment standards during an investigation.🔸 Input Params Used:
service_name: [ecs, ecr], method_name: [describe_tasks, describe_images]🔸 AWS Actions:ecs:DescribeTasks, ecr:DescribeImages🔸 Skills Used:general_aws_query✅ AWSSecurityHubReadOnlyAccess
✅ AWSSecurityHubReadOnlyAccess
Provides read-only access to Security Hub findings and enabled standards, letting AirMDR correlate findings from Security Hub’s integrated sources and check compliance posture during an investigation.🔸 AWS Actions:
securityhub:GetFindings, securityhub:GetFindingsV2, securityhub:GetEnabledStandards🔸 Skills Used:Get AWS SecurityHub Findings, Get AWS SecurityHub Findings v2, List Securityhub Standards✅ IAMReadOnlyAccess
✅ IAMReadOnlyAccess
Enables validation of IAM permissions and detection of unusual user behavior, such as bulk S3 modifications, to support access risk analysis.🔸 Input Params Used:
service_name: iam, method_name: [get_user, list_attached_user_policies, simulate_principal_policy]🔸 AWS Actions:iam:SimulatePrincipalPolicy for Get AWS Caller Permissions; iam:GetUser, iam:ListAttachedUserPolicies through General AWS Query. Behavioral detection pairs these with cloudtrail:LookupEvents, granted under the CloudTrail entry.🔸 Skills Used:Get AWS Caller Permissions, general_aws_query, alongside Lookup AWS CloudTrail Events📎 Findings: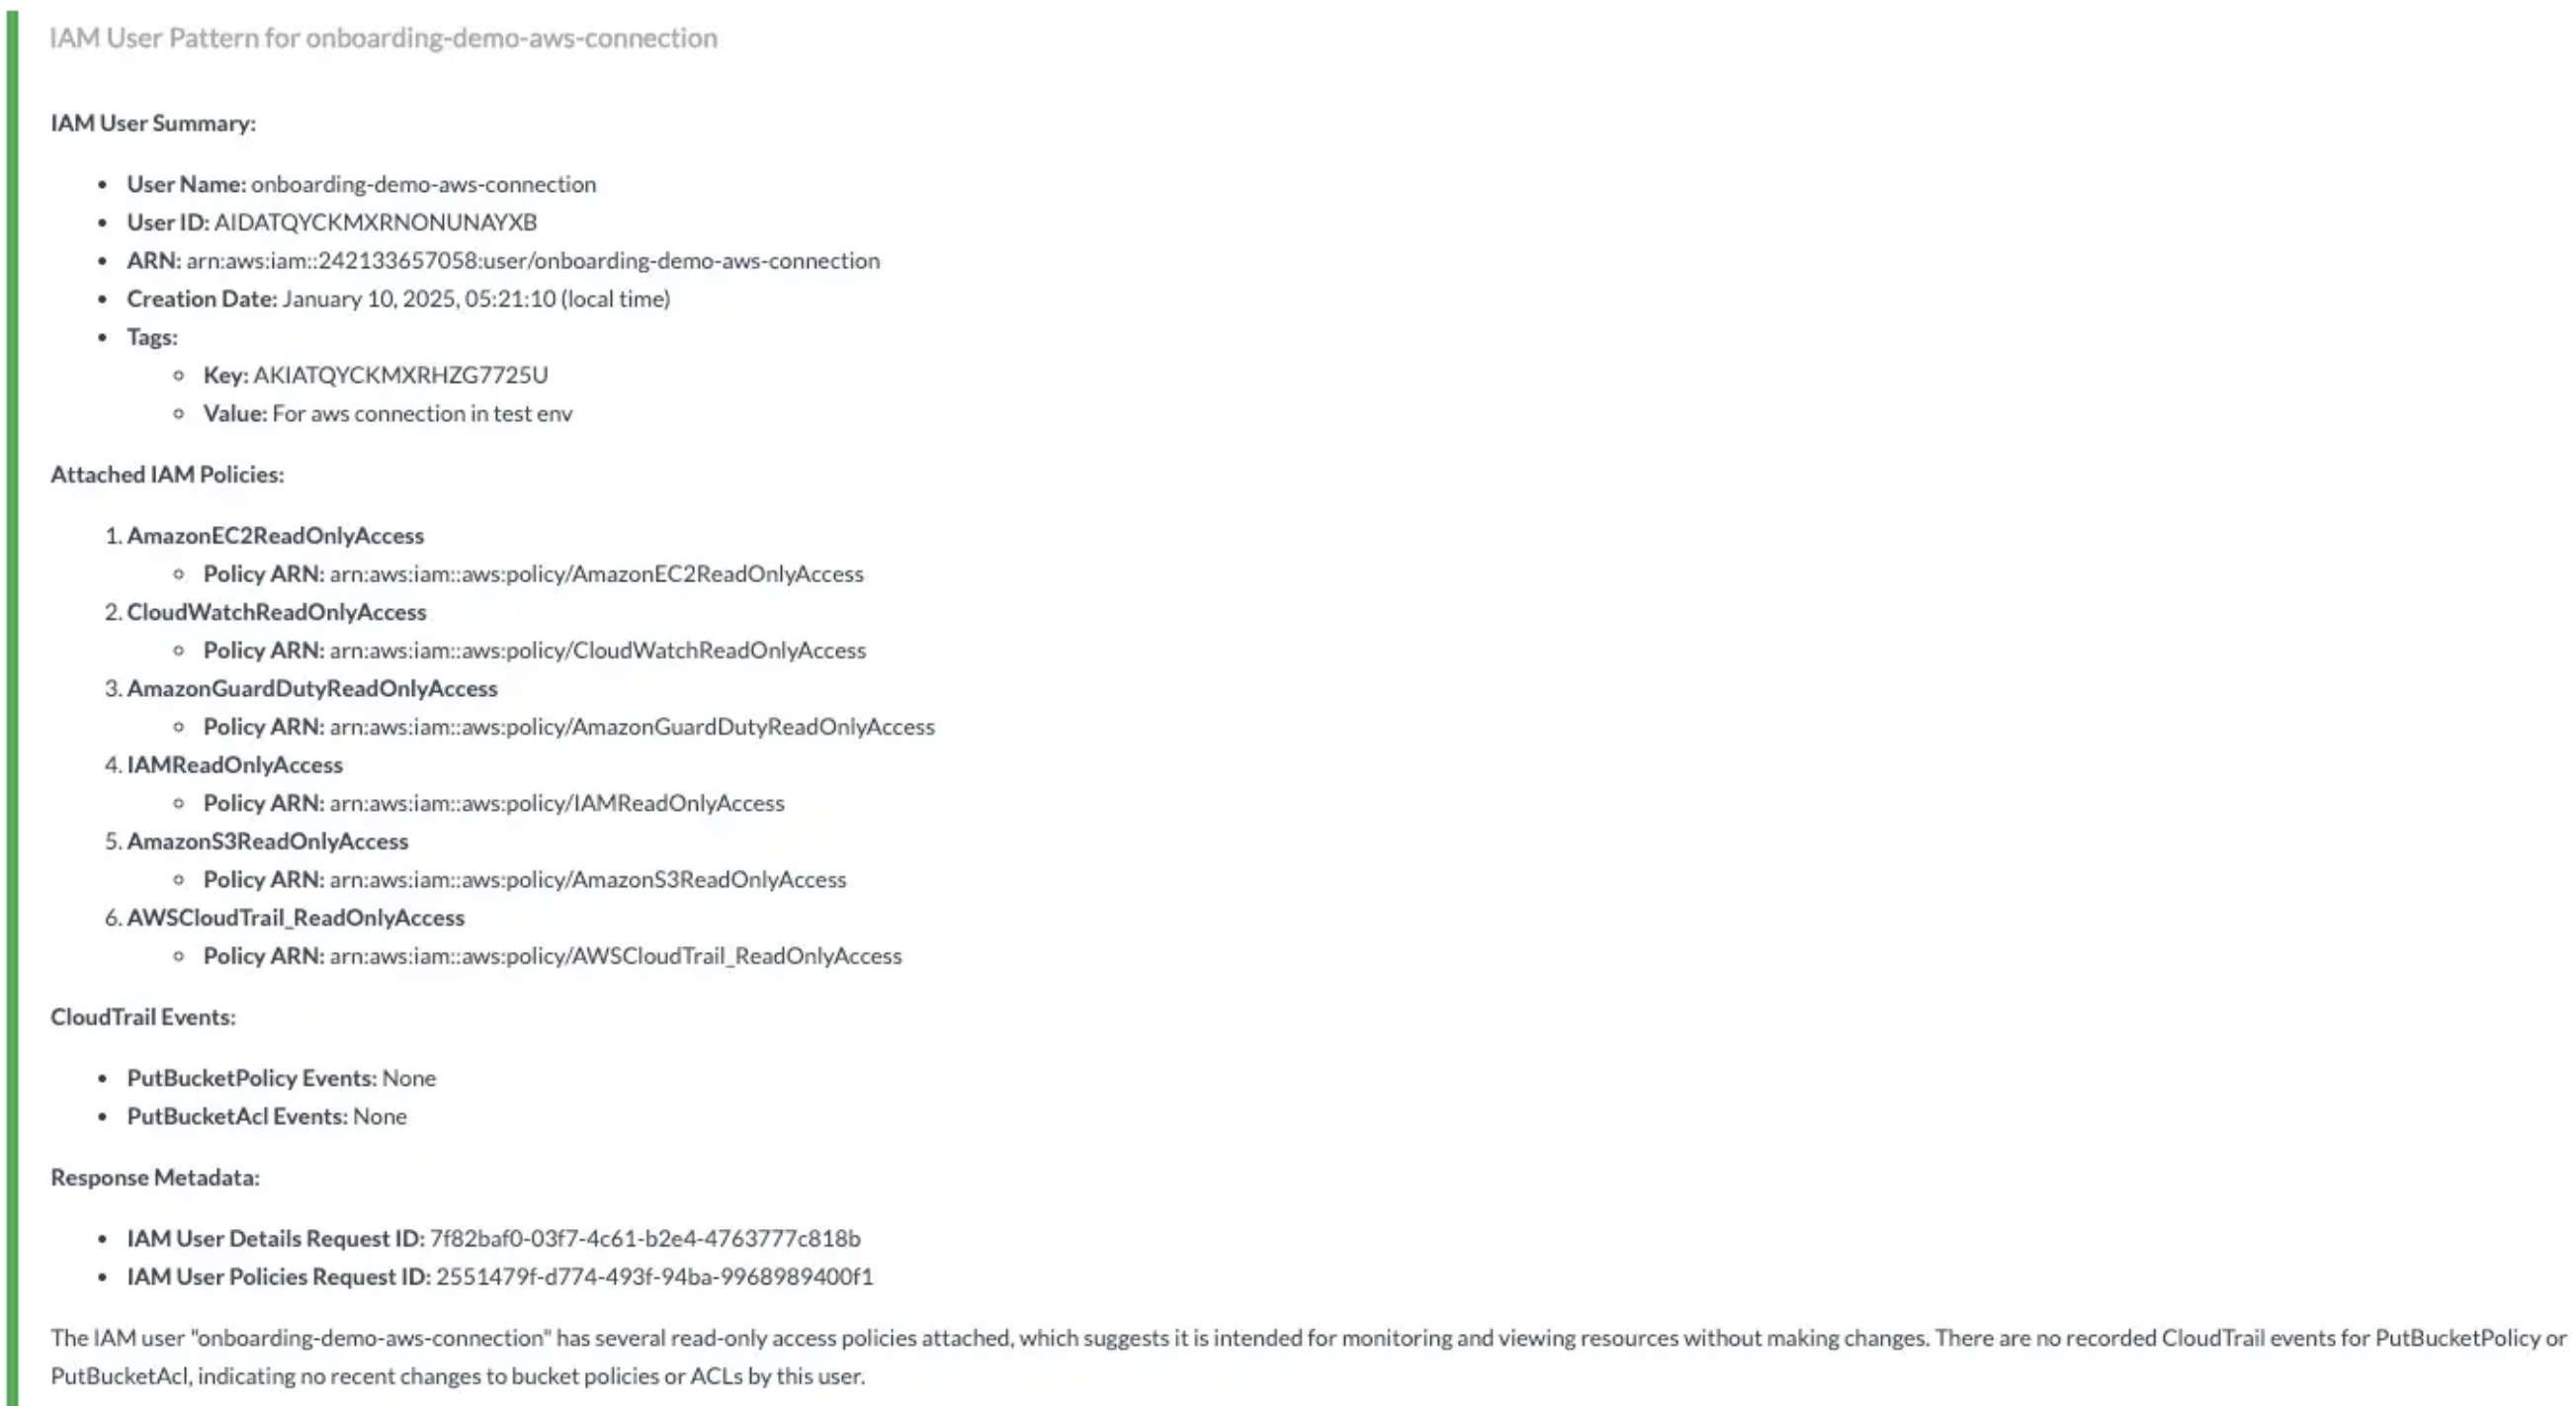
- Sign in to the AWS IAM Console of the account where you enabled GuardDuty.
- Search for IAM in the top menu bar.
-
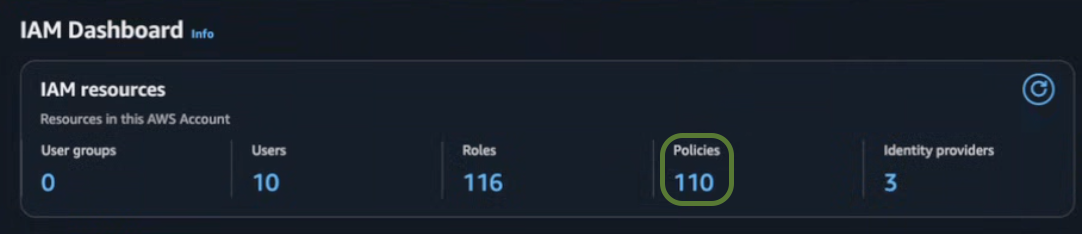
In the IAM dashboard, click on IAM resources → Policies.
-
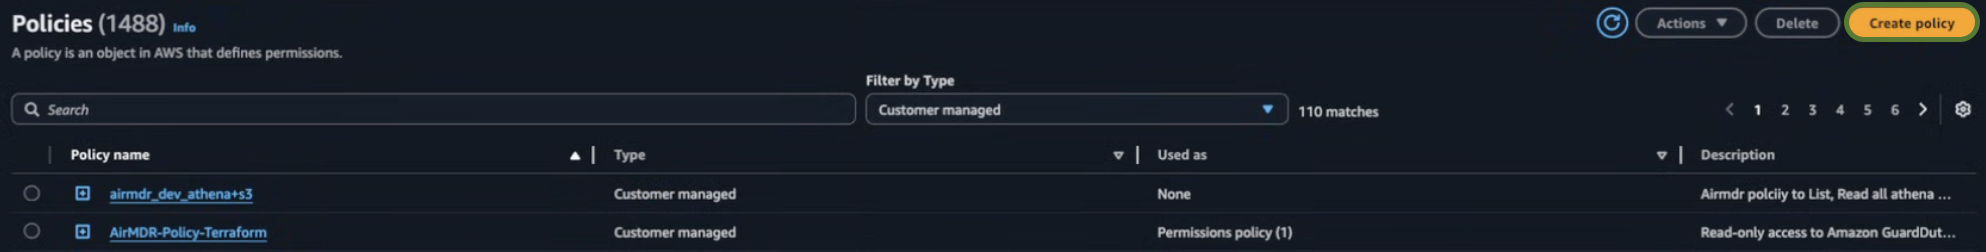
Click Create policy in the top right corner.
-
Select the JSON tab and paste the following:
 You can update the policy permissions in the JSON as per your requirement.The actions from
ec2:DescribeInstancesonwards serve General AWS Query. Drop them if your playbooks do not use that skill, and add whatever other actions the methods your playbooks do call require. - Click Next.
-
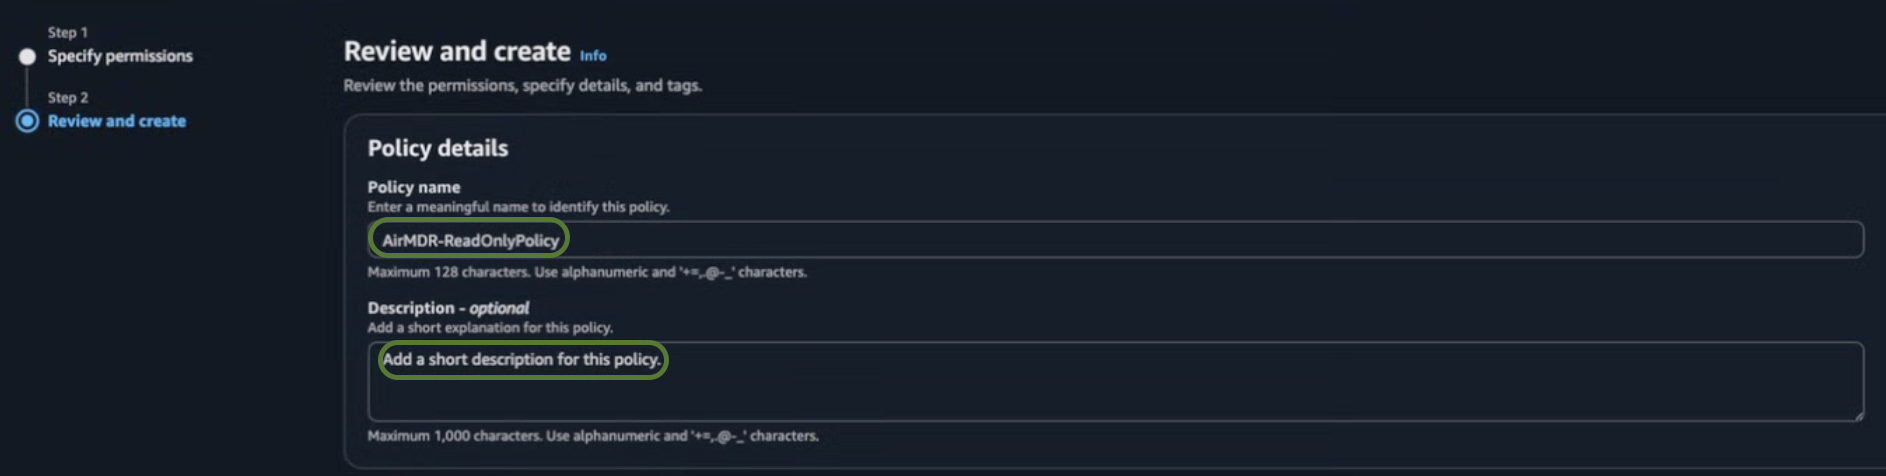
In the Review and create section, provide the Policy details:
- Policy name – Provide a meaningful name like
AirMDR-ReadOnlyPolicy. - Description (Optional) – Add a short description for this policy.
- Policy name – Provide a meaningful name like
-
Under Permissions defined in this policy, confirm the actions listed match what you pasted and meet your security requirements. A policy has no trust policy — that is set on the role in Option 2.
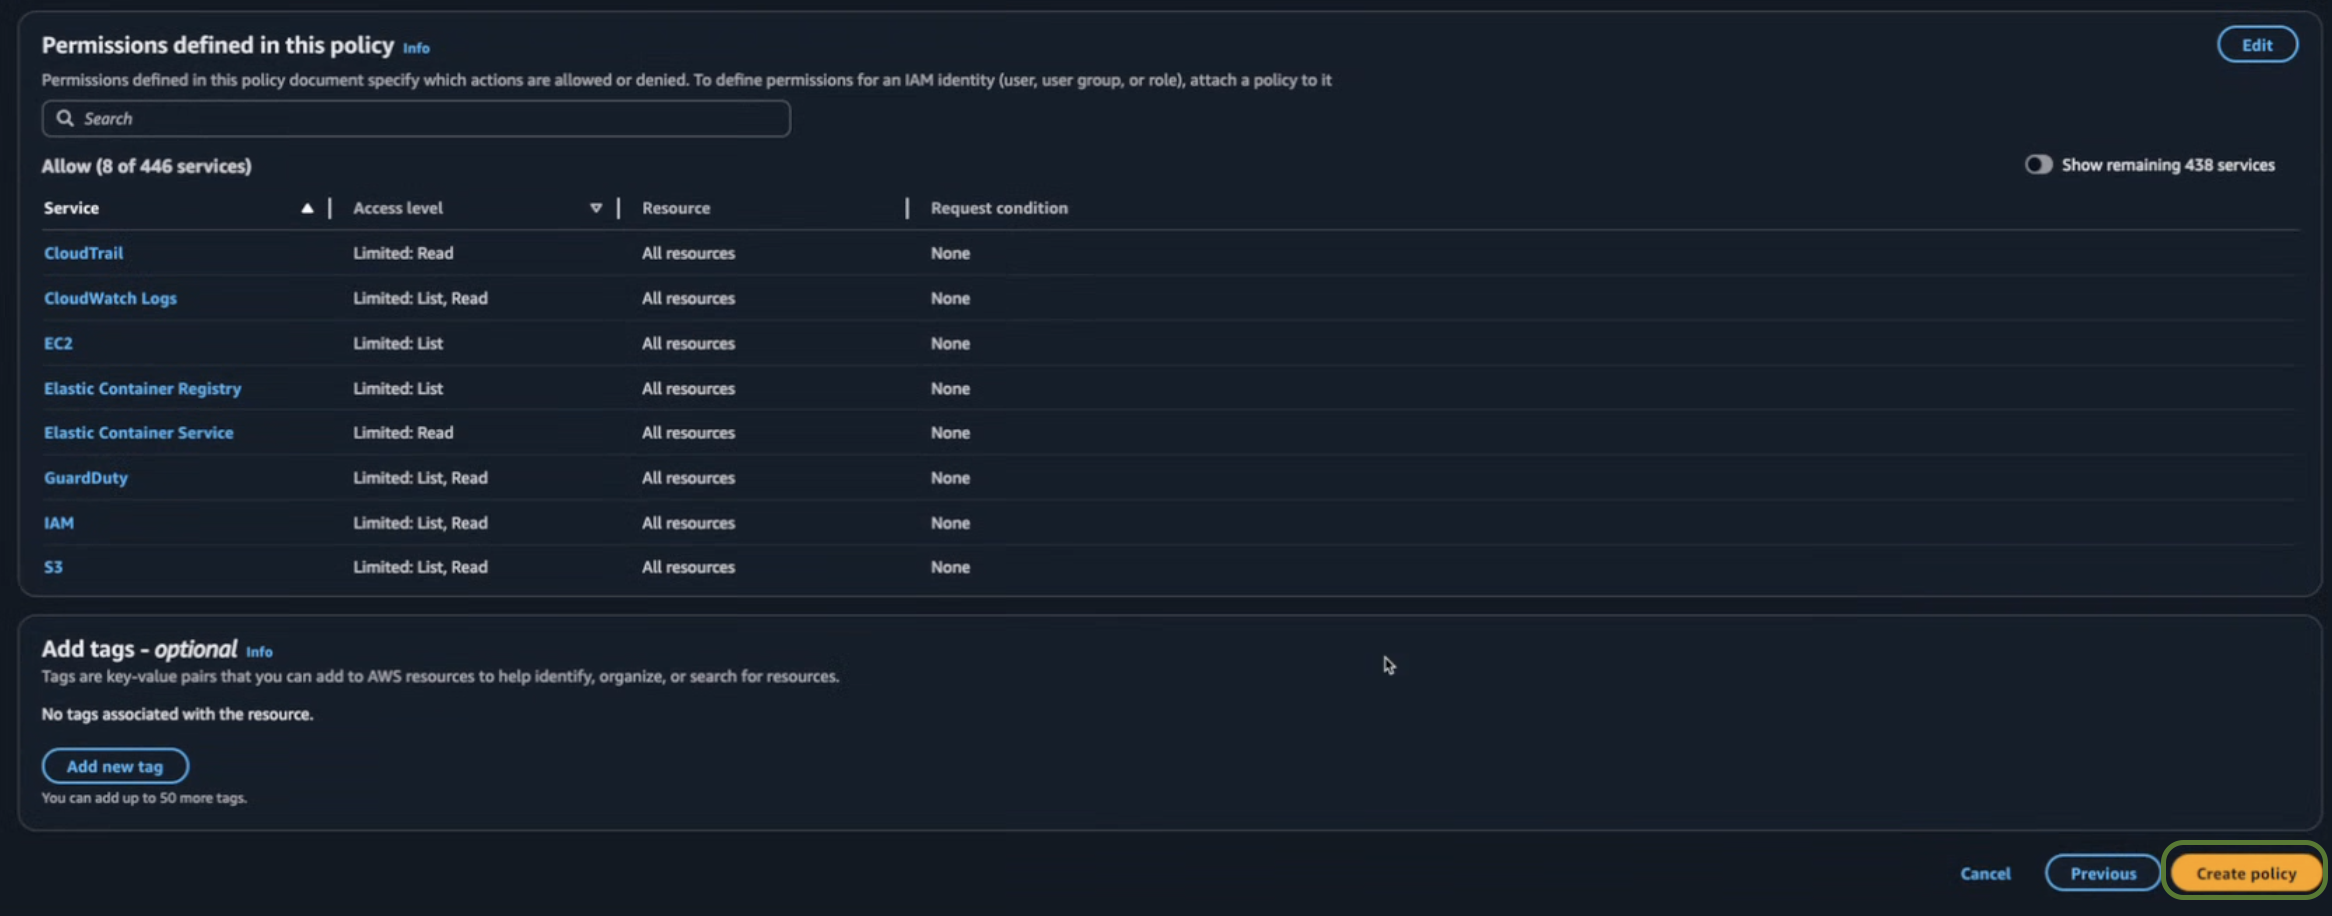
- Click Create policy.
Option 1: IAM User (Access Key Method)
Use this method if you prefer to authenticate via programmatic access credentials (Access Key ID and Secret Key).Create an IAM user and generate access keys
Create an IAM user and generate access keys
- Navigate to IAM → IAM Dashboard.
- Click on IAM resources → Users.
-
Click Create user in the top right corner.
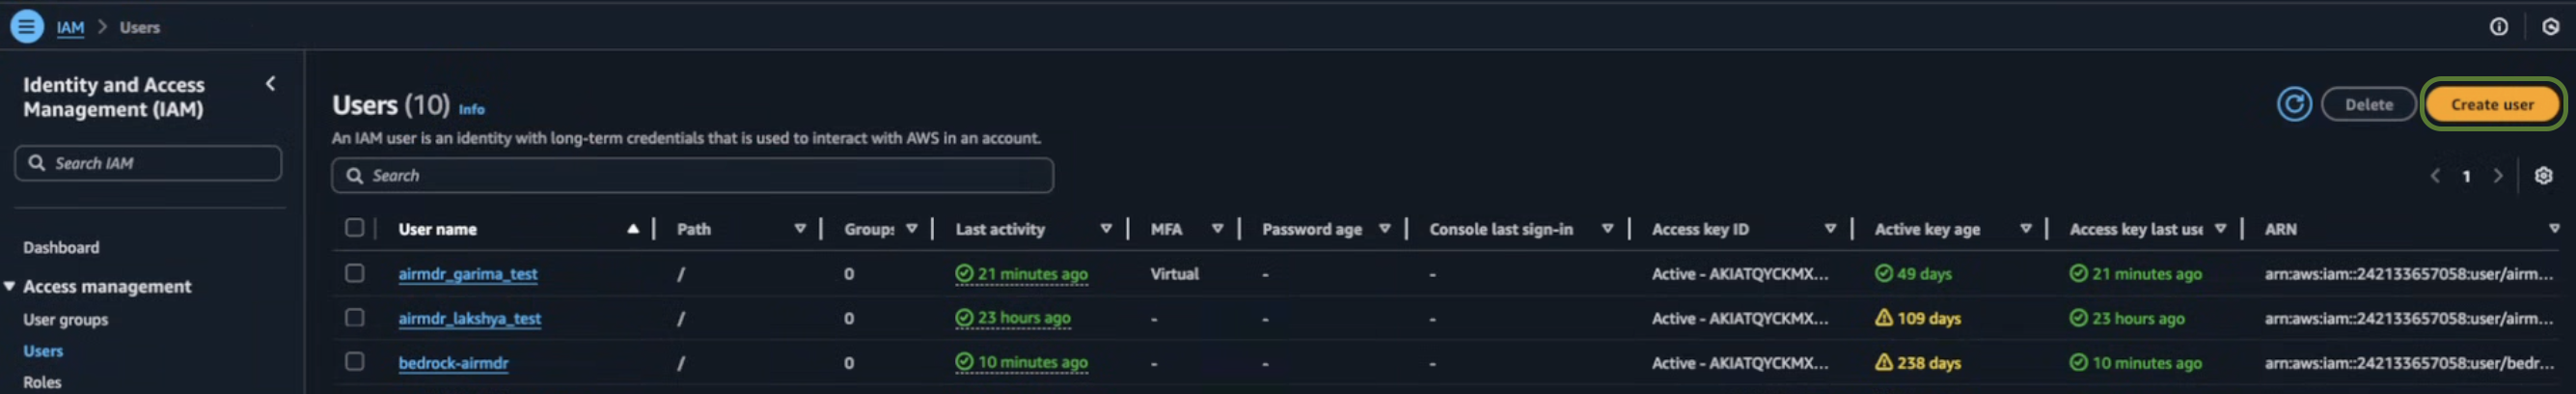
-
Enter a User name (e.g.,
airmdr-integrator). -
Click Next.
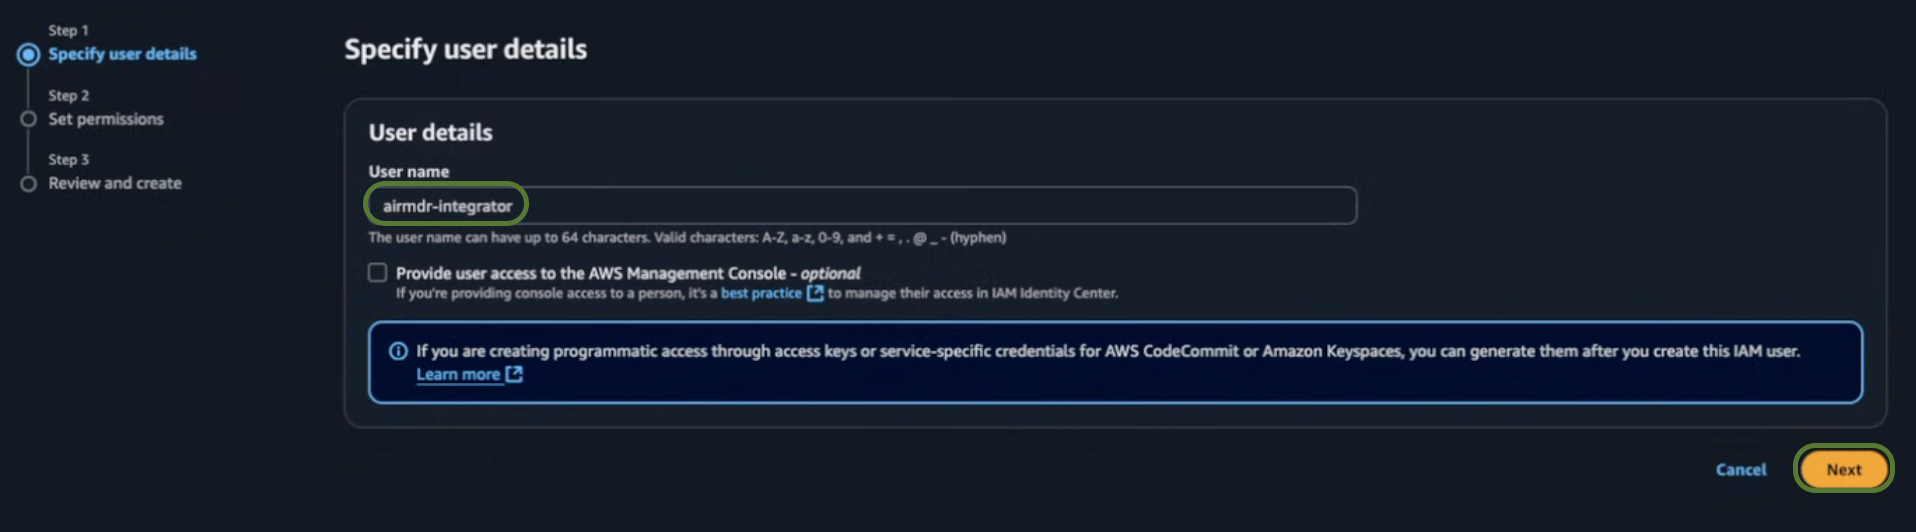
- In the Set permissions section, select Attach policies directly.
-
Search for and select
AirMDR-ReadOnlyPolicy.See Create IAM policy for detailed steps to defineAirMDR-ReadOnlyPolicyin IAM. -
Click Next.
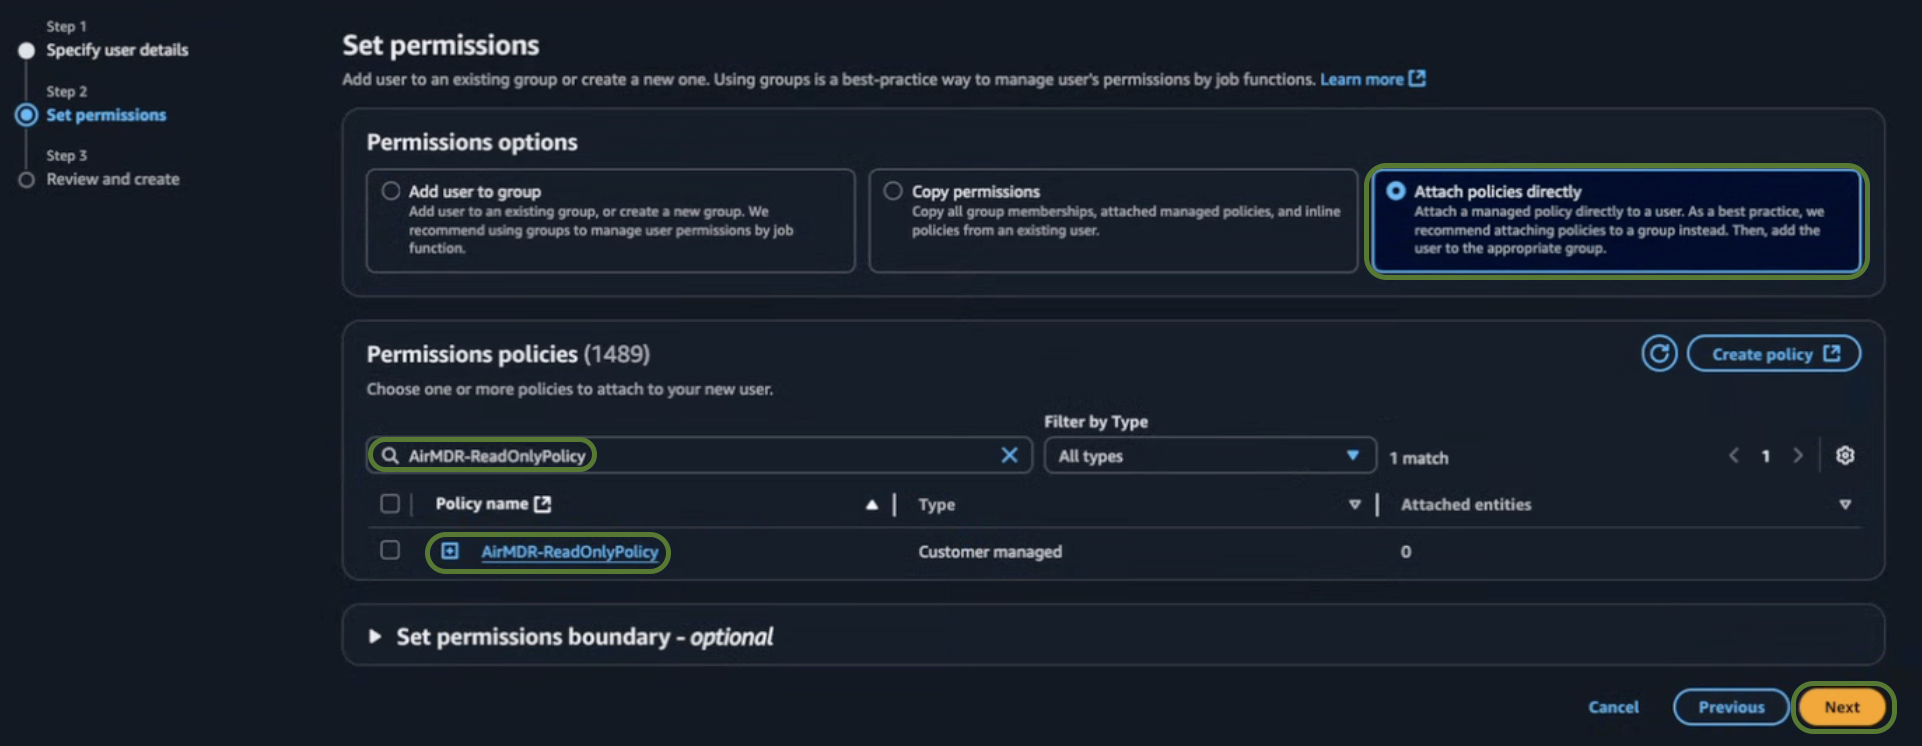
-
In the Review and create section, click Create user.
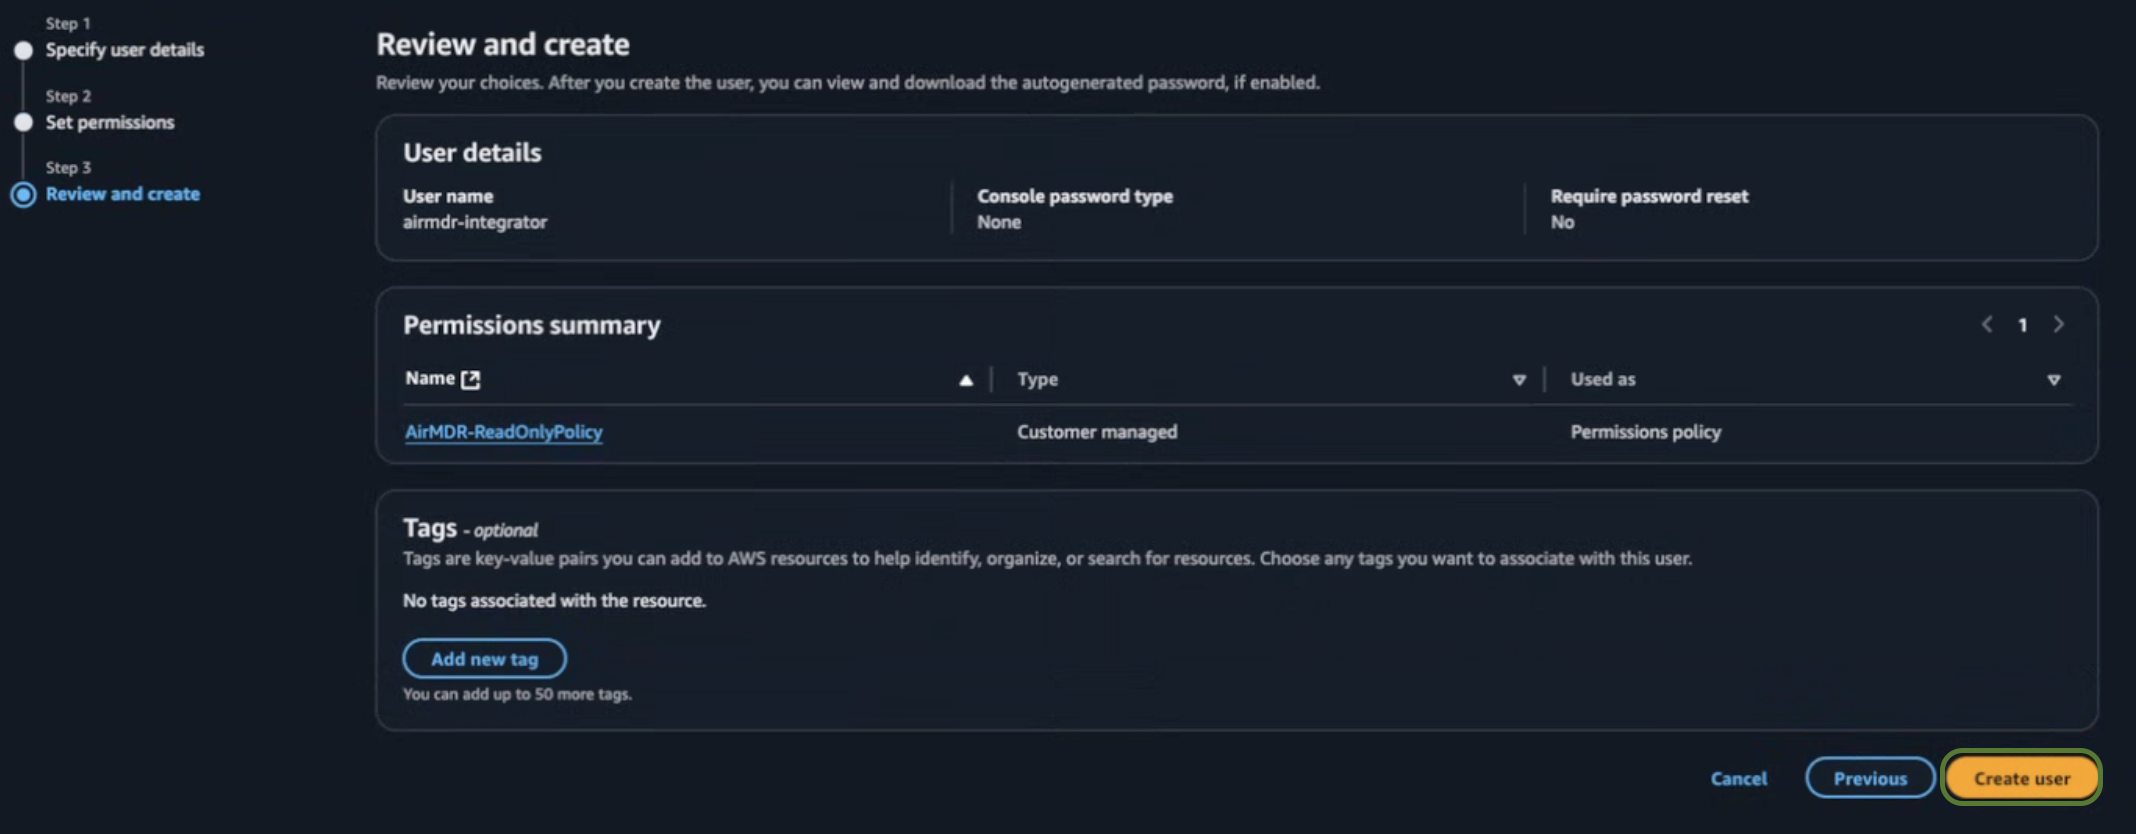
-
Search for and select the user you just created (e.g.,
airmdr-integrator). - Open the Security credentials tab and, under Access keys, click Create access key.
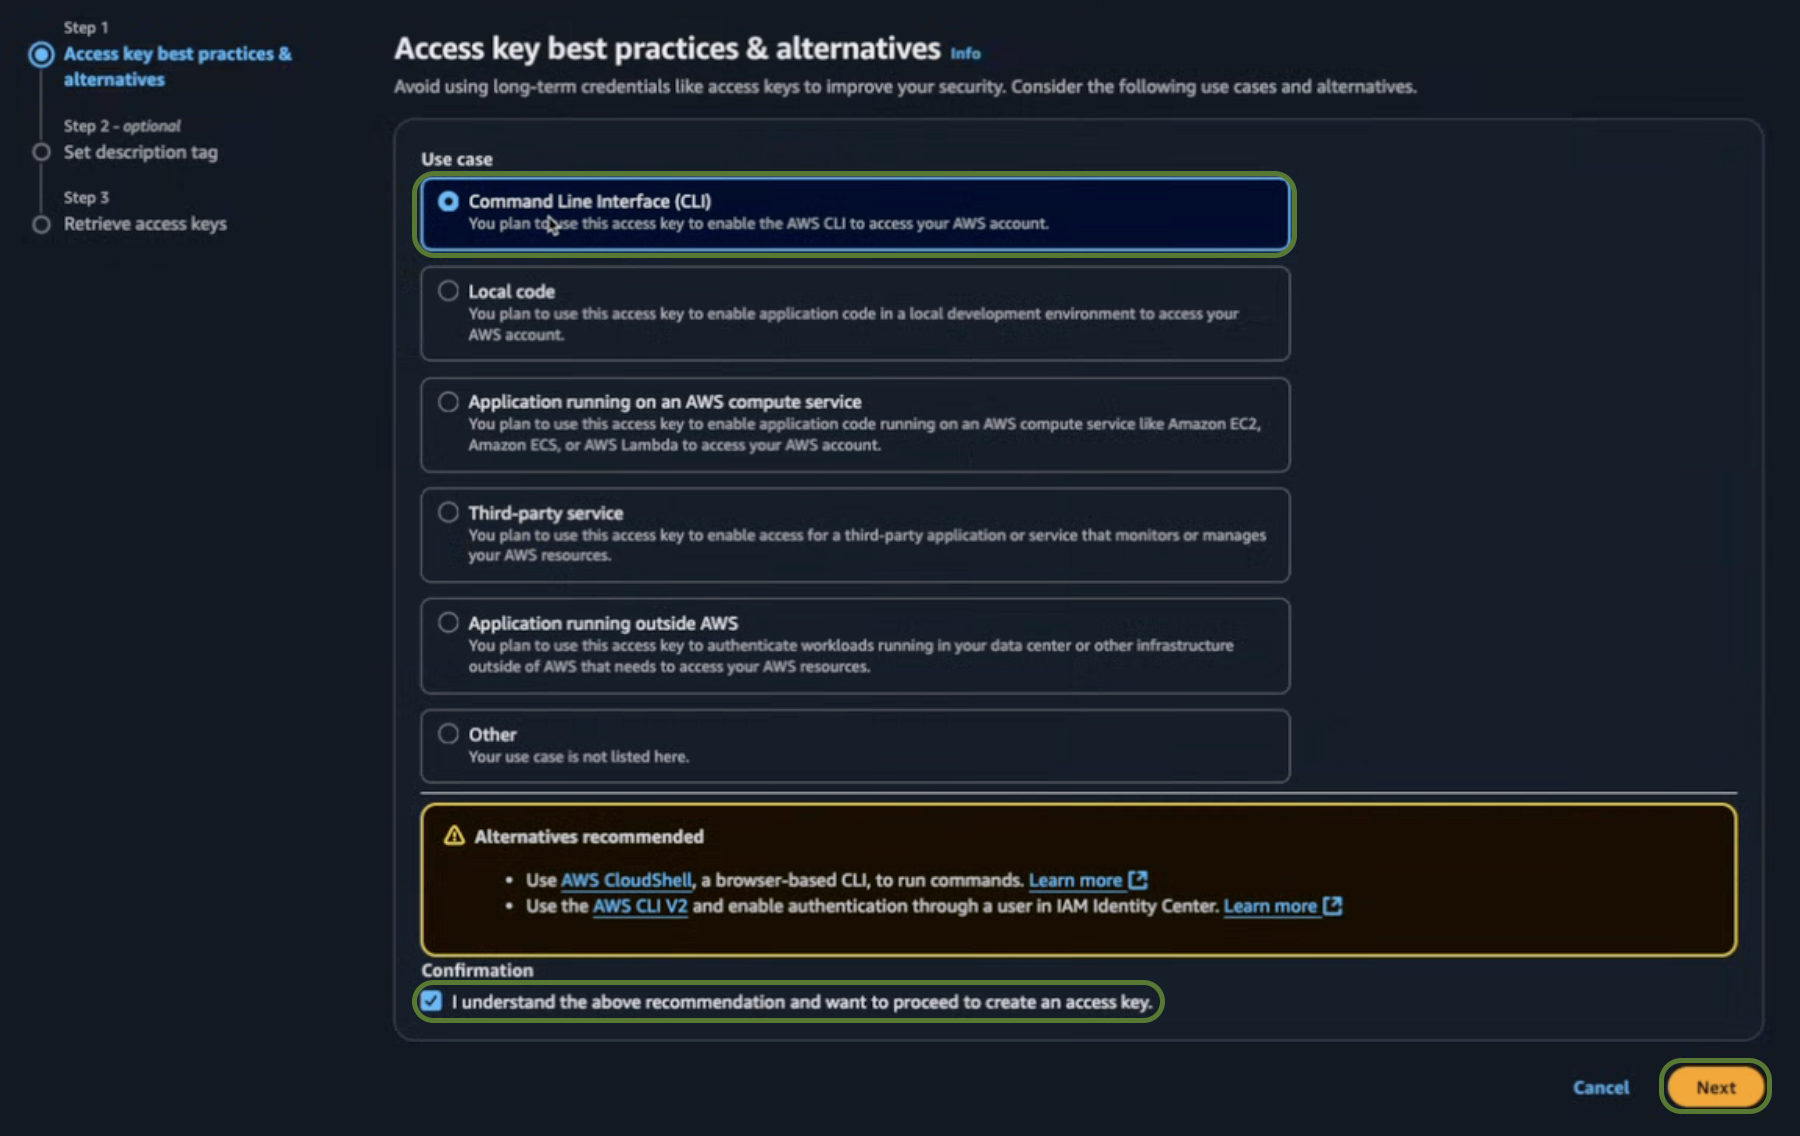
- Select the Command Line Interface (CLI) use case, then select the confirmation checkbox.
-
Click Next.
-
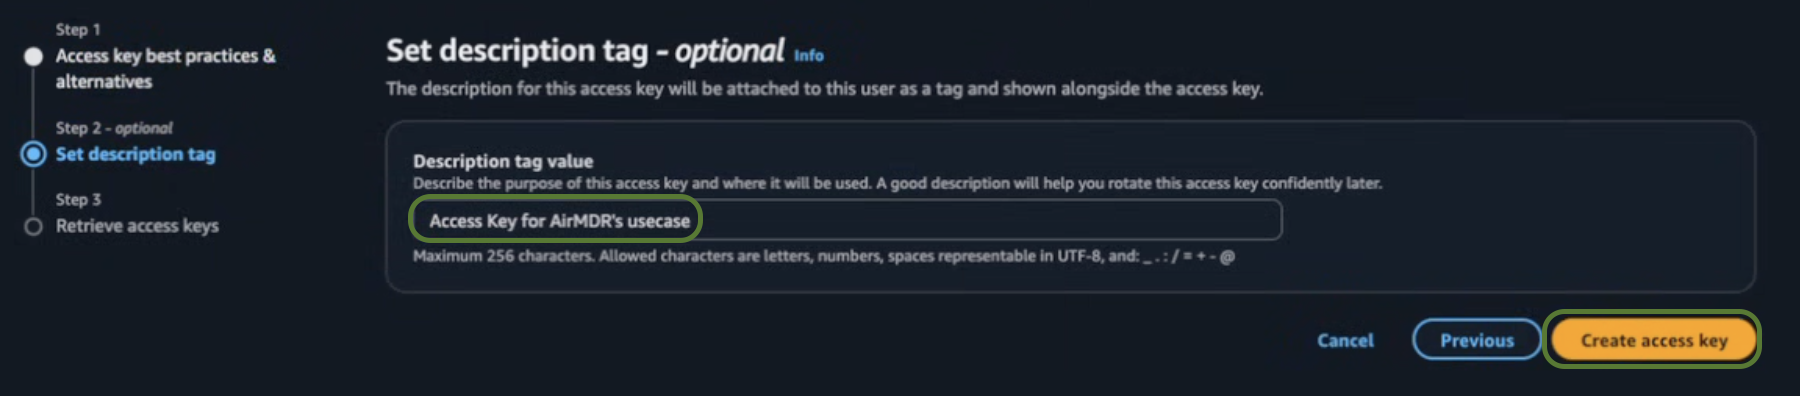
In the Set description tag - optional section, provide the Description tag value.
- Description tag value (Optional) – Access key for AirMDR’s use case.
-
Click Create access key.
-
On the Retrieve access keys screen, copy the:
- ✅ Access Key ID
- ✅ Secret Access Key
- Click Done.
Option 2: IAM Role (Assume Role via STS)
Use this method if you prefer to delegate access securely using AWS Security Token Service (STS). Recommended for production and enterprise environments.Create an IAM role for cross-account access
Create an IAM role for cross-account access
- Navigate to IAM → IAM Dashboard.
-
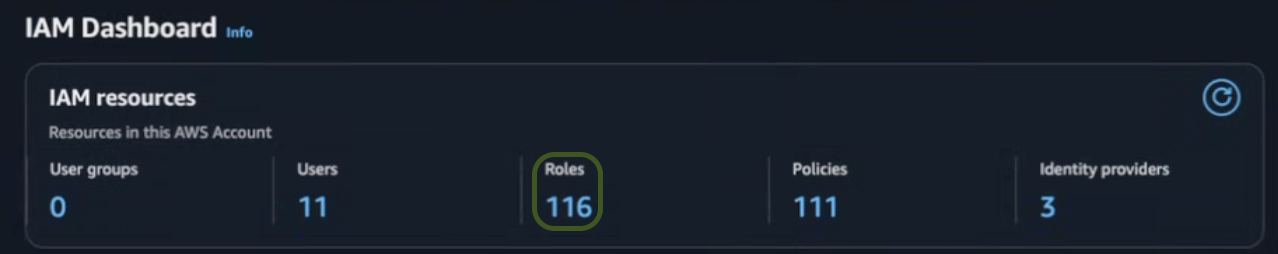
Click on IAM resources → Roles.
-
Click Create role in the top right corner.

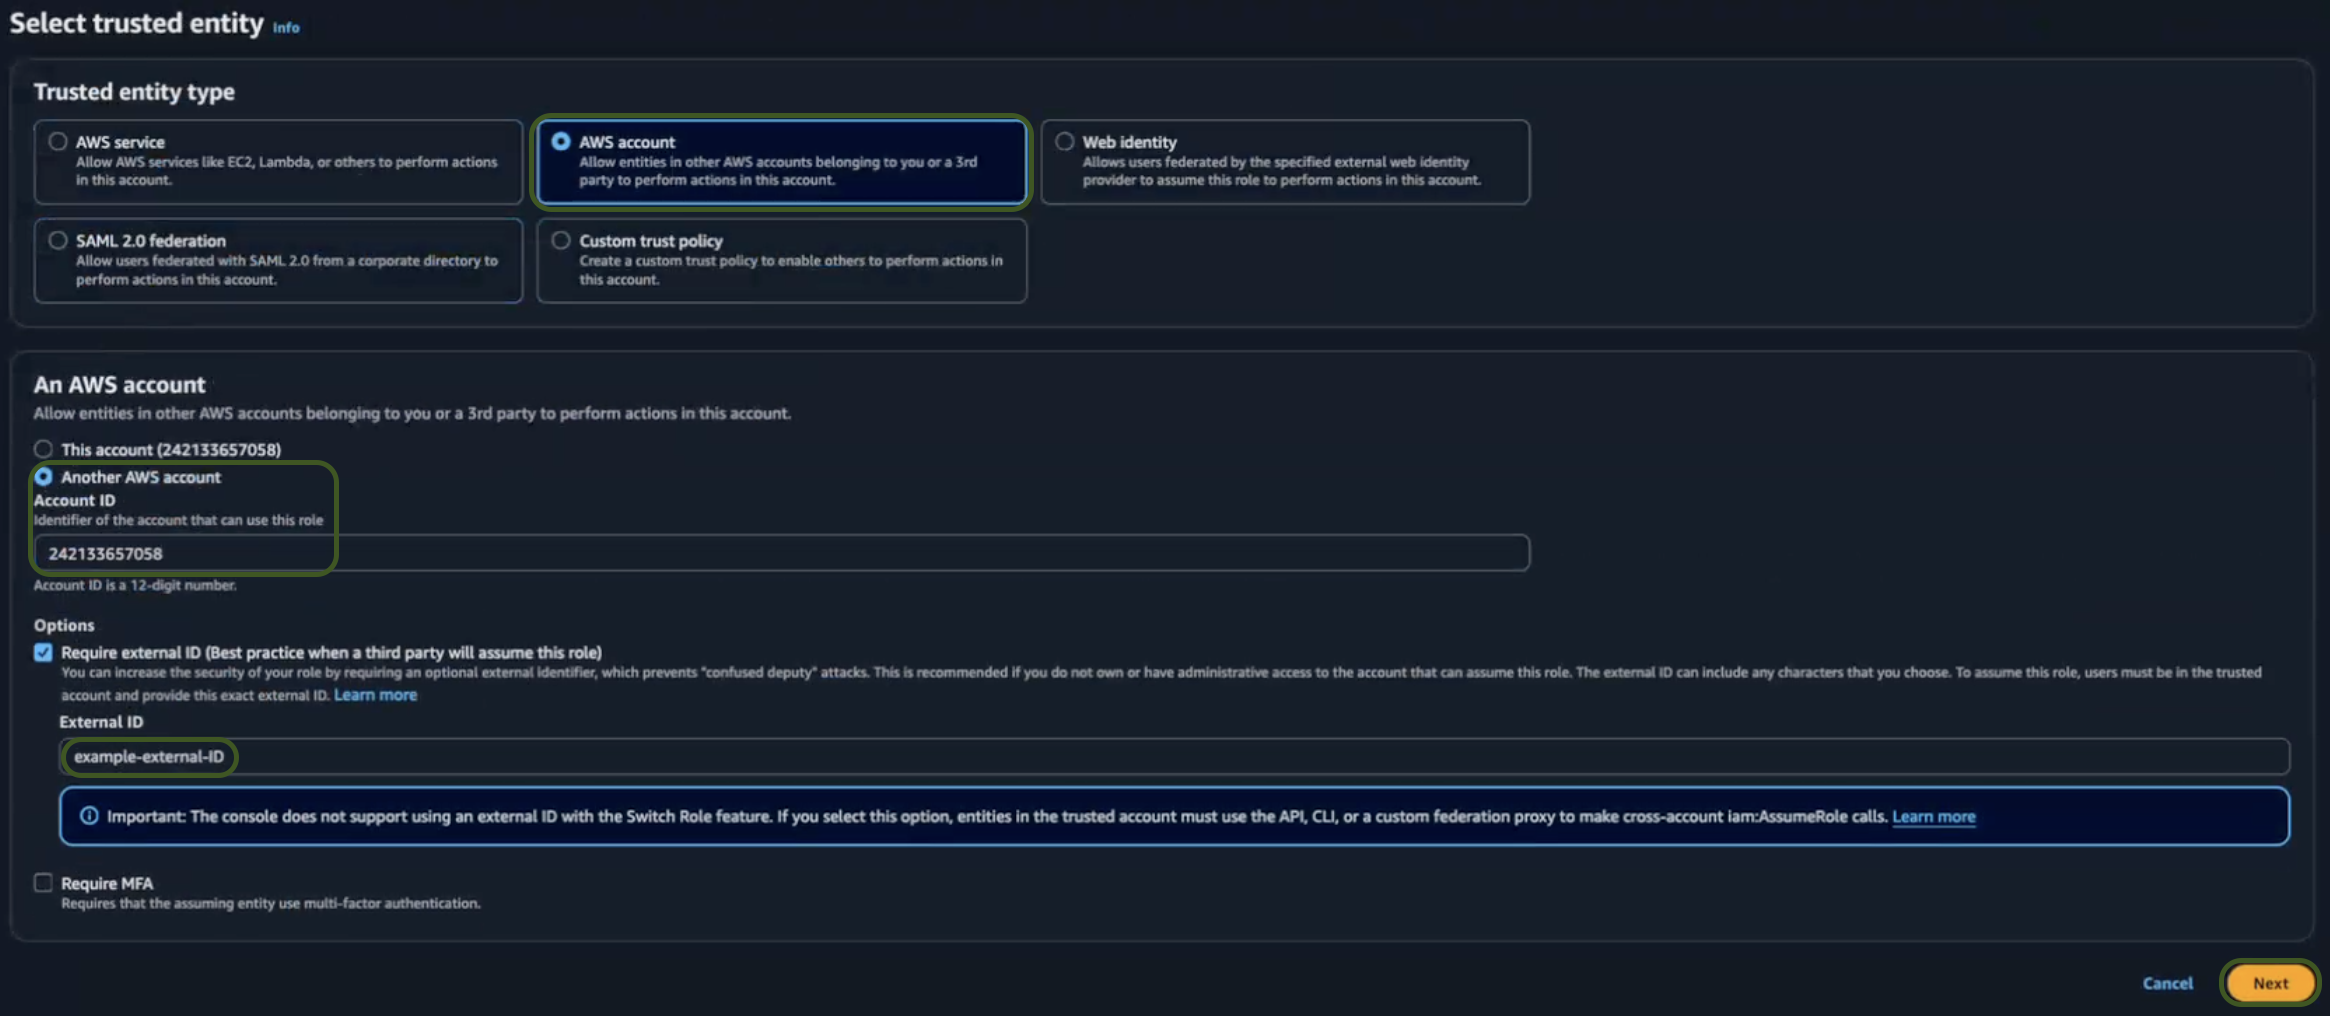
- In Select a trusted entity → Trusted entity type, choose AWS account.
- In the An AWS account section, choose Another AWS account.
-
Enter the AirMDR AWS Account ID: 242133657058 only as an identifier of the account that can use this role.
Generally, the Account ID is a 12-digit number. Use only the Account ID mentioned above.
- Select the Require external ID checkbox (best practice when a third party will assume this role).
-
Enter a unique, hard-to-guess value for the External ID, for example
airmdr-role-2026-5c1e8b7f42d9a036. AirMDR treats it as a secret. -
Click Next.
-
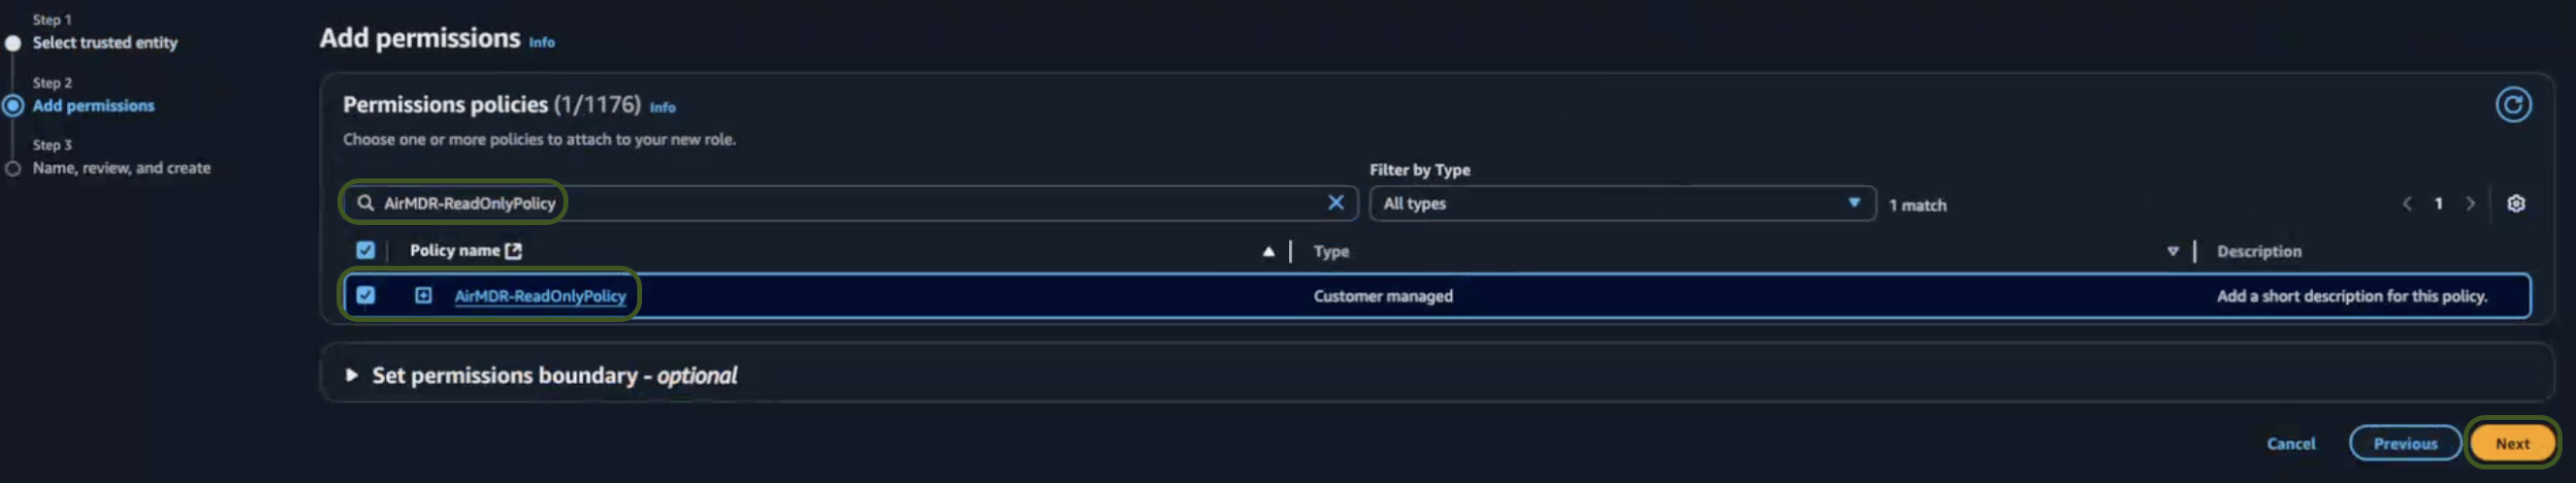
In the Add permissions section, search for and select
AirMDR-ReadOnlyPolicy.See Create IAM policy for detailed steps to defineAirMDR-ReadOnlyPolicyin IAM. -
Click Next.
-
In the Name, review and create section:
-
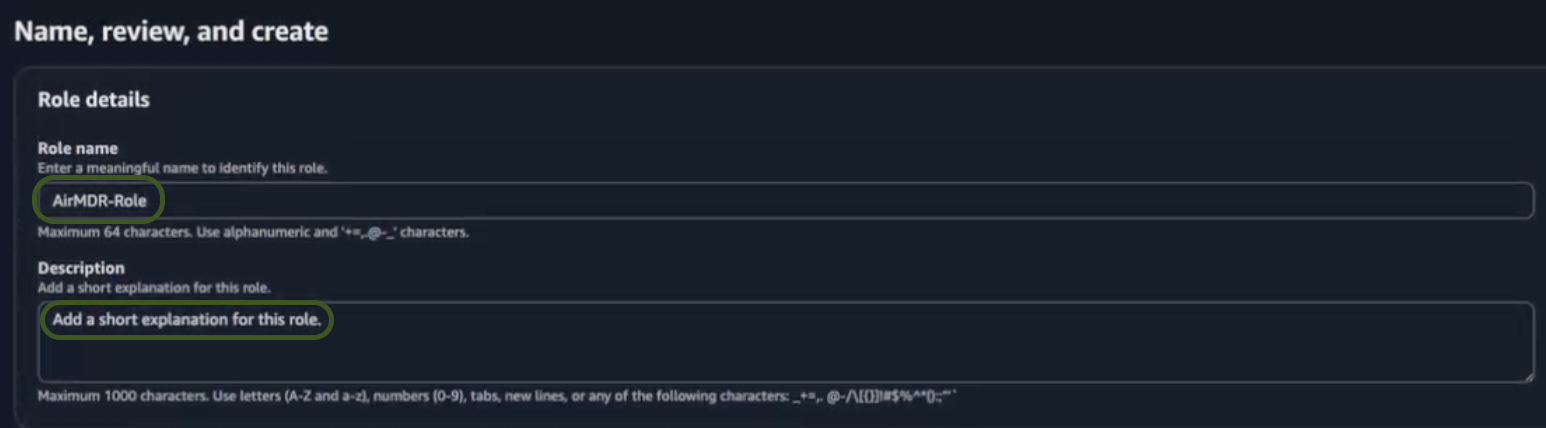
Provide the Role details:
- Role Name – Provide a meaningful name like
AirMDR-Role. - Description (Optional) – Add a short description for this role.
- Role Name – Provide a meaningful name like
-
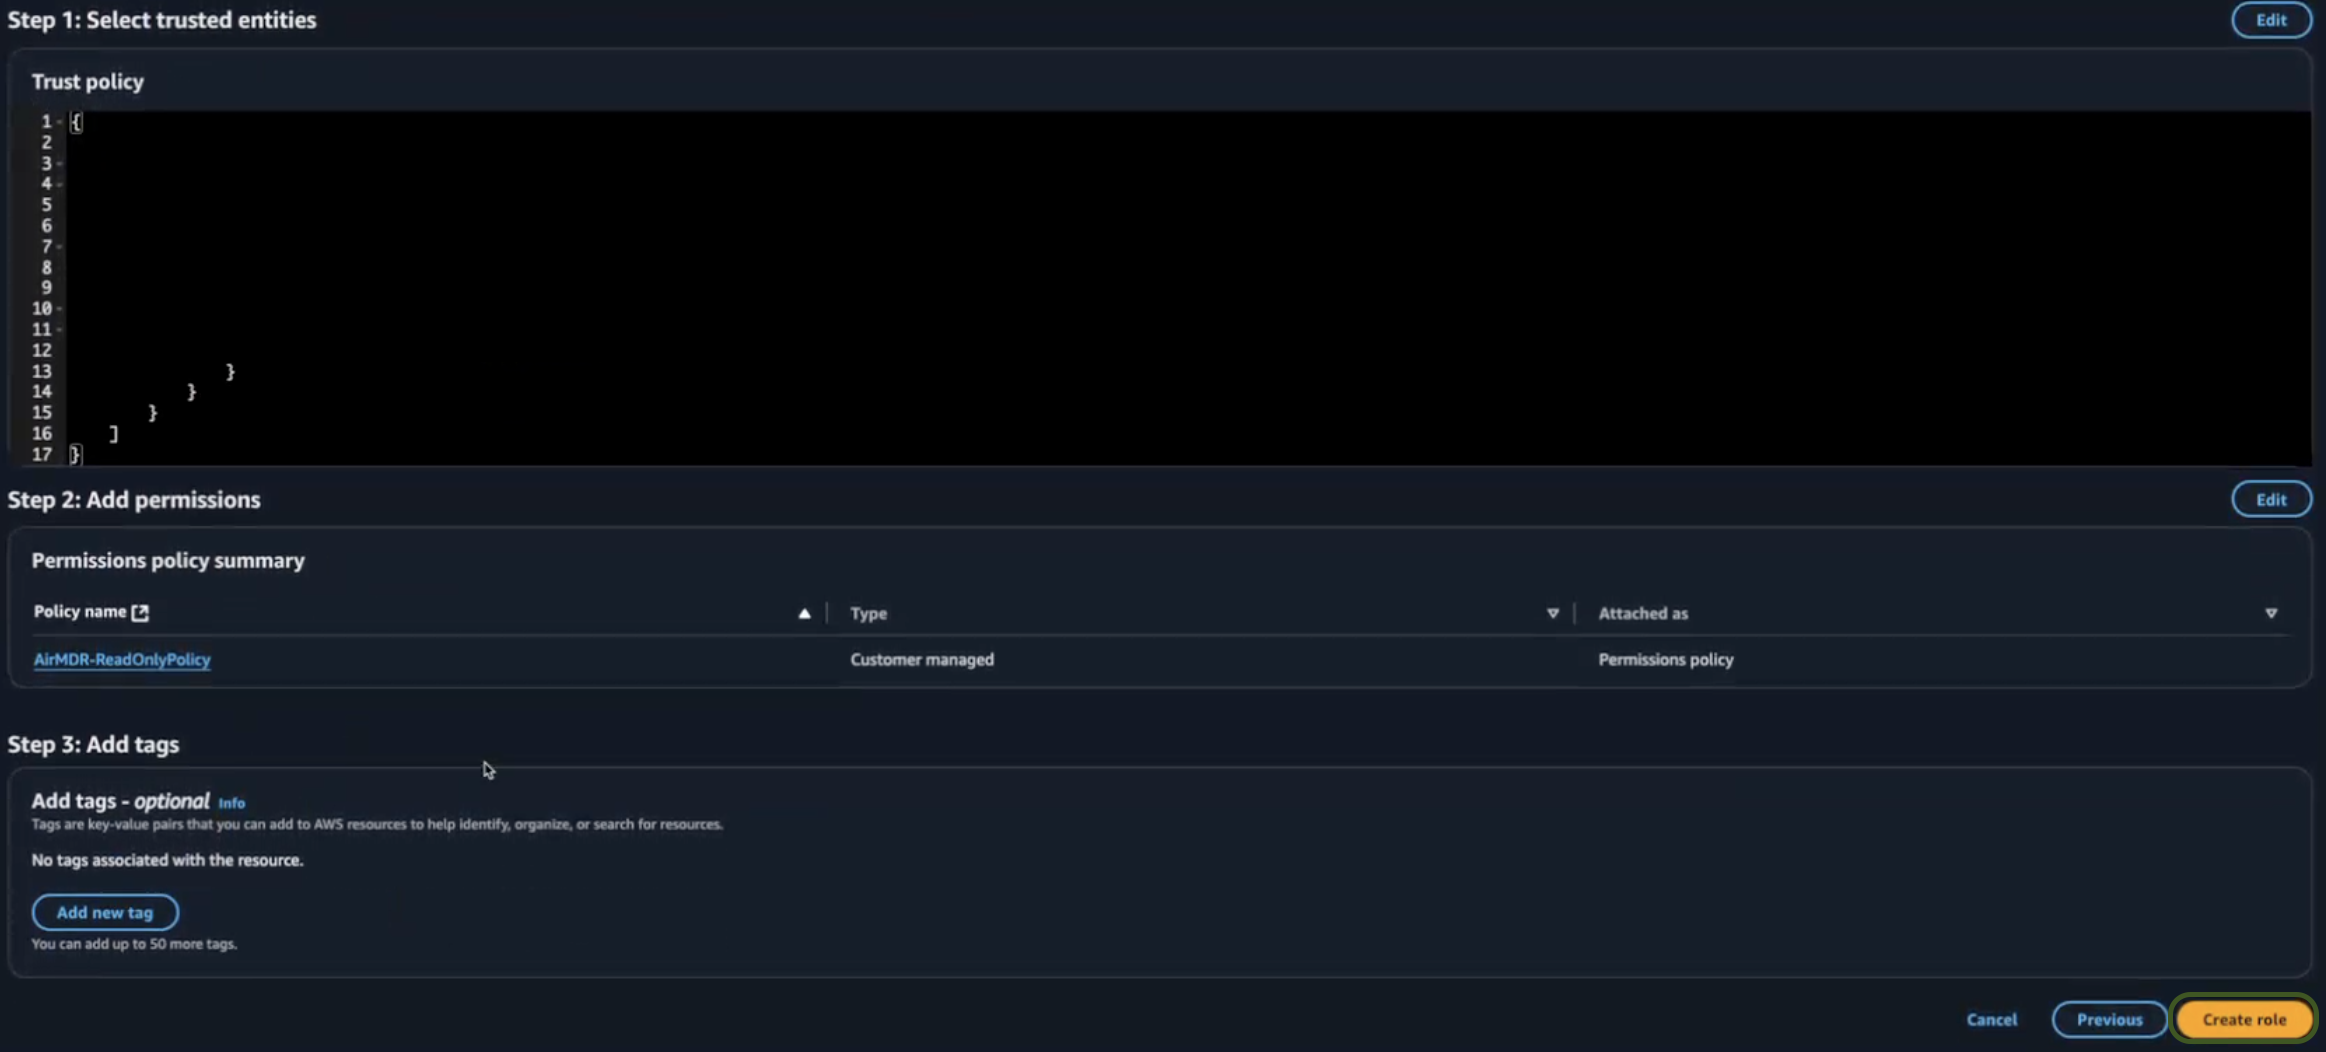
Review your selections and confirm they are correct.
- Permissions –
AirMDR-ReadOnlyPolicyis attached. - Trust policy – the principal is
arn:aws:iam::242133657058:root, with ansts:ExternalIdcondition matching the external ID you entered.
- Permissions –
- Click Create role.
-
Provide the Role details:
-
Open the role you just created (e.g.,
AirMDR-Role). -
Copy and securely save:
- ✅ Role ARN (Amazon Resource Name)
- ✅ External ID (entered earlier)
- Click Done.
Option 3: Multi-Account Integration using AWS StackSet Method
For organizations managing multiple accounts under an AWS Organization, AirMDR supports StackSet-style delegated access via a root account.Connect every account in an AWS Organization
Connect every account in an AWS Organization
How the access chain works
Read this before you start — it determines what you put in each trust policy.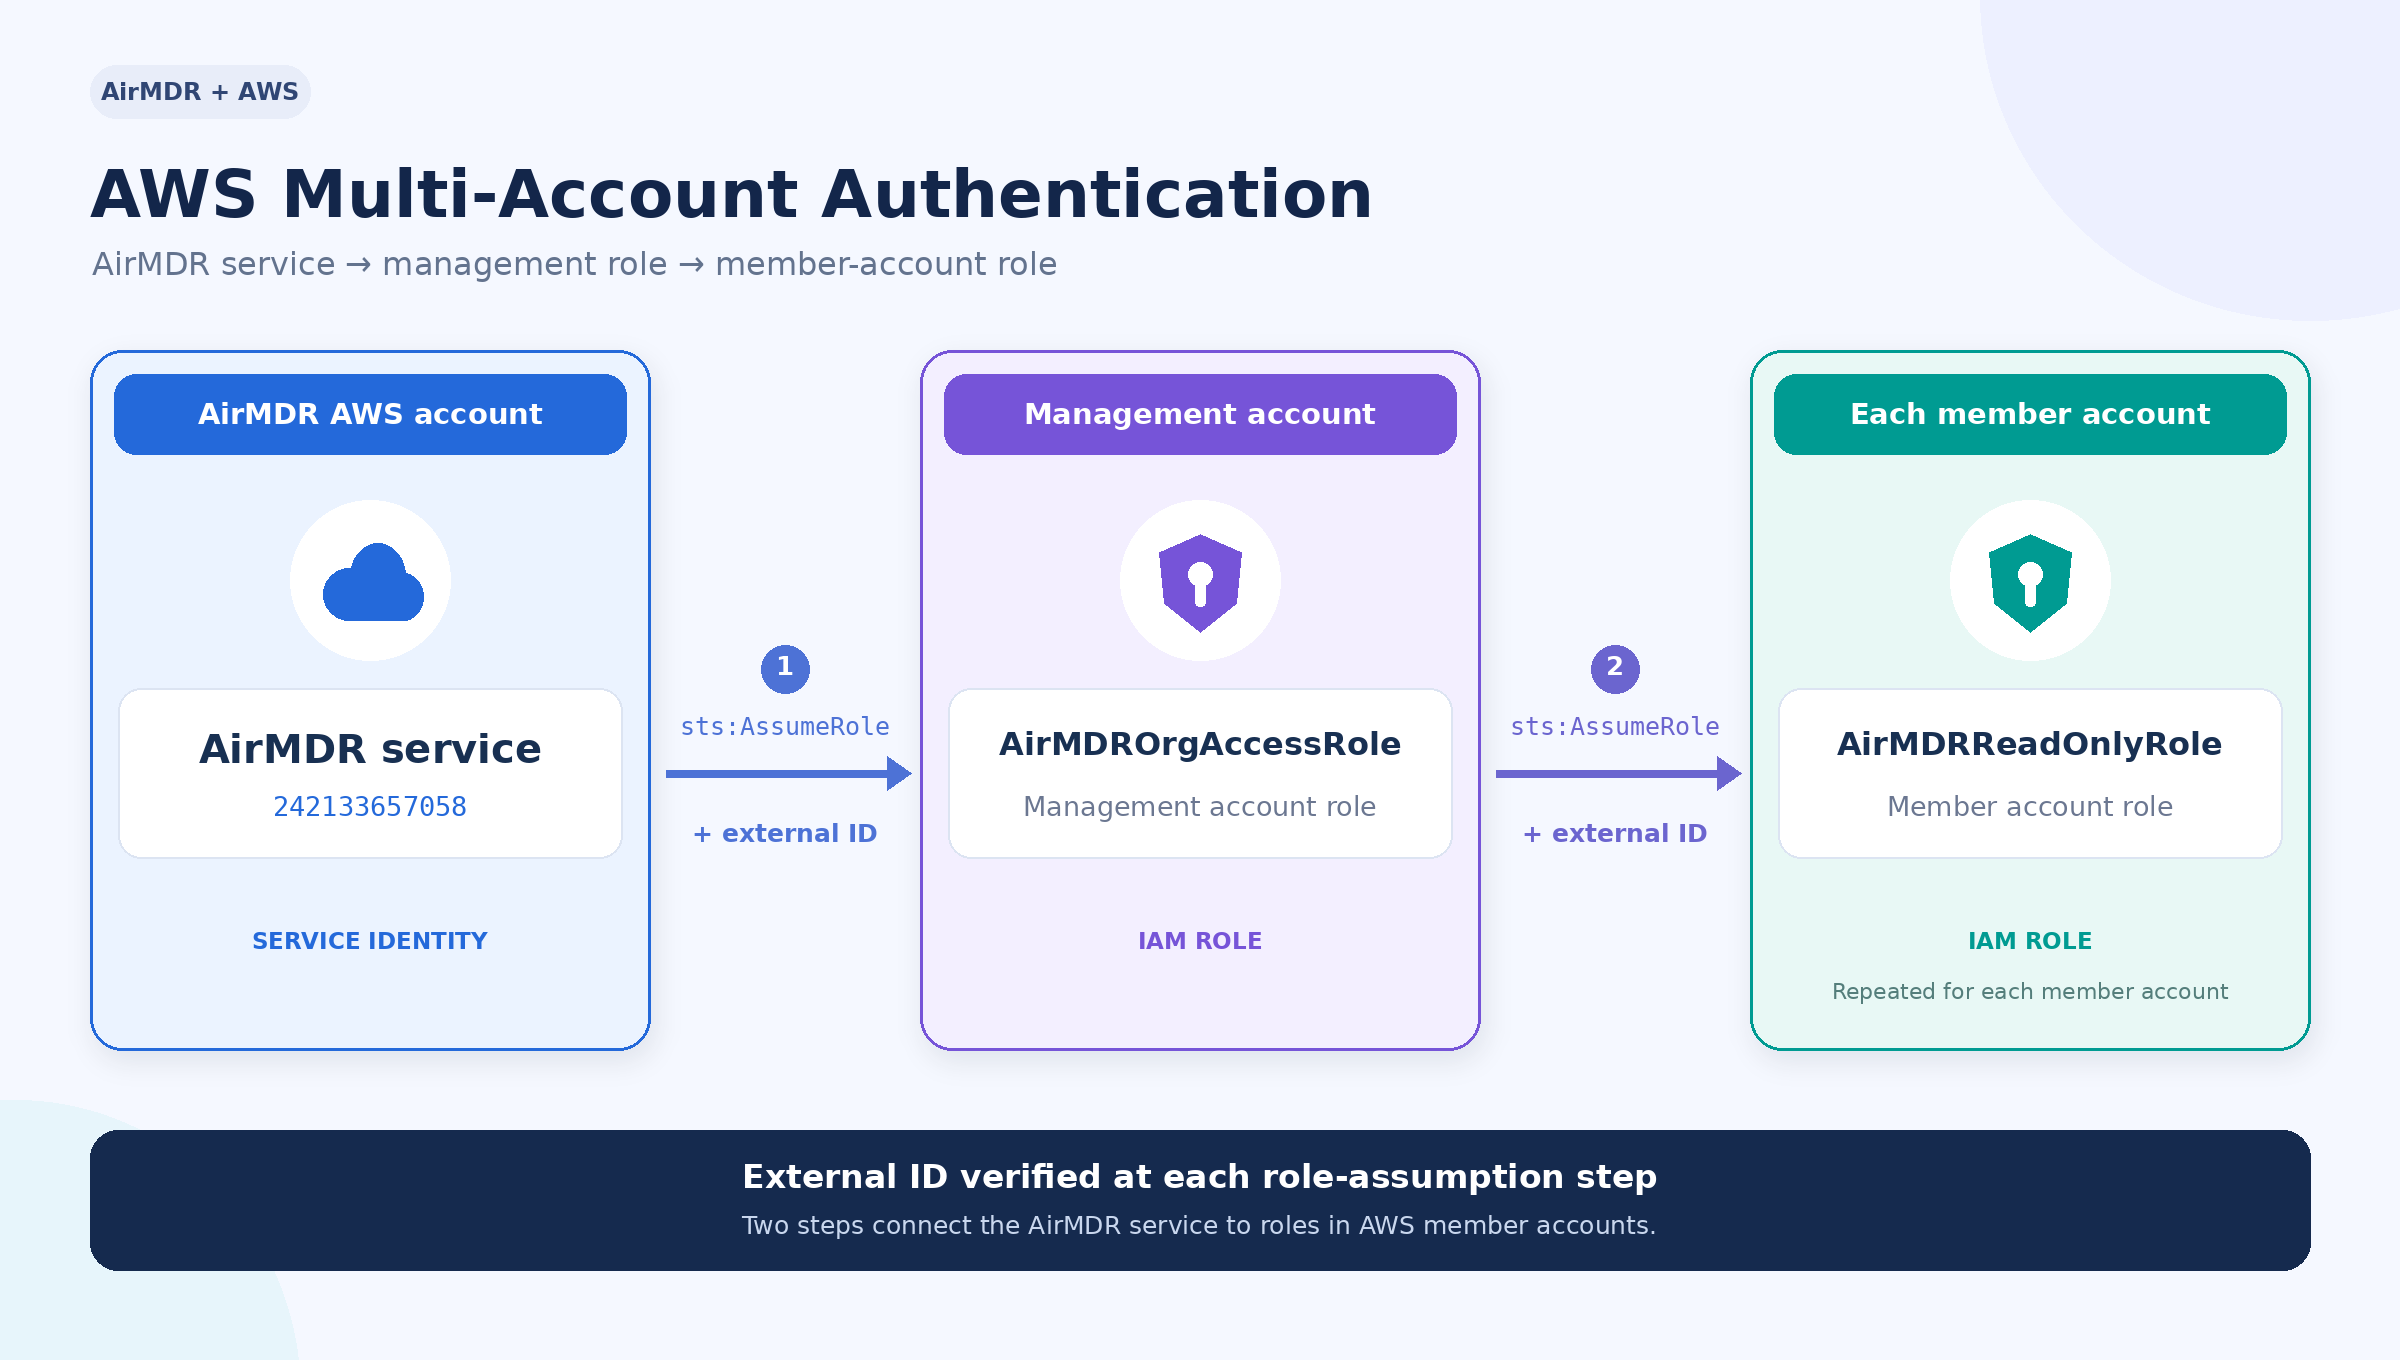
242133657058 — as the earlier template did — the second hop is denied, because the principal making that call is AirMDROrgAccessRole, not AirMDR’s account. It is the single most common setup mistake, so when you fill in TrustedAccountId in Step 2, put your management account ID there, not AirMDR’s.
Already deployed the old template, where the member role trusts 242133657058 directly? It keeps working — AirMDR detects that topology and assumes accordingly.
Step 1. Create the management account role
Sign in to the management (root) account of your organization.- Go to IAM → Roles → Create role.
- Trusted entity type: AWS account.
- Select Another AWS account and enter account ID
242133657058. - Tick Require external ID and enter a unique string. Save it — this is your
root_account_external_id. - Attach the managed policy
AWSOrganizationsReadOnlyAccess. - Name the role
AirMDROrgAccessRoleand create it.
+ = , . @ : / -. Use something unguessable, for example airmdr-orgaccess-2026-a7f3c9e21b8d4f60.Step 1b. Add the inline policies
AWSOrganizationsReadOnlyAccess alone is not enough. It grants only organizations:Describe* and organizations:List*, with no sts:AssumeRole, so the role cannot reach a single member account.Open the role → Add permissions → Create inline policy → JSON. Policy 1 is required; Policy 2 is optional.Policy 1 — AirMDRAssumeMemberRoles (required). Lets the role make the second hop:RoleName in Step 2, match it here.Policy 2 — AirMDRManagementAccountRead (optional). Needed only if AirMDR should read data in the management account itself. The StackSet does not deploy into the management account, so that account is read through this role directly, and without this policy every such read returns AccessDenied.Everything else works without it: Authenticate, enumerating the organization’s accounts, and every read in a member account. Many organizations keep workloads out of the management account, as AWS recommends, and can skip this policy. If you skip it:- Run single-account skills with an explicit member
account_id. Withaccount_idomitted they default to the management account and fail. - Fan-out skills still return every member account, but the management account’s slice errors. Lookup AWS CloudTrail Events and the CloudWatch skills report it as
status: "error"; Get AWS Guard Duty Findings drops it silently. - General AWS Query needs an explicit member
account_id. It stops at the first account that errors, and the management account is always part of its sweep, so withoutaccount_idthe whole query fails.
Step 1c. Record three values
From the role’s summary page:root_account_id also tells AirMDR which account is the management account, so it can route reads there correctly instead of looking for a member role that does not exist.Step 2. Deploy the member role by StackSet
Still in the management account.- CloudFormation → StackSets → Create StackSet.
- Permissions model: Service-managed permissions.
- Prerequisite: Template is ready. Specify template: Upload a template file.
- Upload the YAML below.
+ = , . @ : / -.- StackSet name: e.g.
AirMDR-StackSet. - Parameters: set
TrustedAccountIdto your own management account ID andExternalIdVarto your chosen secret. LeaveRoleNameat its default unless you intend to rename the member role — if you change it, update theResourceARN in the Step 1bAirMDRAssumeMemberRolespolicy and thecross_account_role_namein Step 3 to match. - Configure options: Managed execution → Inactive. Tick the IAM capabilities acknowledgement.
- Deployment options:
- Add stacks to stack set → Deploy new stacks
- Deployment targets → Deploy to organization
- Automatic deployment → Activated (new accounts are covered automatically)
- Account removal behaviour → Delete stacks
- Specify regions → exactly one region. The template creates an IAM role, and IAM is global, so a second region’s stack would try to create the same role again and fail with
AlreadyExists. Which region you pick does not matter to AirMDR — the role works in every region. Picking the one your security data lives in keeps things tidy. - Region concurrency → Sequential; Concurrency mode → Strict failure tolerance
- Review → Submit, then wait for every stack instance to reach
CURRENT.
Write actions. This policy is read-only. Skills that change state in your account — archiving GuardDuty findings, updating Security Hub workflow status, writing or deleting S3 objects, revoking IAM role sessions — needguardduty:ArchiveFindings,securityhub:BatchUpdateFindings,s3:PutObject,s3:DeleteObjectandiam:PutRolePolicy. Athena additionally needsathena:StartQueryExecution,athena:GetQueryExecutionandathena:GetQueryResults. Add them as a second, clearly-labelled statement only if you want AirMDR to take those actions.
The permission set
The template’s two statements — the service reads and the S3 reads — are the complete set of read actions the built-in skills call. They are split so you can scope the S3 statement’sResource down from * to the specific bucket ARNs your investigations use, without touching the rest. That scoping is worth doing: it is the only statement that reaches object contents.If you add the optional AirMDRManagementAccountRead policy in Step 1b, it is the same two statements, so the management account gets the same reads as each member. If you scope the S3 statement in the template, scope it there too. Neither contains sts:AssumeRole — that grant lives separately in AirMDRAssumeMemberRoles, and only the management account role needs it.Two things the template deliberately leaves out:- General AWS Query calls whatever service and method a playbook names, so no fixed list can cover it. Add the actions your playbooks actually use —
ec2:DescribeInstancesands3:GetBucketPolicyare common starting points. - Athena needs
athena:StartQueryExecution,athena:GetQueryExecutionandathena:GetQueryResults, plus the source-data and result-location access described under IAM permissions reference.
Step 3. Create the connection in AirMDR
Follow Configure AWS in the AirMDR Integrations Dashboard, entering these values in Step 4 of the Do it Yourself tab. Leave Steps 2 and 3 blank — they are for the single-account methods.assume_role_in_root_account unset. AirMDR works out which trust topology your member roles use on the first assume and reuses that answer for the rest of the query. Pin it only if you want to skip that one-off detection — true for the template in this guide, false for the older one. A pinned value is obeyed exactly, so an incorrect pin produces AccessDenied rather than silently falling back.Step 4. Verify
Save the connection, then run Authenticate on it from the Connections tab. This runs the Verify Authentication skill, and a green result confirmsAirMDROrgAccessRole is assumable — and nothing more. It only calls sts:GetCallerIdentity, which any principal may call, so it cannot tell you whether the member roles work.Prove the second hop with a real query. Run Lookup AWS CloudTrail Events with no account_id. CloudTrail event history is on by default in every account, so this tests the access chain without depending on any other service being set up. Read AccountResults[] in the response — it has one entry per active account in the organization:- Every entry
status: "success"— the access chain works for every account. status: "error"withAccessDeniedonsts:AssumeRolefor every member — the member trust policy, the external ID, or the Step 1bsts:AssumeRolegrant is wrong.- The same error for some members only — the StackSet has not reached those accounts. Check its stack instances; accounts that joined after deployment are covered only if automatic deployment is on.
AccessDeniedon acloudtrail:action for the management account only — expected if you skipped the optional Step 1b Policy 2,AirMDRManagementAccountRead. Otherwise that policy is missing or incomplete.
account_id: an empty DetectorIds list means GuardDuty is not enabled there.Account coverage
Every skill that calls AWS accepts an optionalaccount_id input — a 12-digit member account ID — so any skill can be pointed at any account in the organization. What differs is the behaviour when you omit it.Fan out across every account when account_id is omitted: Get AWS Guard Duty Findings, Lookup AWS CloudTrail Events, Filter AWS CloudWatch Log Events, Get AWS CloudWatch Metrics, General AWS Query. They report per-account outcomes differently:account_id is omitted: every other skill — List Guardduty Detectors, List Guardduty Findings, List Cloudtrail Trails, List Cloudwatch Log Groups, Get AWS CloudWatch Log Events, all S3 skills, all Security Hub skills, Execute AWS Athena Query, and both IAM skills. Reading the management account this way needs the optional Step 1b Policy 2 on AirMDROrgAccessRole; without it they return AccessDenied. If you skipped that policy, always pass a member account_id to these skills.Configure AWS in the AirMDR Integrations Dashboard
- Navigate to AirMDR, provide the credentials, and click Login.
- In the left navigation pane, select Integrations.
- Search for “Amazon Web Services”, select the Connections tab, and click the + Create icon. The Add New Connection dialog opens.
-
Fill in the two fields at the top — both are required:
- Instance — a unique name for this connection (e.g.,
your org name-AWS), used to identify it when running skills. - Description — what this connection is for.
- Instance — a unique name for this connection (e.g.,
-
Stay on the Do it Yourself tab — for the scripted alternative see Quick setup with the Use a Script tab. Under Steps to provide credentials, complete only the numbered step that matches the method you set up, and leave the other two blank. The dialog capitalizes each field label (
Root_account_role_arn); the rest of this guide uses the lowercase parameter names (root_account_role_arn) for the same fields. -
In Step 5, enter Region_name — the AWS region this connection queries (e.g.,
us-east-1). This field is required. - Advanced Configuration (optional) — expand it to set a Remote Agent or an Expiry date for the credentials. Leave both unset unless your deployment requires them.
- Click Save.
- Back on the Connections tab, run Authenticate on the new connection to validate the credentials and authorize it.
region_name.Where to find the generated AWS Authentication Parameters in the Console (UI Steps)
Skills Provided by this Integration
The AWS integration provides skills to investigate security findings, query logs and metrics, access S3 objects, analyze historical data, and automate response actions. Each table below lists the IAM actions that skill requires. Grant them to the IAM user or role configured for the AirMDR connection, and restrict them to the smallest set of resources your workflows need. Permissions that depend on an optional feature are listed separately under IAM permissions reference.CloudTrail — Audit and Investigation
CloudTrail — Audit and Investigation
LookupEvents retrieves management and supported Insights events within the last 90 days in a region. It does not retrieve data events. Query older events or data events from a configured logging destination, such as CloudTrail logs stored in S3 through Athena.CloudWatch — Logs and Metrics
CloudWatch — Logs and Metrics
logs:DescribeLogStreams is required: the integration discovers log streams before retrieving events from them.GuardDuty — Threat Investigation and Response
GuardDuty — Threat Investigation and Response
Security Hub — Findings and Compliance
Security Hub — Findings and Compliance
GetFindings and GetFindingsV2 are separate APIs with separate IAM actions. Grant securityhub:GetFindings for the ASFF skill and securityhub:GetFindingsV2 for the OCSF skill; grant both if you use both. securityhub:ListFindings and securityhub:DescribeHub are not called by any skill.Amazon S3 — Object Management
Amazon S3 — Object Management
Athena — Historical Data Analysis
Athena — Historical Data Analysis
SELECT query writes query results.database_name and output_location. When database_name is omitted it queries the default database; when output_location is omitted it runs in the primary workgroup and writes results to that workgroup’s configured result location, so the workgroup must have one set.IAM — Permission Checks and Session Response
IAM — Permission Checks and Session Response
DateLessThan condition on aws:TokenIssueTime — the same mechanism as the console’s Revoke active sessions. Repeated runs refresh the same inline policy rather than adding new ones.Revocation does not deactivate IAM user access keys. It cannot edit IAM Identity Center permission-set roles or revoke service-linked role sessions. Restrict iam:PutRolePolicy to the intended target roles because it permits inline policy changes.General AWS Operations
General AWS Operations
account_id to isolate a failing account.IAM permissions reference
The per-skill actions are listed with each skill above. The tables below cover the extra permissions that apply only when a particular feature, encryption option, or data source is in use. AWS managed policies can provide broader access than a workflow requires; use these specific actions when defining a custom policy.Conditional permissions and dependencies
Conditional permissions and dependencies
s3:PutObjectAcl, s3:PutObjectTagging, s3:DeleteObjectVersion and the multipart actions are therefore not required for those two skills. Athena’s result location is different — see the Athena table below.Athena data-access dependencies
Athena data-access dependencies
SELECT query writes results. Other SQL operations, federated queries, and different catalog configurations can require additional permissions.