Supported Versions
Supported Versions
Authentication
Authentication
AirMDR authenticates with Abnormal Security using a bearer API token.When AirMDR makes an API request, the token is submitted in the following HTTP header:
Authorization: Bearer <API_TOKEN>Enter only the generated token in the AirMDR API Token field. Do not add the
Bearer prefix unless the AirMDR UI explicitly requests it.Required role
The user creating the token must be able to:- Access Settings → Integrations.
- Create and manage API tokens.
- Select the tenant associated with the token.
- Assign API endpoint permissions.
- Configure token expiration and IP safelisting, when applicable.
Token access requirements
Use Custom Access and grant only the endpoints required by the AirMDR skills that will use this connection.For example:Pre-requisites
Users must have Administrator access to the Abnormal Security UI with sufficient privileges to create an API key.Permission to create and access the Abnormal Security API keys settings.
Some endpoints require an additional Abnormal Security license. For example, access to the Cases API requires an Account Takeover Protection license.
Setup Steps
1
Generate the API Token in Abnormal Security
- Sign in to the Abnormal Security portal.
- From the navigation menu, select Settings & Configuration → Integrations.
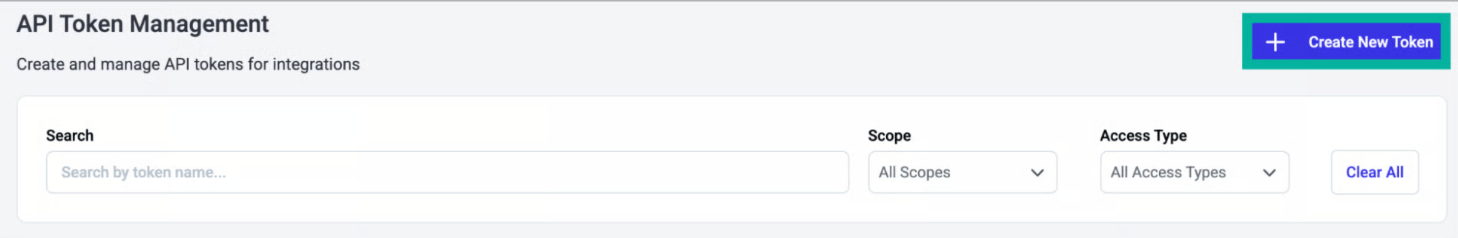
- Locate the API Token Management section.
- Click + Create New Token.
- For Integration Type, select REST API.
- Click Next.
- Continue with the applicable token-scope procedure, under Token Scope, select the appropriate scope.
- Option 1: Tenant (Single Tenant)
- Option 2: Customer (Multiple Tenants)
2
Option 1: Tenant (Single Tenant)
Use this scope when the AirMDR connection needs to access only one Abnormal Security tenant.
- Under Token Scope, select Tenant (Single Tenant).
- From the tenant list, select the organization that will connect to AirMDR.
- Click Next.
- Under Configure Access Type, select Custom Access.
- Select the API endpoints required by the supported AirMDR skills.
- Assign the minimum required access level to each selected endpoint. For example:
- Click Next.
- Continue to Configure the Token Details.
Access to some endpoints may depend on the Abnormal Security products licensed for the selected tenant. For example, the Cases API requires an Account Takeover Protection entitlement.
3
Option 2: Customer (Multiple Tenants)
Use this scope only when the AirMDR connection is intended to access multiple Abnormal Security tenants managed under the same customer or partner account.
- Under Token Scope, select the applicable customer-level option, such as Customer (All Current and Future Tenants).
- Select the customer account associated with the tenants that AirMDR must access.
- Review the scope carefully. If All Current and Future Tenants is selected, the token may also apply to tenants added to the customer account after the token is created.
- Click Next.
- Under Configure Access Type, select Custom Access.
- Select only the API endpoints required by the supported AirMDR skills.
- Assign the minimum required access level for each endpoint.
- Verify that the selected endpoint permissions are appropriate for every tenant covered by the token.
- Click Next.
- Continue to Configure the Token Details.
If different tenants require different permissions or access restrictions, create separate single-tenant tokens and AirMDR connections instead of using one broadly scoped customer token.
4
Configure the Token Details
Complete these steps after selecting either the single-tenant or multiple-tenant scope:
Navigation Path: Settings → Integrations → API Token Management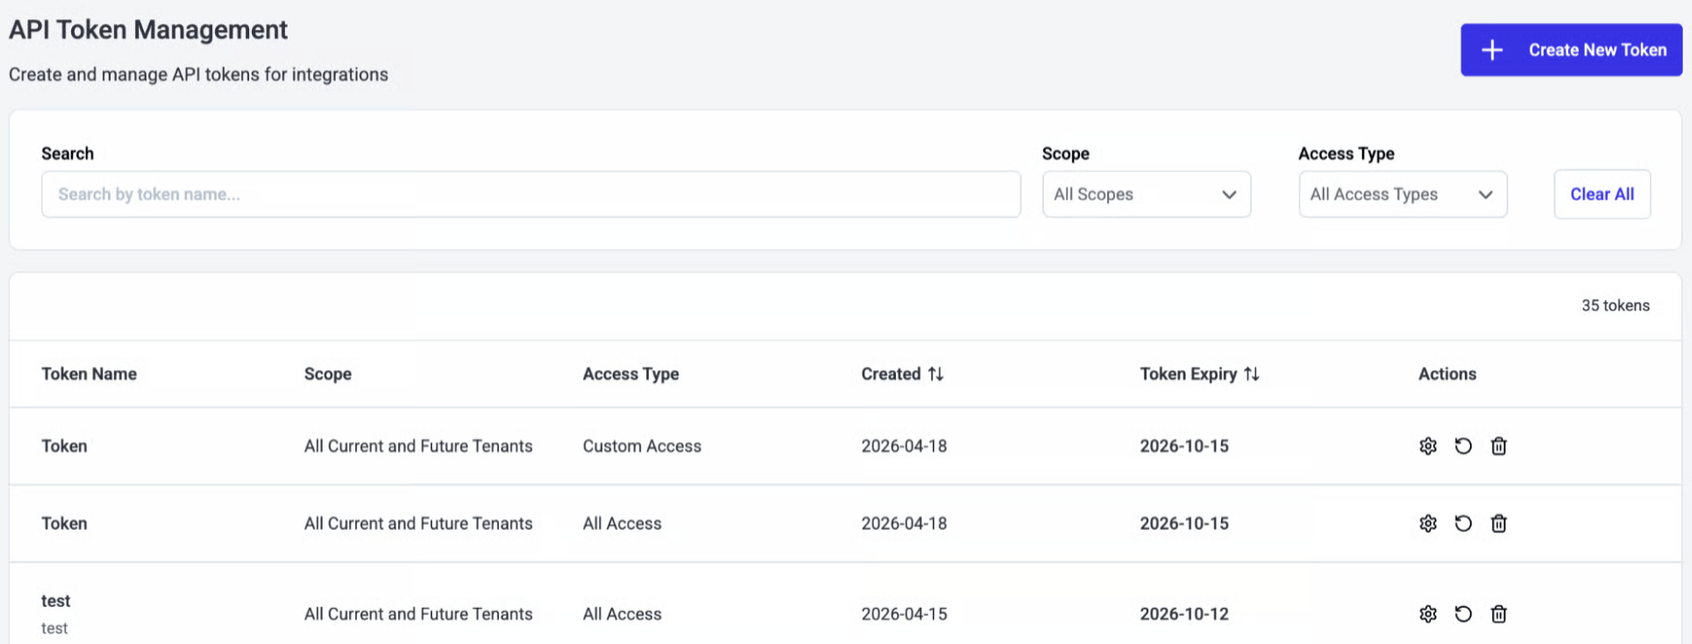
- Enter a recognizable Token Name.
Single-tenant example:AirMDR-Abnormal-Production-Tenant
Multiple-tenant example:AirMDR-Abnormal-Multi-Tenant - Enter a description that identifies the connection’s purpose and scope.
Example:Token used by AirMDR to execute approved Abnormal Security skills for the selected tenant scope. - Select a Token Expiration Period that complies with your organization’s credential-rotation policy.
- In IP Safelist, enter the approved AirMDR outbound IPv4 or IPv6 addresses or CIDR ranges.
Obtain the applicable outbound IP addresses from your AirMDR administrator or AirMDR Support. Requests may return
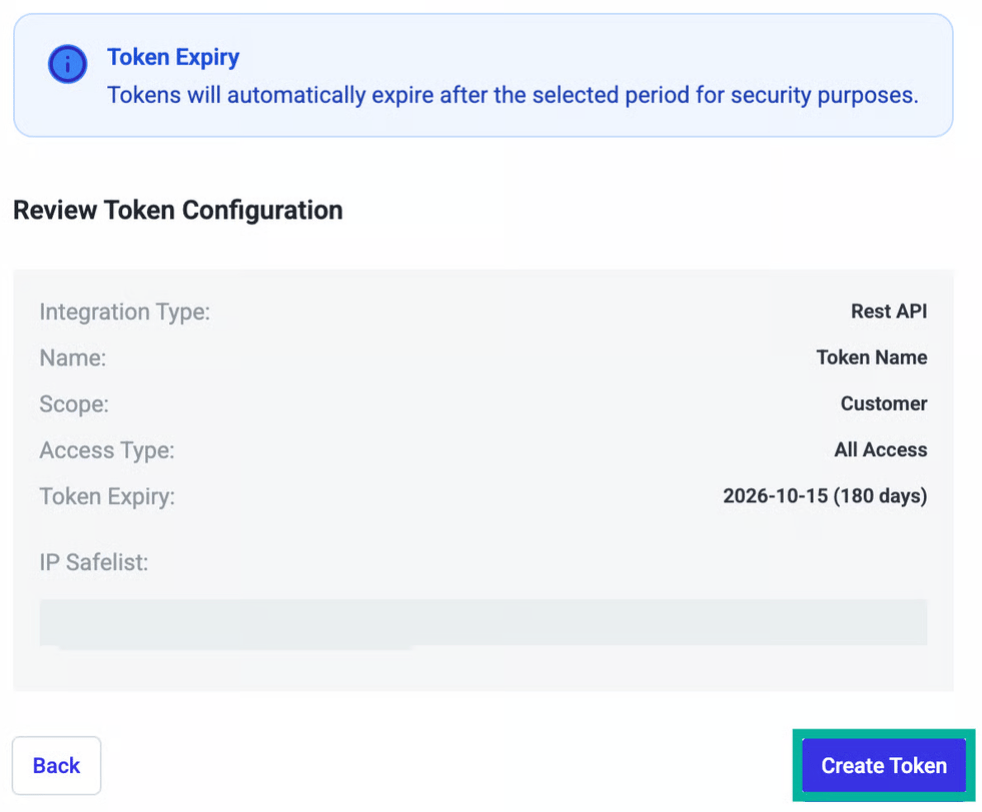
403 Forbiddenif the AirMDR outbound IP addresses are not included in the safelist. - Review the following token settings:
- Integration type
- Token scope
- Included tenants
- API endpoint permissions
- Expiration period
- IP safelist
- Click Create Token.
- Copy the generated API token immediately.
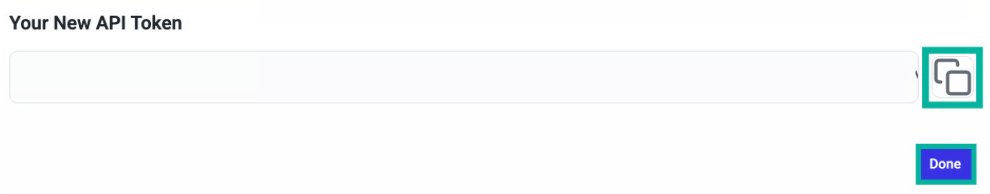
- Store the token in an approved secrets manager or encrypted credential vault and share it securely with AirMDR.
- Click Done.
If your tenant does not display API Token Management, navigate to Settings → Integrations → Additional Integrations → Abnormal REST API → Click Connect.
Configure the required access and IP safelist to generate and copy the token.
Manage, Rotate, and Revoke Tokens
On the API Token Management dashboard, you can search, filter, rotate, revoke, and edit existing tokens. Use the search bar to filter by token name, scope, or access type.Navigation Path: Settings → Integrations → API Token Management
Rotate and API Token
Rotate and API Token
Rotating a token generates a new token value and immediately invalidates the existing value. The token scope, access permissions, and IP safelist remain unchanged.To rotate an API token:
- Click the rotate icon (rotating arrow icon).
- Select a new token expiration date.
- Click Rotate Token.
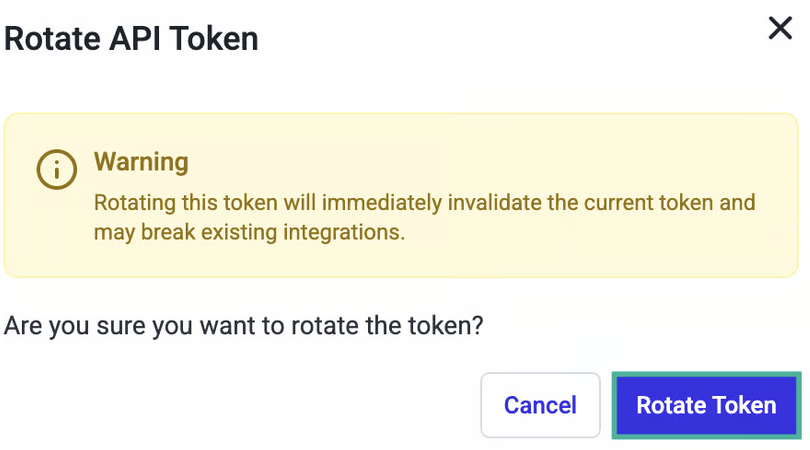
- Copy the newly generated token immediately and store it temporarily in an approved secure location.
- Return to the AirMDR connection.
- Replace the existing value in API Token with the new token.
- In Expiry, select the new Abnormal Security token expiration date.
- Click Save.
Edit Token
Edit Token
To edit an existing token:
- Click the cog wheel icon to open a Token Details page.
You can update any of the following:- Token name
- Description
- Safelisted IP addresses
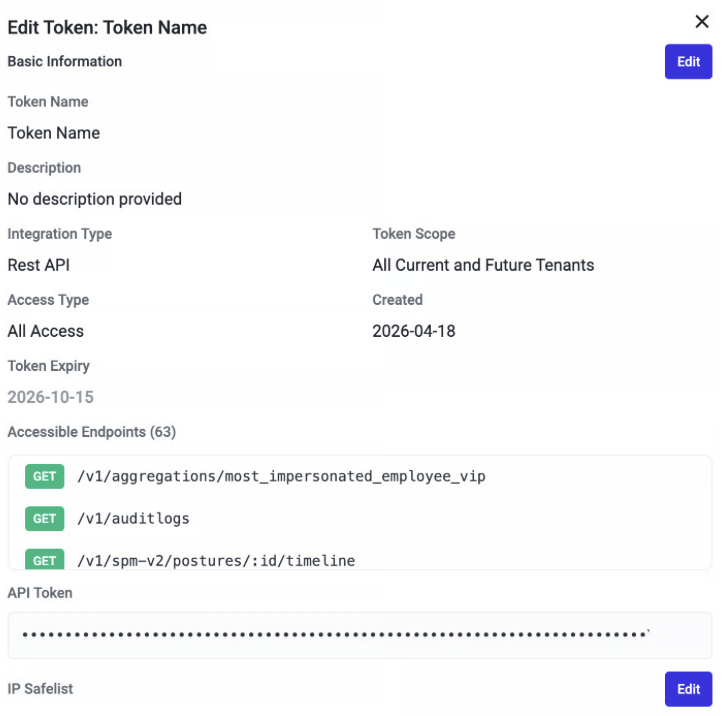
- Save the changes.
Revoke an API Token
Revoke an API Token
Revocation immediately and permanently invalidates a token. Unlike rotation, revocation does not generate a replacement token.Revoke a token when:
- The AirMDR connection is being decommissioned.
- The token is suspected to have been compromised.
- A policy change requires removing the granted access.
- A new token with a different scope or access level has replaced the existing token.
- A legacy token has been successfully replaced.
- Create a replacement token.
- Update the AirMDR connection with the replacement token.
- Update the Expiry field.
- Save and validate the connection.
- Revoke the previous token only after successful validation.
- Sign in to the Abnormal Security portal.
- Navigate to Settings → Integrations → API Token Management.
- Find the token that you want to revoke.
- Click the trash icon.
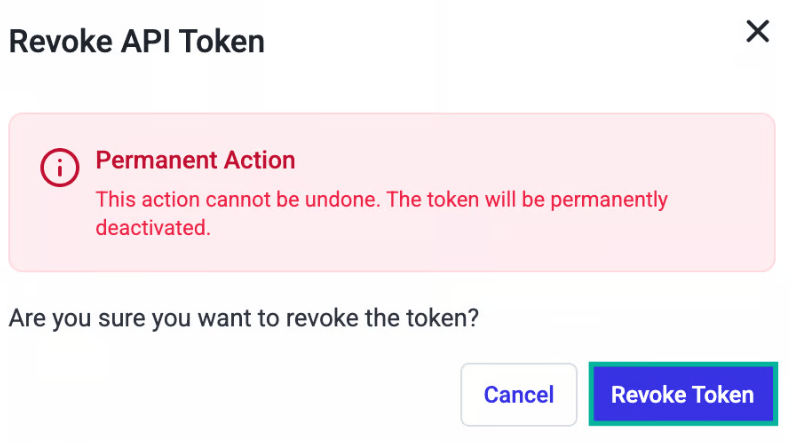
- Review the permanent-action warning.
- Click Revoke Token.
- Confirm that the revoked token is no longer used by any AirMDR connection or other integration.
5
Determine the Base URL
The Base URL is not generated with the token. Select it based on the region in which your Abnormal Security tenant is hosted.
Enter the Base URL only. Do not append an individual resource path such as
/threats or /cases.If you are unsure of the tenant region:
- Review your Abnormal Security onboarding information.
- Check the region associated with your tenant.
- Contact your Abnormal Security administrator or Abnormal Security Support.
Abnormal Security Credential Reference Table
Validate Connectivity
The following example retrieves threat information from the US API endpoint:Sample Request US Tenant
Sample Request US Tenant
Sample Request EU Tenant
Sample Request EU Tenant
curl —request GET \—url “https://eu.rest.abnormalsecurity.com/v1/threats” \—header “Authorization: Bearer <API_TOKEN>” \—header “Accept: application/json”
Sample Response
Sample Response
{“instance”: “Abnormal-Security-Production”,“base_url”: “https://api.abnormalplatform.com/v1”,“api_token”: “<stored-securely-in-airmdr>”}
Abnormal Security also documents a
Mock-Data: True header for testing supported requests without relying on production threat data.Run manual API tests only from an approved system. Do not expose the token in shared terminal history or logs.
Configure Abnormal Security in AirMDR Integrations Dashboard
- Navigate to AirMDR, provide the credentials and click Login
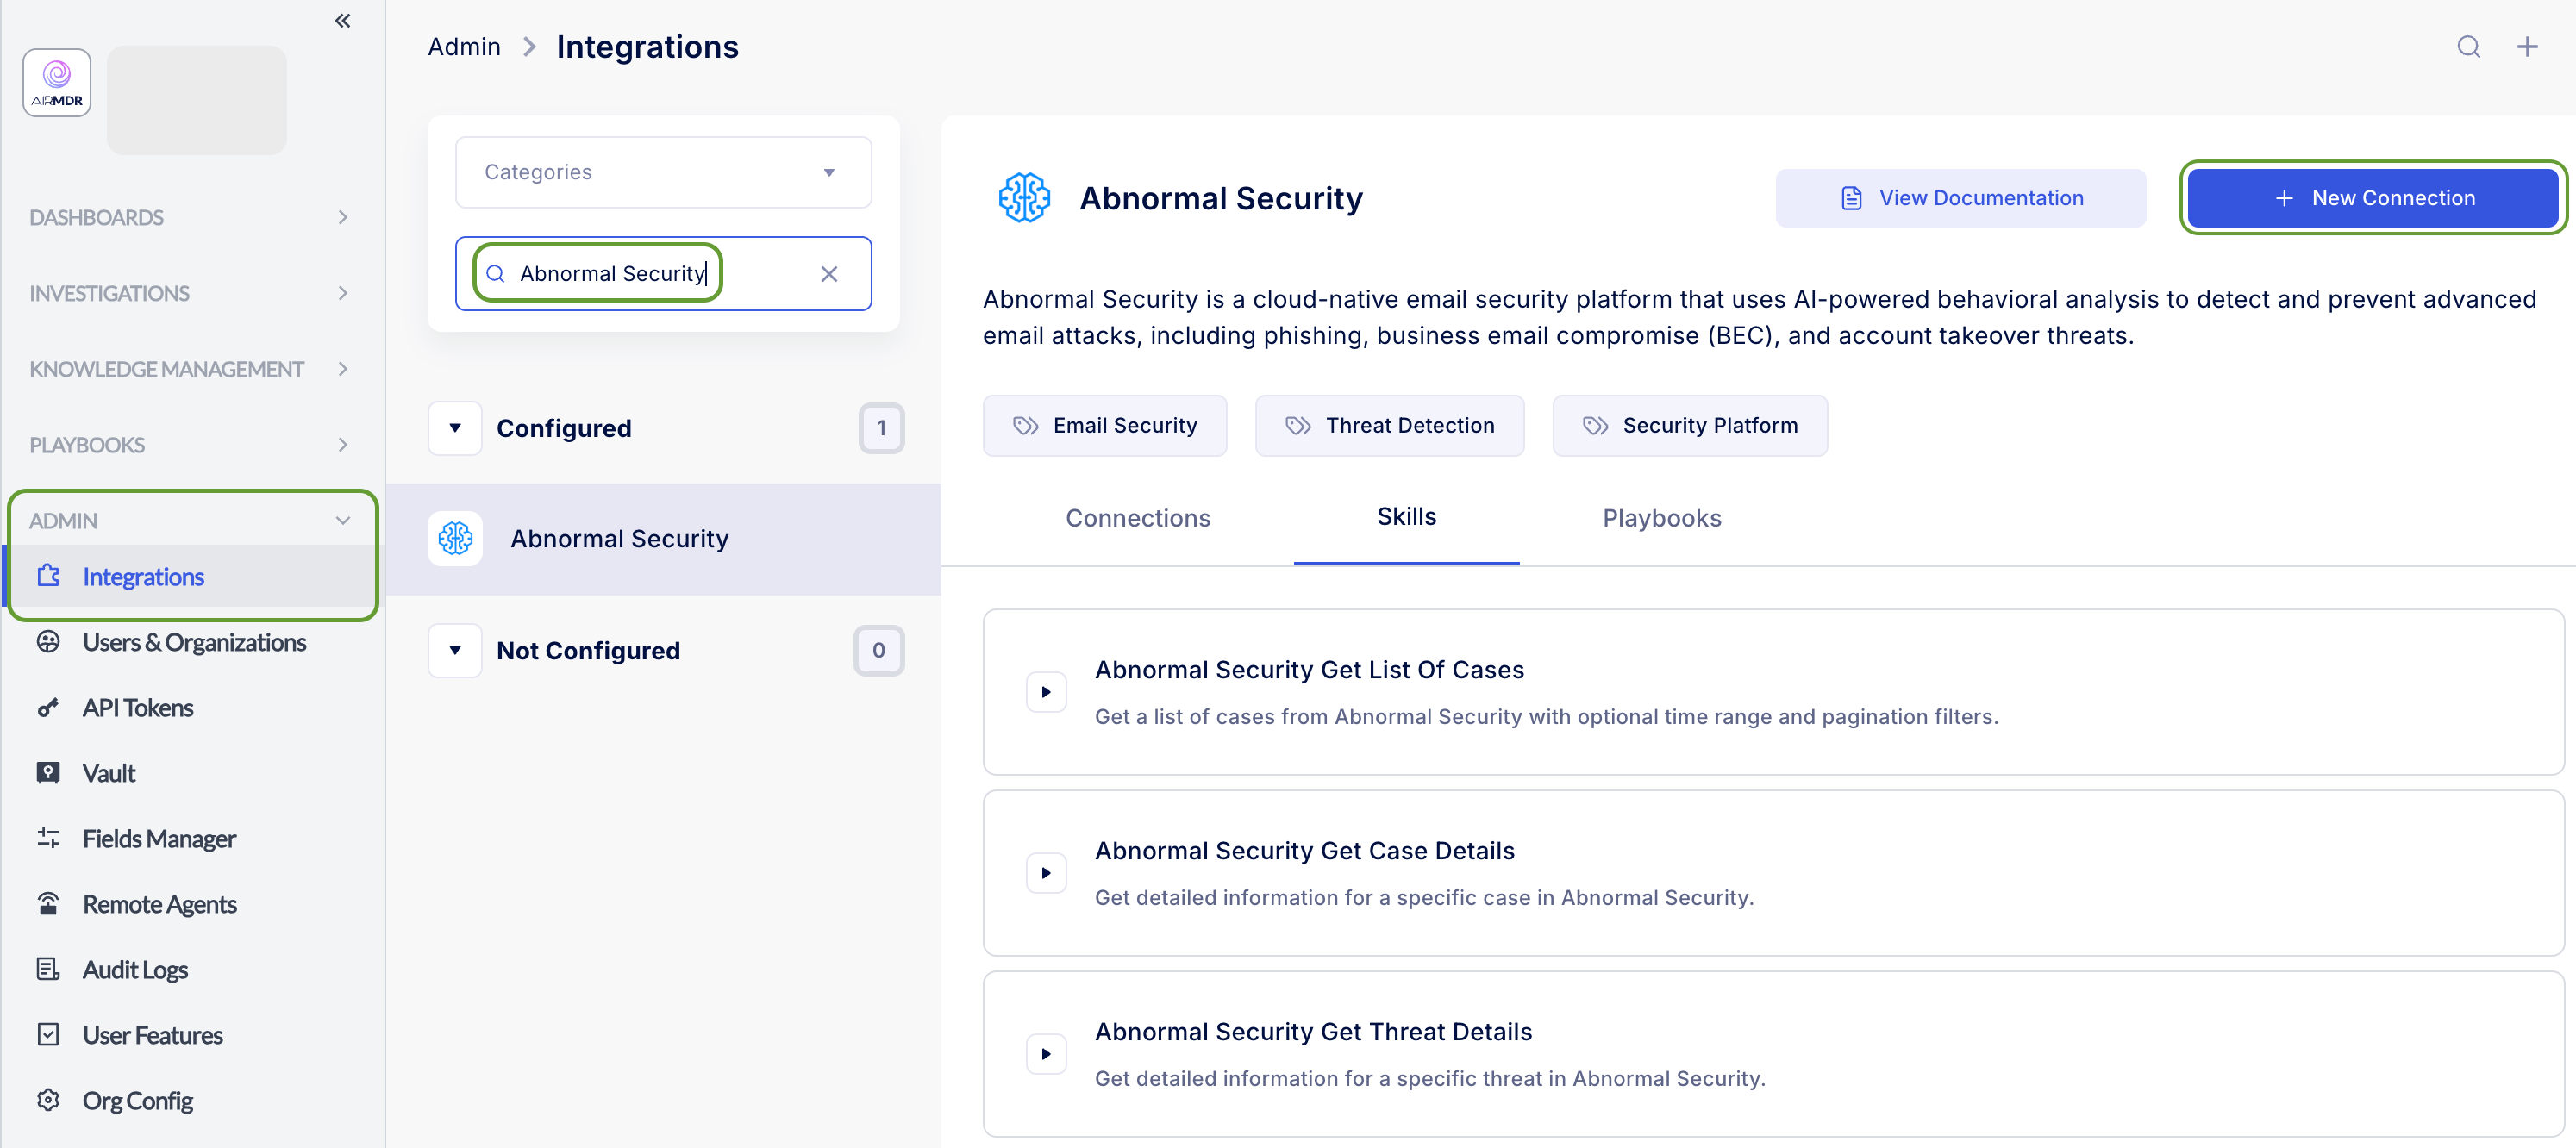
- Navigate to the AirMDR Integrations Dashboard in the left navigation pane and select ADMIN → Integrations.
- Use the search option, enter the keyword “Abnormal Security”, select the Connections tab, and click + New Connection button.
- Use the following values in the AirMDR integration configuration screen:
Enter only the token value in API Token. Do not include the
Bearerprefix. Enter the Base URL without appending endpoints such as/threatsor/cases.Expand Advanced Configuration if required. (Optional)
- In Remote Agent, leave the field unselected for a standard cloud connection. Select an AirMDR Remote Agent only when your organisation requires Abnormal Security API requests to pass through an approved private network route or a specific outbound IP address.
When using a Remote Agent, add the Remote Agent’s public outbound IP address to the IP Safelist configured for the Abnormal Security API token. Otherwise, Abnormal Security may reject requests with a
403 Forbiddenresponse. - In Expiry, select the date on which AirMDR should treat the stored connection credentials as expired, according to your organisation’s credential-rotation policy.
The AirMDR Expiry setting is a connection-management control. It does not automatically configure or rotate the API key in Abnormal Security.
- In Remote Agent, leave the field unselected for a standard cloud connection. Select an AirMDR Remote Agent only when your organisation requires Abnormal Security API requests to pass through an approved private network route or a specific outbound IP address.
- Click Save.
Skills provided by this Integration
Case Investigation
Case Investigation
Case-related skills may require the applicable Abnormal Security product entitlement. Confirm that the selected tenant supports the Cases API.
Threat Investigation
Threat Investigation
Additional Information
🧰 Error Handling
🧰 Error Handling
🔄 Monitoring & Logs
🔄 Monitoring & Logs
AirMDR monitoring
Monitor:- Connection status.
- Skill-execution status.
- Playbook execution history.
- Authentication and authorization failures.
- API timeouts and network errors.
- Connection instance used by the skill.
- Execution timestamp.
- HTTP status code.
- Requested operation.
- Error response, excluding credentials.
Abnormal Security monitoring
In Abnormal Security:- Navigate to Settings > Integrations.
- Open API Token Management.
- Confirm that the AirMDR token is active.
- Verify its expiration date.
- Confirm the selected tenant and endpoint access.
- Verify the IP safelist.
- Rotate or revoke the token if suspicious usage is detected.
Example sanitized log entries
Successful request:🛑 Security & Access Best Practices
🛑 Security & Access Best Practices
✅ Do
- Use Custom Access and assign the minimum endpoint permissions required.
- Use a dedicated token for the AirMDR integration.
- Configure an expiration period.
- Safelist only approved AirMDR outbound IP addresses.
- Store the token in the AirMDR credential field or an approved secrets manager.
- Rotate the token according to your organization’s credential policy.
- Use separate read-only and response-action tokens when operational separation is required.
- Revoke unused, expired, or potentially compromised tokens.
- Verify the tenant region before entering the Base URL.
❌ Don’t
- Granting full access when read-only access is sufficient.
- Reusing a personal or unrelated integration token.
- Adding
/threats,/cases, or another resource path to the Base URL. - Entering the EU Base URL for a US tenant, or vice versa.
- Including
Bearerin the AirMDR token field unless explicitly required. - Sharing the token through email, chat, documentation, screenshots, or tickets.
- Logging the token or Authorization header.
- Disabling certificate validation.
👉 Support & Maintenance
👉 Support & Maintenance
- 📧 Contact AirMDR Support through your designated support channel.
- 🔁 Rotate credentials regularly. Recommended cadence: As per your internal security policy
- 🔄 Reconnect with AirMDR immediately when secrets are changed.
🛑 Data Flow & Security
🛑 Data Flow & Security
Data flow
- An AirMDR playbook or analyst initiates an Abnormal Security skill.
- AirMDR retrieves the stored connection credentials.
- AirMDR sends an HTTPS request to the configured regional Base URL.
- Abnormal Security validates the API token, endpoint permission, token scope, expiration, and IP safelist.
- Abnormal Security returns the permitted response.
- AirMDR makes the results available to the playbook or analyst.
Data exchanged
The data exchanged depends on the skill and permissions assigned to the token. It may include:- Threat identifiers and threat details.
- Sender and recipient information.
- Attack type and remediation status.
- Message and attachment metadata.
- Case information and status.
- Employee or user information.
- Action identifiers and action-status information.
Network and encryption
All network communication must use the HTTPS endpoint. Do not replace
https:// with http://.